
How Entra Access Packages Can Create Privilege-Escalation Risks
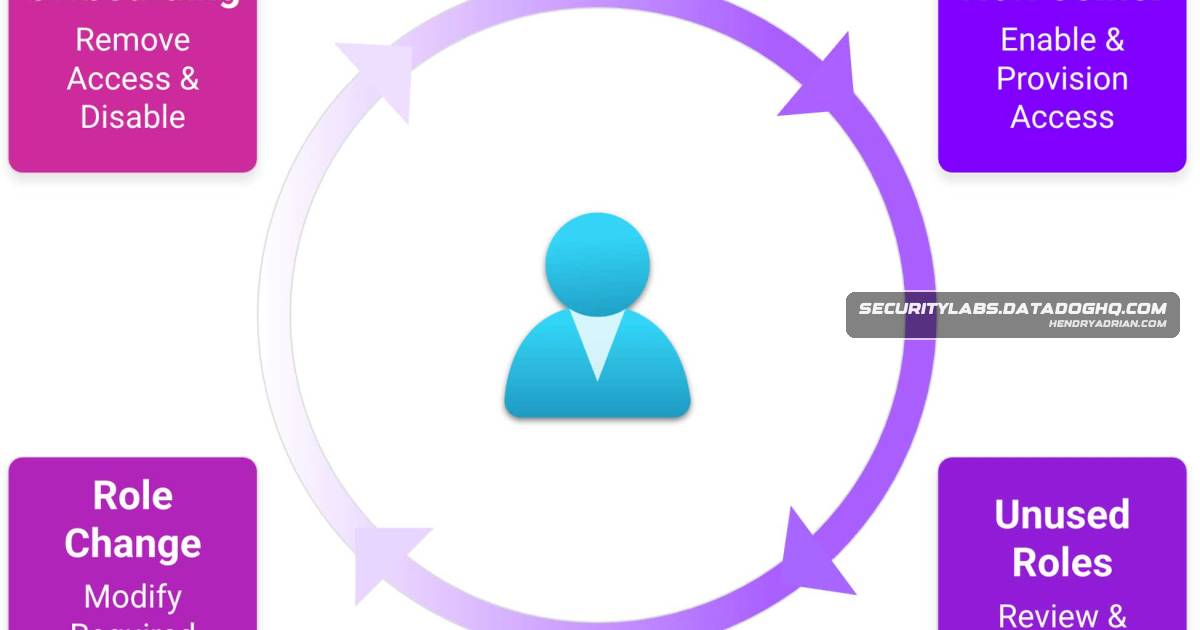
Summary
Datadog explains how Microsoft Entra ID Governance access packages bundle permissions and can expose privilege-escalation paths through role-assignable groups, non-Entra roles, governance roles and application permissions; it recommends auditing both Entra and IDGovern
Key points
- Entra entitlement management bundles group memberships, application roles, Azure roles and other resources into access packages governed by request and approval policies.
- Although access packages cannot directly assign privileged Entra roles, they can include role-assignable groups that grant those roles and roles such as Exchange Administrator.
- Global Administrator, Identity Governance Administrator, certain custom Entra roles and the Catalog Owner role can control aspects of entitlement management.
- Auditors need to review both Entra role assignments and ID Governance role assignments, including assignments at the individual catalog level.
- The Microsoft Graph EntitlementManagement.ReadWrite.All application permission can give service principals full management access.
- An attacker controlling entitlement management could target package eligibility, create packages using resources in a catalog they control, or tamper with group memberships.
Article Details
- Topic
- Technical overview of Microsoft Entra ID Governance entitlement management, access package configuration, role assignments, and potential privilege escalation risks.
Vendors
Products
Microsoft Entra IDThis post provides technical background about entitlement management and access packages in Microsoft Entra ID Governance.Microsoft Entra ID GovernanceThis post provides technical background about entitlement management and access packages in Microsoft Entra ID Governance.Microsoft GraphID and ID Governance, application permissions—specifically, the EntitlementManagement.ReadWrite.All Microsoft Graph permission—can grant SPs full management access to entitlement management.PIMEntitlement management versus PIM