
Binance Details Fake-Interview Attack Behind $6.34B in Affected Crypto Assets
Summary
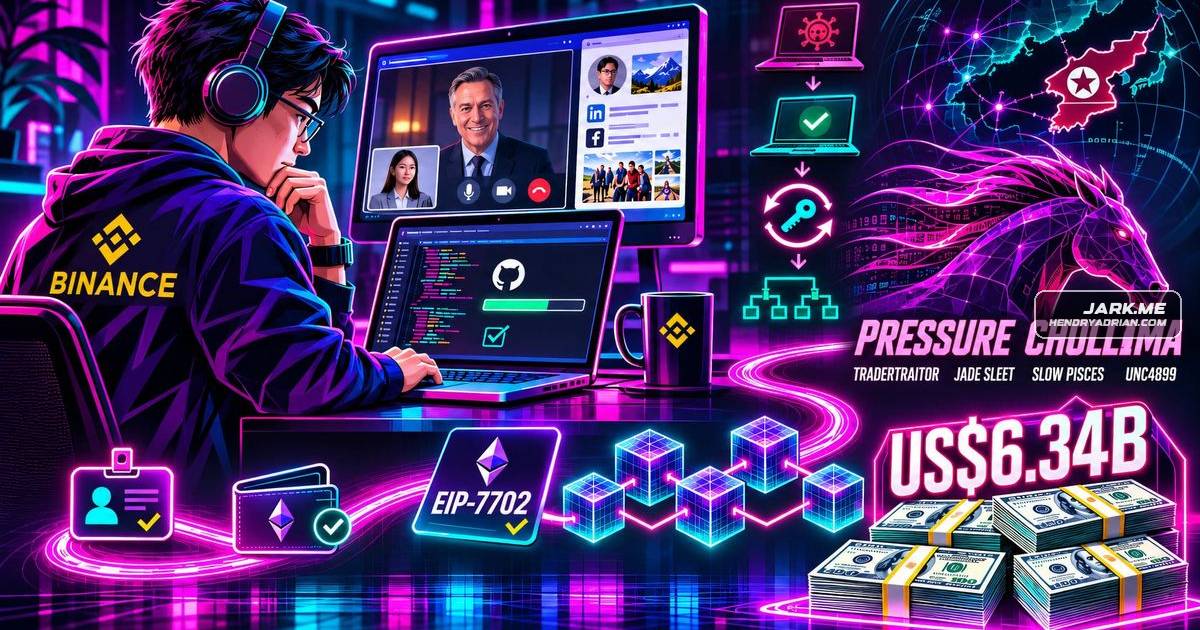
Binance’s preliminary report traces an attack to a fake job interview and compromised developer systems, which attackers used to reach wallet signing operations. The company says $6.34 billion in assets were affected; an independent review is pending.
Key points
- Binance’s preliminary report traces an initial June 2026 compromise to a tampered Homebrew installation, followed months later by a fake recruitment process targeting another engineer.
- A malicious coding assignment installed a custom implant that replaced a pyenv component and could execute commands from an attacker-controlled server; Binance identifies no exploited zero-day vulnerability.
- The attackers used compromised endpoints, stolen credentials, an internal AI tool and a container deployment token to move toward wallet operations; Binance has not explained the AI tool’s role in detail.
- On October 29, attackers used Binance’s signing service to authorize an EIP-7702 delegation from the Binance14 hot wallet. One of 50 signed authorizations took effect.
- Binance says about $6.34 billion in assets were affected, about $2.85 billion was frozen or intercepted, and roughly 98% of impacted token assets had been replenished by October 31.
- Binance says an independent review is forthcoming. Its preliminary report does not provide malware hashes or C2 infrastructure, or explain the signing policies that allowed the authorizations.
Article Details
- Attack Vectors
- In June 2026, a Binance wallet DevOps engineer downloaded a tampered Homebrew installation after searching for an AI coding tool. Binance says its security team detected the anomaly, replaced the device, and rotated related credentials.
- In September, the adversary allegedly posed as a recruiter, arranged video interviews with an ostensible HR representative and CEO, and persuaded a second engineer to download and run a coding assignment from a repository on a Binance work machine.
- The assignment created a malicious pyenv component in the Homebrew directory, replaced the legitimate pyenv, rebuilt a symbolic link, and spawned zsh. Binance says the component could execute commands from an attacker-controlled server and used obfuscation and evasion techniques.
- On October 20, the adversary used Engineer B's compromised computer and an internal AI tool to gain control over two other wallet-team engineers, then discovered a container-deployment permission token on Engineer A's computer.
- On October 29, the adversary used credentials stolen from Engineer A to access Engineer C's computer, deploy a container, and trigger the script that launched the theft.
- Binance says the adversary used its signing service to create EIP-7702 authorizations granting an attacker-controlled contract partial execution rights over the Binance14 hot wallet. One of fifty authorizations took effect, enabling unauthorized transfers.
- Defensive Notes
- Binance says it replaced the device affected by the June compromise and rotated related credentials, but the later operation used knowledge about the wallet team gained during that earlier access.
- After the incident, Binance says it rebuilt the affected internal AI tool and strengthened its access controls.
- Binance says it is reviewing signing-policy coverage and hot-wallet controls; its preliminary report does not explain what policy permitted the authorizations or why the pattern did not trigger an alert.
- Binance developed and sent a new on-chain authorization to clear the malicious delegation. It also reported that about US$2.85 billion was frozen or intercepted and roughly 98 percent of impacted token assets had been replenished by October 31.
MITRE ATT&CK
T1027 · Obfuscated Files or InformationBinance says the malicious component used obfuscation.T1059.004 · Unix ShellThe malicious pyenv component spawned zsh.T1070.004 · File DeletionBinance says the malware removed traces after execution.T1078 · Valid AccountsThe adversary used credentials stolen from Engineer A to access Engineer C's computer.T1195.002 · Compromise Software Supply ChainBinance traced an earlier compromise to a tampered Homebrew installation downloaded by a wallet DevOps engineer.T1204.002 · Malicious FileAn engineer downloaded and ran the malicious coding assignment on a Binance work machine.T1610 · Deploy ContainerThe adversary used stolen credentials to deploy a container as part of the attack chain.T1656 · ImpersonationThe adversary allegedly impersonated a recruiter, an HR representative, and a company CEO to induce an engineer to run a coding assignment.
Threat Actors
Jade SleetCrowdStrike tracks the cryptocurrency-theft adversary as PRESSURE CHOLLIMA. The article attributes the Binance operation to it and describes the fake-interview intrusion and theft; Binance's account is preliminary pending an independent review.MataThe article identifies Mata as one of the alternate names used by other security vendors for the cryptocurrency-theft adversary tracked by CrowdStrike as PRESSURE CHOLLIMA.
Products
BinanceHe does. Code buried inside the project executes during setup. The interview has done its job. North Korea now has the foothold Binance does not see.HomebrewJune 2026, when a wallet DevOps engineer searched for a popular AI coding tool and downloaded a tampered Homebrew installation. Binance's security team caught the anomaly. They replaced the device and rotated themacOSThe report identifies no zero-day CVE, no privilege-escalation flaw, and no published hole in macOS or pyenv behind the compromise.pyenvThe report identifies no zero-day CVE, no privilege-escalation flaw, and no published hole in macOS or pyenv behind the compromise.
Countries
JapanThe geopolitical scale is difficult to overstate. The United States, Japan, and South Korea have repeatedly warned that DPRK cryptocurrency theft generates illicit revenue for North Korea's unlawful weapons of massNorth KoreaHe does. Code buried inside the project executes during setup. The interview has done its job. North Korea now has the foothold Binance does not see.South KoreaThe geopolitical scale is difficult to overstate. The United States, Japan, and South Korea have repeatedly warned that DPRK cryptocurrency theft generates illicit revenue for North Korea's unlawful weapons of massUnited StatesThe geopolitical scale is difficult to overstate. The United States, Japan, and South Korea have repeatedly warned that DPRK cryptocurrency theft generates illicit revenue for North Korea's unlawful weapons of mass