
Google Reports Threat Actors Using AI Agents to Automate Exploits and Phishing
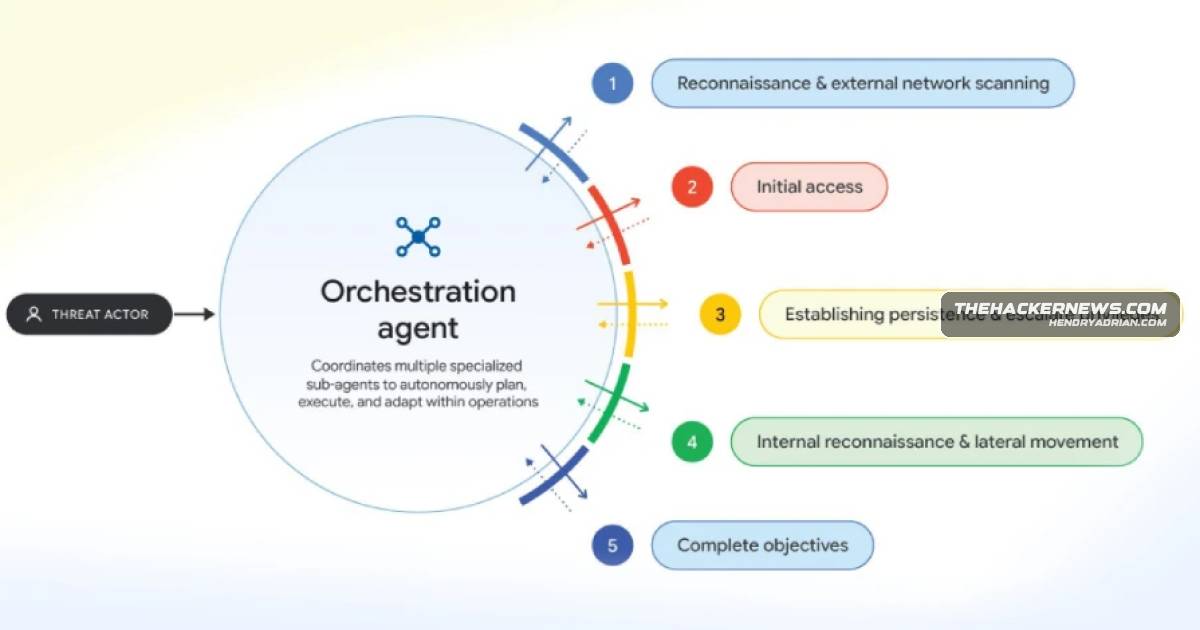
Summary
Google says threat actors are experimenting with AI-agent frameworks to automate intrusion tasks and weaponize patched vulnerabilities. Its findings also cover LLMjacking and an LLM-assisted phishing platform.
Key points
- Google reports that threat actors are experimenting with open-source agentic frameworks, including ARTEX, CAIRN, CyberStrikeAI, and PentAGI, to automate tasks during intrusions.
- The report says actors use LLMs and agentic frameworks to compare software versions and reverse-engineer patches, accelerating weaponization of newly disclosed vulnerabilities.
- Google cites PaperCut NG/MF flaws as an example of vulnerabilities actors sought to weaponize after patches were released.
- The report describes LLMjacking: stealing LLM credentials and cloud resources from compromised enterprises and reselling access through proxy services such as APIMart and JetNight.
- Google says the Jieyou phishing platform uses an LLM chatbot to help customers configure phishing panels and customize templates with natural-language commands.
- The findings include experimentation by financially motivated actors and suspected China-aligned espionage actors.
Article Details
- Event Type
- Google reported that threat actors are using AI agents and agentic frameworks to automate exploit development, intrusion tasks, phishing, and LLMjacking.
- Impact
- The reported use of these tools can accelerate vulnerability weaponization, scale intrusion operations, and lower the technical barrier to phishing. Google also reported theft of LLM credentials and cloud resources from compromised enterprise environments, with access resold through underground proxy services.
Products
Tools
Agent Zeroservices, such as ZeroHollow, an inference service used for exploit development and LLM routing, and Agent Zero, an open source agent framework which features autonomous code execution and dynamic tool generation,"ARTEXactors has gone beyond manual prompting to deploying autonomous multi-agent offensive frameworks like ARTEX, CAIRN, CyberStrikeAI, and PentAGI to execute multi-stage intrusions at greater operational velocity.Cairnhas gone beyond manual prompting to deploying autonomous multi-agent offensive frameworks like ARTEX, CAIRN, CyberStrikeAI, and PentAGI to execute multi-stage intrusions at greater operational velocity.CyberStrikeAIbeyond manual prompting to deploying autonomous multi-agent offensive frameworks like ARTEX, CAIRN, CyberStrikeAI, and PentAGI to execute multi-stage intrusions at greater operational velocity.JieyouThis includes a Chinese-language phishing platform called Jieyou that has integrated an LLM chatbot assistant to allow customers to configure phishing panels and modify existing templates using natural language commandsPentAGIprompting to deploying autonomous multi-agent offensive frameworks like ARTEX, CAIRN, CyberStrikeAI, and PentAGI to execute multi-stage intrusions at greater operational velocity.ZeroHollow"These observations additionally extend to the use of other tools and services, such as ZeroHollow, an inference service used for exploit development and LLM routing, and Agent Zero, an open source agent framework which