
CERT-In Warns of AI-Assisted Attacks as Backdoored ARTEX Image Is Found on 62 Consoles
Summary
CERT-In reports AI-assisted attacks targeting Indian financial organizations. A researcher says a backdoored ARTEX Docker image enables unauthenticated root command execution; 62 internet-facing consoles served the build.
Key points
- CERT-In says the actor it tracks as Crafty Falcon is targeting Indian BFSI organizations with AI-assisted offensive tools, including ARTEX, PentAGI, Cairn, and CyberStrikeAI.
- CERT-In reports attacks exploiting internet-facing applications and exposed APIs to steal credentials and invoke fund-transfer APIs, while operators delete logs and tamper with endpoint security tools.
- The agency says cryptocurrency exchanges and digital asset service providers have also been targeted, resulting in theft of keys and funds.
- CERT-In's Artificial Intelligence Security Auditing Guidelines call for testing agent identities, objectives, tool permissions, least privilege, human approval for consequential actions, and emergency controls for high-risk systems.
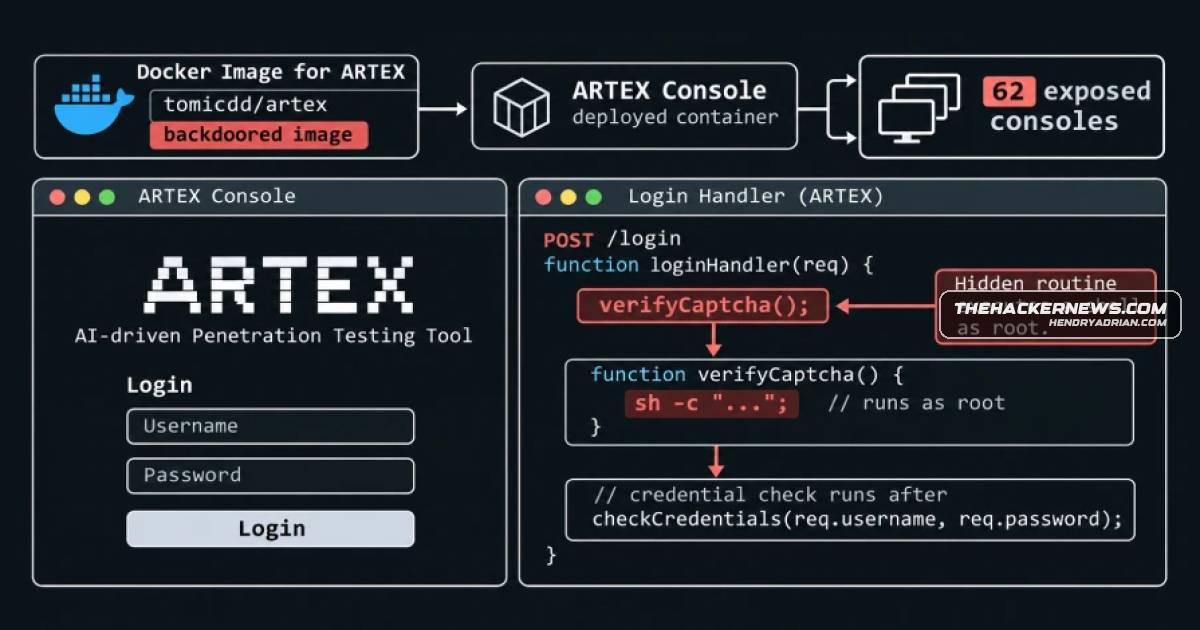
- Researcher Badbyte says a modified ARTEX Docker image contains a login handler that can execute a shell command as root during an unauthenticated request using a secret CAPTCHA marker.
- The backdoored build was found on 62 internet-facing ARTEX consoles between November 2 and 4, 2026; Docker Hub statistics cited in the article show 9,000 downloads of the image.
Article Details
- Event Type
- CERT-In warning about active AI-assisted cyberattacks against financial-sector organizations and discovery of a backdoored ARTEX Docker image.
- Impact
- CERT-In reported attacks targeting financial organizations, cryptocurrency exchanges, and digital asset service providers, including theft of keys and funds. Separately, researcher Badbyte reported that a modified ARTEX image provided an unauthenticated root shell; 62 consoles were found serving the backdoored build, and Docker Hub statistics showed 9,000 downloads. The article does not establish that all exposed consoles were compromised.
MITRE ATT&CK
T1059.004 · Unix ShellThe backdoored ARTEX image reportedly runs attacker-supplied input through sh -c as root.T1070 · Indicator RemovalCERT-In reported that operators delete logs to complicate detection and incident response.T1105 · Ingress Tool TransferCERT-In reported that attackers target cloud infrastructure to deploy malicious payloads.T1190 · Exploit Public-Facing ApplicationCERT-In said attackers exploit internet-facing applications and exposed APIs and privileged endpoints.T1562.001 · Disable or Modify ToolsCERT-In reported that attackers tamper with endpoint security tools.
People
Threat Actors
Tools
ARTEXDescribing the threat as active and ongoing, the activity involves the use of publicly-available AI-driven offensive security tools like ARTEX, PentAGI, Cairn, and CyberStrikeAI.CairnDescribing the threat as active and ongoing, the activity involves the use of publicly-available AI-driven offensive security tools like ARTEX, PentAGI, Cairn, and CyberStrikeAI.CyberStrikeAIDescribing the threat as active and ongoing, the activity involves the use of publicly-available AI-driven offensive security tools like ARTEX, PentAGI, Cairn, and CyberStrikeAI.PentAGIDescribing the threat as active and ongoing, the activity involves the use of publicly-available AI-driven offensive security tools like ARTEX, PentAGI, Cairn, and CyberStrikeAI.
Countries
Chinaimage was pushed. Of these, 26 consoles are located in the U.S., followed by 17 in Hong Kong and seven in China.Hong Kongafter the Docker image was pushed. Of these, 26 consoles are located in the U.S., followed by 17 in Hong Kong and seven in China.United StatesOctober 20, 2026, twelve days after the Docker image was pushed. Of these, 26 consoles are located in the U.S., followed by 17 in Hong Kong and seven in China.
Industries
Banking, Financial Services, and Insurance (BFSI)threat actor it tracks as Crafty Falcon is targeting organizations in the Banking, Financial Services, and Insurance (BFSI) sectors in the country.Digital lendingwhich warned of multiple cyber attack campaigns targeting non-banking financial companies (NBFCs), digital lending platforms, fintech entities, payment service providers, and cryptocurrency wallet operators.fintechcyber attack campaigns targeting non-banking financial companies (NBFCs), digital lending platforms, fintech entities, payment service providers, and cryptocurrency wallet operators.Non-banking financial companies (NBFCs)2026 alert issued by CERT-In, which warned of multiple cyber attack campaigns targeting non-banking financial companies (NBFCs), digital lending platforms, fintech entities, payment service providers, and