
Law Enforcement Disrupts Gootloader, CastleRAT and StealC Infrastructure
Summary
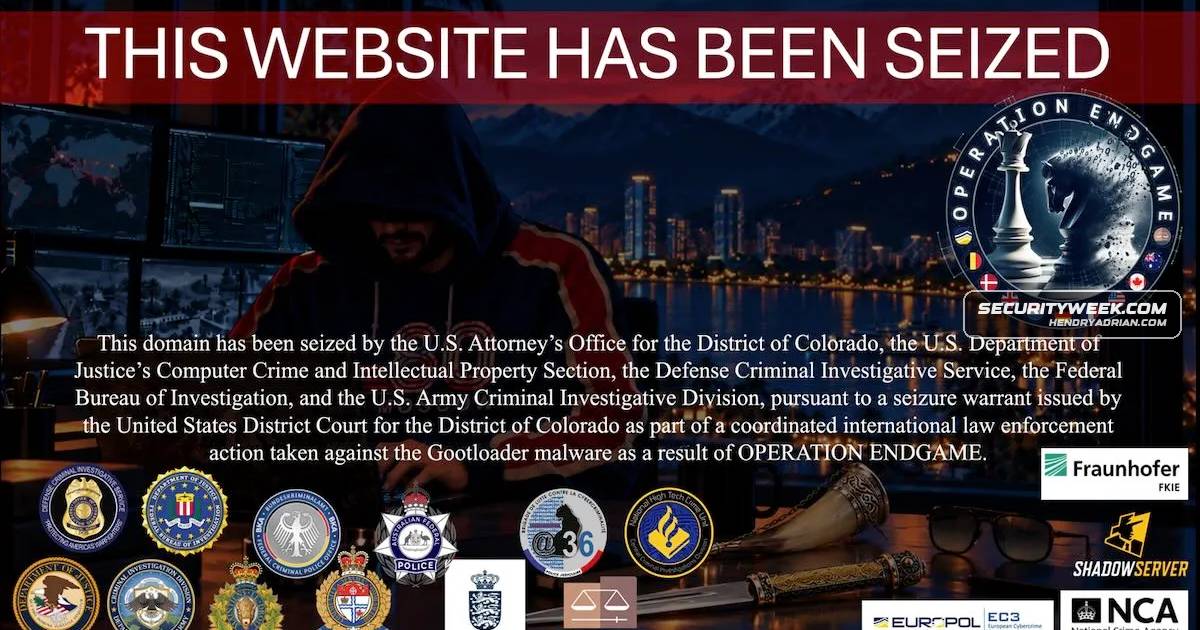
Authorities in the US, Europe, Australia and Canada disrupted infrastructure linked to Gootloader, CastleRAT and StealC, seizing servers and domains. Europol says the operation recovered 6.4 million victim credentials.
Key points
- Authorities seized 235 servers and 257 domains associated with the three malware operations, according to Europol.
- Operation Endgame removed Gootloader from 100 servers; Europol also reports 14 servers and 218 domains seized and 681 infected websites cleaned.
- Law enforcement seized 120 CastleRAT servers and 39 domains, as well as victim data; HaveIBeenPwned says 180,000 email addresses and 893,000 unique passwords were retrieved.
- Authorities disrupted 102 StealC servers and seized 6.4 million victim credentials, which Europol says were shared with security organizations.
- Europol says the stolen credentials were used for sale and could enable further cyberattacks, including ransomware.
Article Details
- Event Type
- International law enforcement disruption and seizure of infrastructure associated with Gootloader, CastleRAT, and StealC operations.
- Impact
- Investigators seized 235 servers and 257 domains associated with the operations. The article reports that Gootloader-related action removed the malware from 100 servers, seized 14 servers and 218 domains, and cleaned 681 infected websites; CastleRAT-related action seized 120 servers, 39 domains, and victim data; and 102 StealC servers were disrupted. Europol says 6.4 million victim credentials were seized and shared with partner organizations. HaveIBeenPwned says CastleRAT-related data included 180,000 email addresses and 893,000 unique passwords. The US Department of Justice says Gootloader infected over 25,000 computers and caused approximately $28.8 million in damages in the United States.
Malware
CastleRATLaw enforcement agencies in the US, Europe, Australia, and Canada have seized infrastructure behind the notorious Gootloader, CastleRAT, and StealC malware.GootloaderLaw enforcement agencies in the US, Europe, Australia, and Canada have seized infrastructure behind the notorious Gootloader, CastleRAT, and StealC malware.StealCLaw enforcement agencies in the US, Europe, Australia, and Canada have seized infrastructure behind the notorious Gootloader, CastleRAT, and StealC malware.
Countries
AustraliaLaw enforcement agencies in the US, Europe, Australia, and Canada have seized infrastructure behind the notorious Gootloader, CastleRAT, and StealC malware.CanadaLaw enforcement agencies in the US, Europe, Australia, and Canada have seized infrastructure behind the notorious Gootloader, CastleRAT, and StealC malware.United StatesLaw enforcement agencies in the US, Europe, Australia, and Canada have seized infrastructure behind the notorious Gootloader, CastleRAT, and StealC malware.