
Hudson Rock Finds Historical Infostealer Credentials for Two Addresses Reported in School Threats
Summary
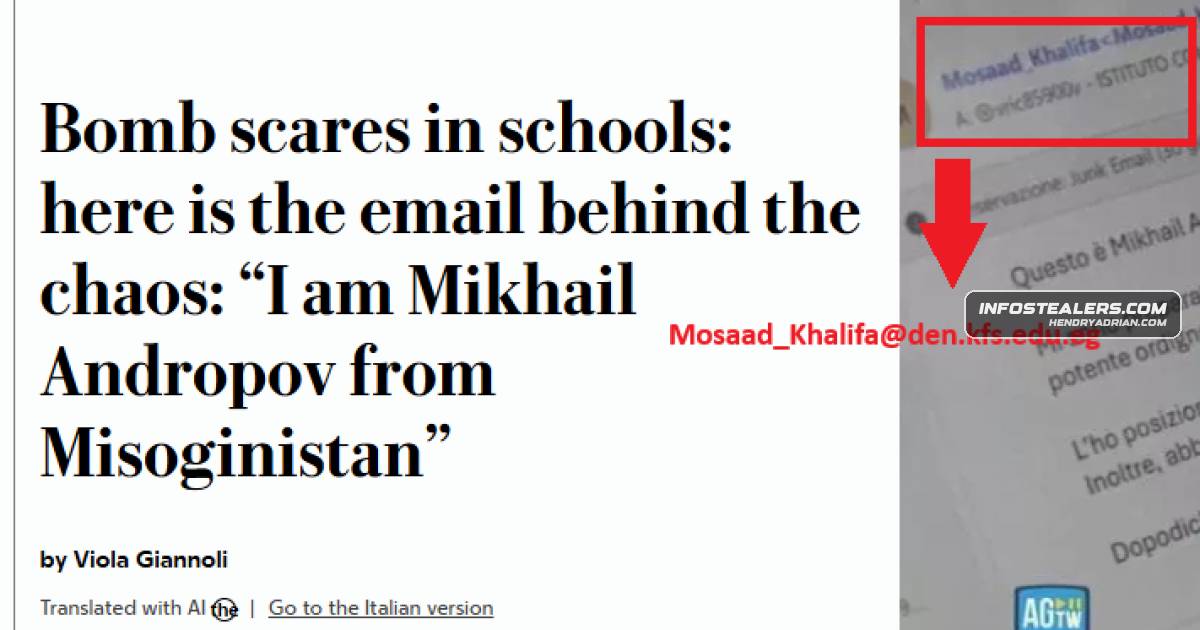
Hudson Rock found historical infostealer-derived credentials for two university email addresses reported in connection with November 2026 school threats. The records predate the threats but do not show the credentials were used to send them.
Key points
- A Vidar-associated computer record dated October 1, 2021 contained 112 browser credential records, including 20 for the Egyptian university address and two saved for Microsoft sign-in pages.
- Hudson Rock found the Taiwanese university address in historical AlienTXTBASE data and assesses the credential entry as infostealer-derived, dating it to more than a year before the threats.
- Da-Yeh University reported that an alumnus account sent a large volume of email and appeared compromised; it suspended the account while investigating the cause and sender.
- The threats disrupted schools in Italy and elsewhere. The sender name and organizational labels in the messages are unverified claims.
- The records do not establish that the credentials remained valid or were used to send the threats, or that either account holder authored them. Provider sign-in and mail records are needed to connect the accounts to the sending activity.
- The article recommends investigating affected devices, replacing exposed credentials, revoking sessions, and monitoring sign-ins and outgoing mail.
Article Details
- Event Type
- Investigation into bomb-threat emails sent to schools, reporting historical infostealer credential exposure for two university accounts associated with threat-related material.
- Impact
- ANSA reported that approximately 6,000 Italian schools received the messages, citing the Education Ministry; some schools evacuated. Police in Northern Ireland said more than 300 schools reported the same message, and Police Scotland assessed threats as hoaxes. Searches in Italy found no bombs, according to Prime Minister Giorgia Meloni. Hudson Rock found historical Vidar-associated credentials for an Egyptian university address and an infostealer-derived entry for a Taiwanese university address, but the evidence does not establish that the credentials were used to send the threats. The Taiwanese university reported apparent account compromise and suspended the account.
People
Malware
Vendors
Tools
Countries
EgyptThe Egypt-associated machine in Hudson Rock’s Cavalier platform.IrelandPolice in Northern Ireland said more than 300 schools reported the same threatening message.ItalyThe disruption extended beyond Italy. Police in Northern Ireland said more than 300 schools reported the same threatening message.TaiwanFocus Taiwan reported on November 12 that Da-Yeh University’s initial investigation found an alumnus account had sent a large volume of email and appeared to have been compromised.