
Vates Says Xen Orchestra Authentication Bypass Is Being Actively Exploited
Summary
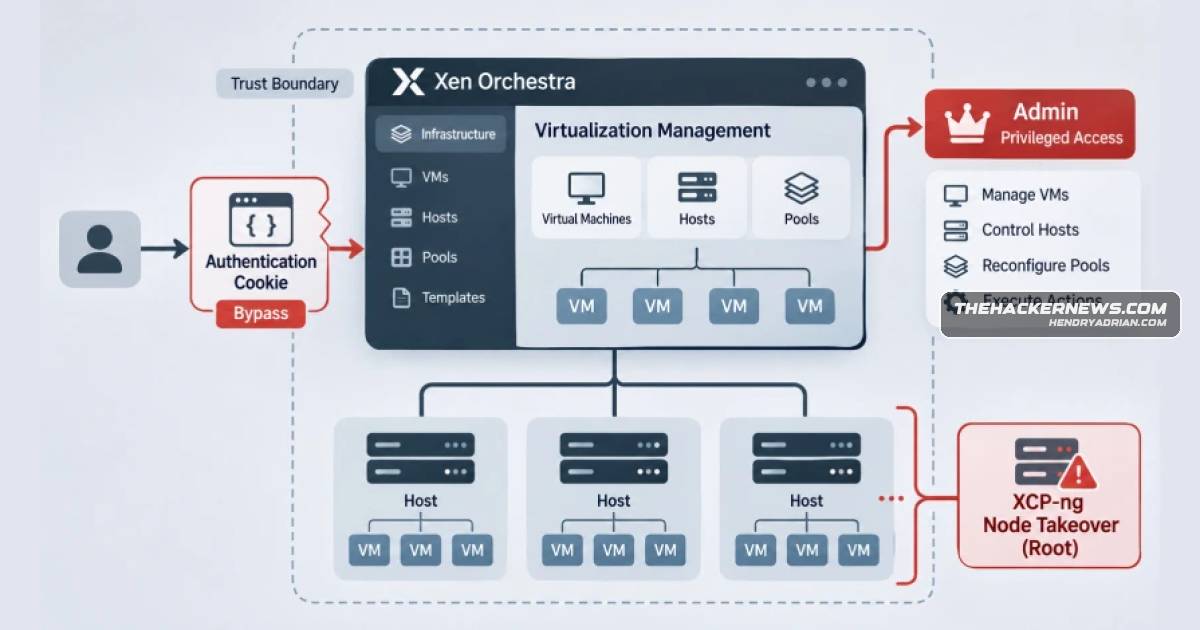
Vates says attackers are exploiting Xen Orchestra flaw VSA-2026-062. A crafted cookie may bypass authentication and enable admin actions, potentially leading to code execution and root takeover; fixes are available.
Key points
- Vates reports active exploitation of Xen Orchestra authentication-bypass flaw VSA-2026-062; the flaw has no CVE identifier.
- The described flaw involves REST cookie parsing and token lookup accepting an object instead of requiring a string.
- Vates says the flaw may allow authentication bypass, admin-level actions, arbitrary code execution on managed pools, and root takeover of an XCP-ng node.
- Vates attributes observed exploitation to a threat actor but the supplied article does not include the referenced IP address or TOR domain.
- Fixes are listed for Xen Orchestra 6.9.1 and 6.10.0, and xo-server 5.211.2 and 5.213.1.
- The article says the start of the activity and whether the flaw was exploited as a zero-day are unclear.
Article Details
- Vulnerability Types
- Authentication bypass
- Severity
- Critical
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
People
Vendors
Products
XCP-ngwith "Admin" privileges, ultimately resulting in arbitrary code execution on managed pools and a full XCP-ng node takeover as root.Xen OrchestraFrench software company Vates VMS has warned of a critical security vulnerability in Xen Orchestra that it said is being actively exploited in the wild.