
Xen Flaws Let Malicious VMs Read and Write Other VMs’ Memory
Summary
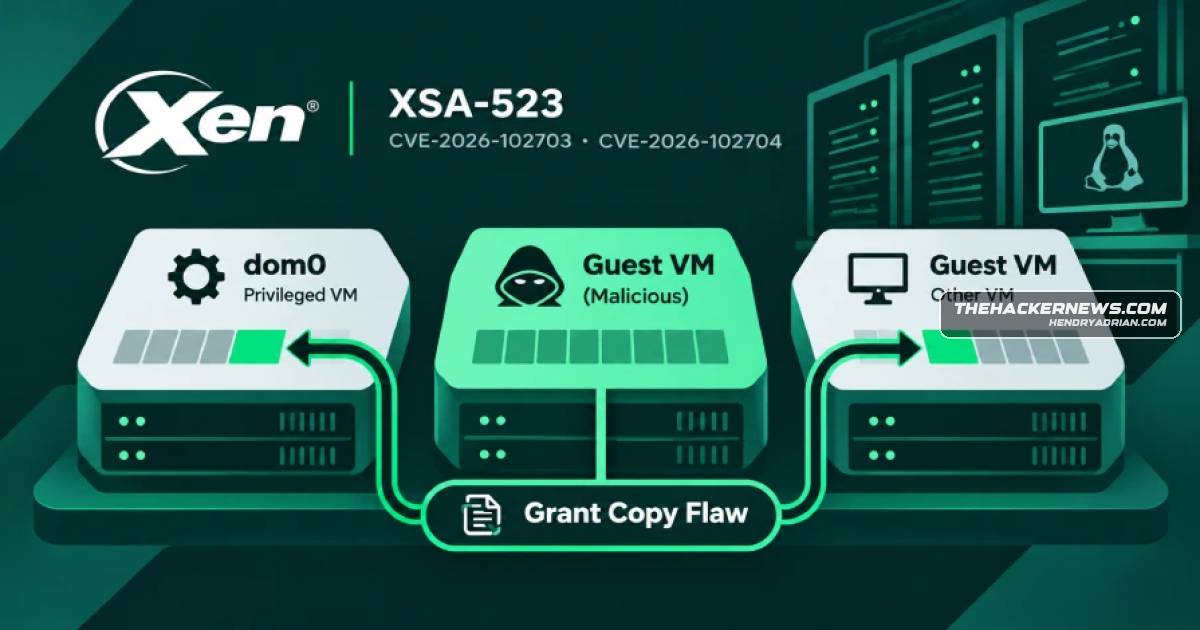
Two flaws in Xen 4.6 and later can let a malicious guest VM read and write other VMs’ memory, including dom0. Patches are available; the article reports no known exploitation.
Key points
- CVE-2026-102703 and CVE-2026-102704 are tracked together as Xen advisory XSA-523.
- The flaws affect Xen versions 4.6 and later; versions 4.5 and earlier are not affected.
- A grant-copy permission-check reuse error can allow a guest VM to access memory belonging to other VMs, including dom0.
- The Xen Project has published patches; its advisory provides no known mitigation.
- The advisory does not report attacks exploiting the flaws or specify the attacker access required within a VM.
- Qubes OS said all supported releases and configurations are affected; its fix was in security testing, with stable release planned after community testing.
- As of November 4, Debian listed xen as vulnerable in bookworm, trixie, and forky, and fixed in sid.
Article Details
- Vulnerability Types
- Grant-copy permission-check flaws allowing cross-VM memory access
- Affected Versions
- Xen 4.6 and later
- Exploitation Status
- not_reported
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
CVE
CVE-2026-102703Xen · XenAll Xen versions from 4.6 onward are vulnerable, while 4.5 and earlier are not. The flaws are tracked as CVE-2026-102703 and CVE-2026-102704, under Xen advisory XSA-523.CVE-2026-102704Xen · XenAll Xen versions from 4.6 onward are vulnerable, while 4.5 and earlier are not. The flaws are tracked as CVE-2026-102703 and CVE-2026-102704, under Xen advisory XSA-523.
People
Vendors
Products
Debian Linuxbuilt on those versions are affected until their makers add the XSA-523 patches. As of November 4, Debian's security tracker listed the xen package in its bookworm, trixie, and forky releases as vulnerable, andQubes OSQubes OS is a security-focused desktop operating system that keeps software in separate Xen-based compartments called qubes. A bulletin said that every supported release and configuration is affected. Its fix is forXCP-ngXCP-ng, an open-source virtualization platform built around Xen, said in its update notes that "a single compromised guest can break out of its isolation and take over the whole host."XenTwo flaws in the Xen hypervisor allow a malicious guest virtual machine (VM) to read and write the memory of other VMs on the same host, including dom0.