
Exposed API Key Led to 2.3 Million Emails and a $10K Bill
Summary
An exposed SendGrid API key was abused to send 2.3 million emails, driving a reported 500× bill spike and harming deliverability. The article also describes phishing through a compromised Purdue SendGrid account and recommends key controls and monitoring.
Key points
- DMARC reports revealed an abnormal surge in outbound email from a fully authenticated domain.
- An engineering vendor confirmed SendGrid API keys were exposed and believed a NextJS vulnerability was responsible.
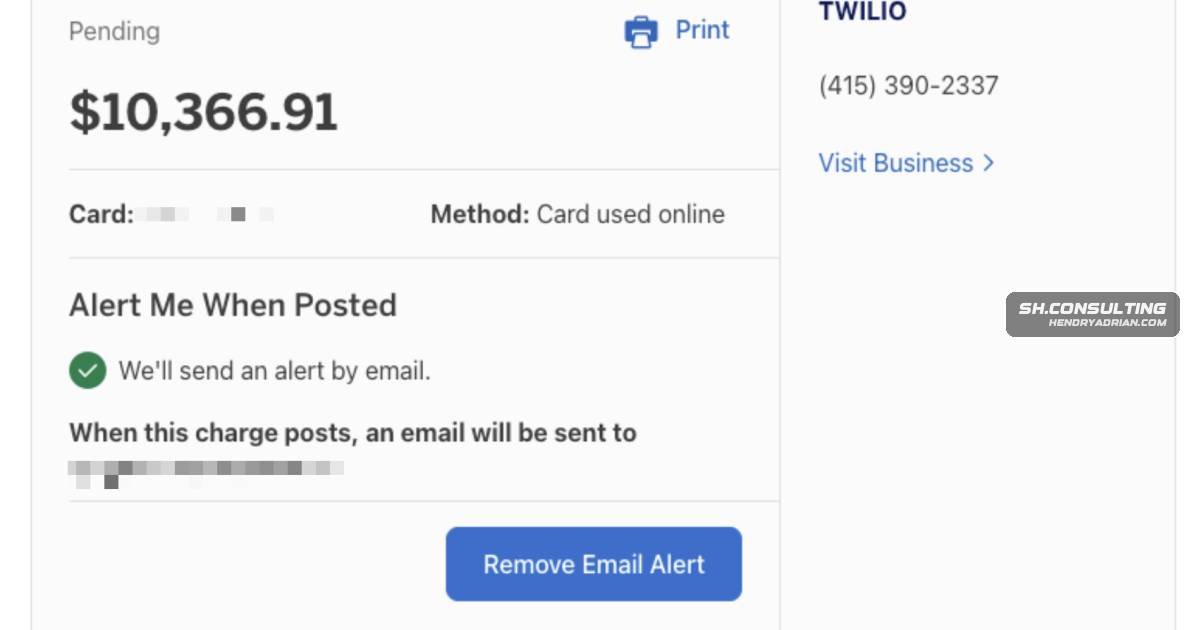
- The keys were revoked, but the incident reportedly drove a more than 500× bill spike, reaching $10,000, and damaged domain reputation and deliverability.
- The author says a client was targeted by phishing sent through a compromised Purdue University SendGrid account; the messages passed SPF and DKIM.
- The phishing email imitated SendGrid and linked to a credential-harvesting site on a domain registered that day.
- Purdue changed its DMARC policy to p=quarantine, and Purdue and SendGrid closed the reported hole; DMARC alone does not prevent abuse of valid API keys.
- Recommended safeguards include limiting access to API keys, using separate least-privilege keys, rotating API and DKIM keys, and monitoring DMARC reports and sending volume.
Article Details
- Defense Focus
- Detect abnormal authenticated email activity and reduce the risk and impact of exposed SendGrid API keys.
- Detection Methods
- Review DMARC reports for abnormal surges in authenticated outbound email.
- Monitor email sending volume for unexpected spikes.
- Data Sources
- DMARC reports
- Email sending-volume data
- Defensive Actions
- Restrict which people and systems can access API keys.
- Use a separate API key for each system and grant each key only the permissions it needs.
- Rotate API and DKIM keys on a schedule.
- Revoke exposed keys promptly.
- Review vendor security practices that affect the handling of your keys.
- Do not rely on DMARC policy alone to prevent abuse of valid API keys.
MITRE ATT&CK
Vendors
SendGridA Twilio bill spiked more than 500× after an exposed API key was abused to send 2.3 million emails through a company’s SendGrid infrastructure.TwilioA Twilio bill spiked more than 500× after an exposed API key was abused to send 2.3 million emails through a company’s SendGrid infrastructure.