
January 2026 Report Surveys Cyber Threats to Korean and Global Financial Firms
Summary
A January 2026 review covers malware and phishing targeting financial firms, dark-web sales of access and data, and ransomware claims. It describes an insurer access offer, a claimed 22.5 million-record dataset sale, and a Clop listing with no breach confirmed.
Key points
- The report says FTP, SSH, and RDP credentials for a masked Mexican insurer were offered on LeakBase; actor PanchoVilla claimed network access and potential ransomware deployment.
- Actor Solonik offered a dataset allegedly containing about 22.5 million customer records from a masked U.S. asset manager; the report describes sample records but does not independently confirm the claimed dataset.
- Clop listed a masked global payment processor as a victim and claimed to possess internal data. No leaked samples or file lists had been disclosed, and no breach was confirmed at the time of the report.
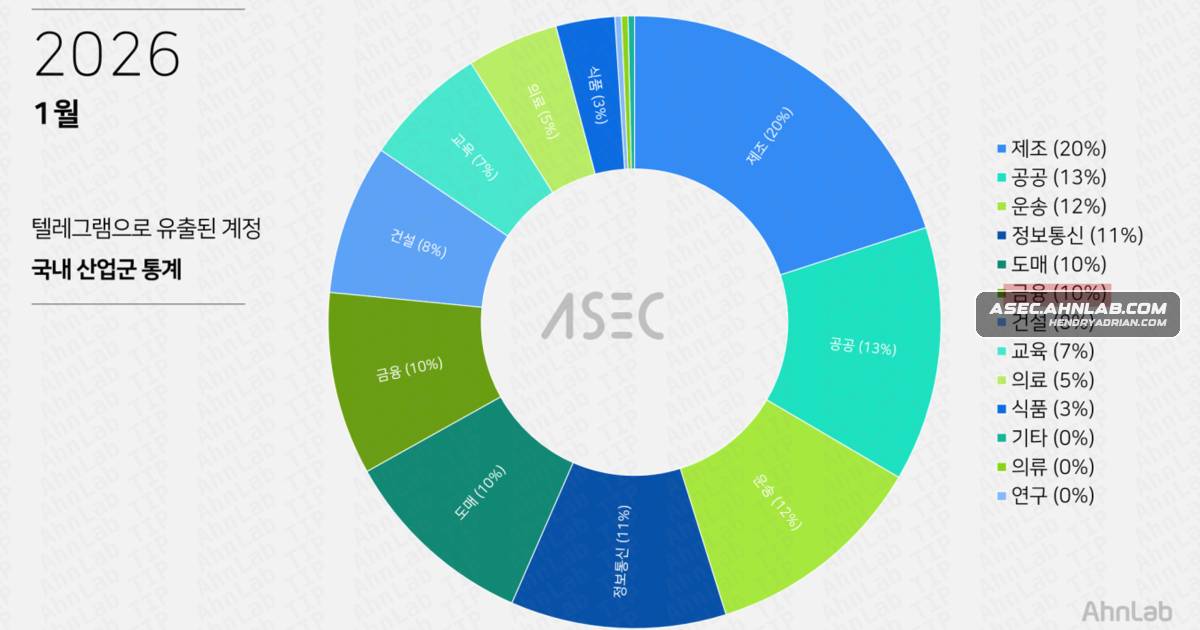
- The report also discusses financial-sector phishing and malware, and statistics on domestic account industries represented in data leaked via Telegram.
- It identifies dark-web sales of financial data and access as risks that could enable follow-on impersonation, phishing, or fraud.
Article Details
- Publisher
- ASEC (asec.ahnlab.com)
- Report Period
- January 2026
- Scope
- Cyber threats affecting the Korean and global financial sectors, including phishing, dark-web data and access sales, database leaks, and ransomware.
- Key Statistics
- Solonik claimed the dataset for The V***, Inc. contained approximately 22.5 million customer records; the claim was not independently confirmed.
- Solonik also provided an additional sample of approximately 34,000 records.
- The claimed V*** dataset was offered for $9,500.
- The report lists five MD5 hashes associated with incidents.
- Recommendations
- Continuously monitor for additional evidence or data releases related to the Clop listing of T***.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| MD5 | 0e945218340f80377d777f43a86bdd57 | MD5 hash published in the report among ransomware/malware sample artifacts associated with incidents; the specific sample attribution is not stated. |
| MD5 | 539fe169480ffd66765c1693f8ed0d7d | MD5 hash published in the report among ransomware/malware sample artifacts associated with incidents; the specific sample attribution is not stated. |
| MD5 | 940cfb70828c94ae4b5ae4fdee4a98a3 | MD5 hash published in the report among ransomware/malware sample artifacts associated with incidents; the specific sample attribution is not stated. |
| MD5 | abbe5d0506f14ae9de6e59d598bc7c42 | MD5 hash published in the report among ransomware/malware sample artifacts associated with incidents; the specific sample attribution is not stated. |
| MD5 | b8c046a7c3a28653662140bb2eaad32d | MD5 hash published in the report among ransomware/malware sample artifacts associated with incidents; the specific sample attribution is not stated. |
MITRE ATT&CK
T1021 · Remote ServicesFTP, SSH, and RDP credentials for access to the H*** internal network were reportedly leaked and offered for sale.T1071 · Application Layer ProtocolThe actor reportedly mentioned that deploying a C2 server was possible; the report does not say that one was deployed.T1078 · Valid AccountsThe report describes claimed access to the H*** network through an already authorized user account.T1486 · Data Encrypted for ImpactThe report discusses ransomware groups and financial-sector victim listings, but notes that the Clop listing of T*** did not confirm a breach or encryption.T1566 · PhishingThe report describes phishing email campaigns targeting financial institutions without providing specific campaign indicators.T1567 · Exfiltration Over Web ServiceThe report says samples of a dumped database were presented through an external file-sharing link.
Threat Actors
Apt73The report presents APT73 as a name associated with Eraleig, which it identifies as a ransomware group that compromised and publicly listed financial-sector victims.ClopListed T*** as a victim and claimed to possess its internal data; the report says no leaked data samples or file lists had been disclosed and no breach was confirmed.EraleigIdentified by the report as a ransomware group that compromised and publicly listed financial-sector victims.EverestIdentified by the report as a ransomware group that compromised and publicly listed financial-sector victims.PanchoVillaClaimed to have compromised access to the H*** insurance network through an authorized user account and said the access could support ransomware deployment; these claims are not independently confirmed.SolonikClaimed access to and offered for sale a dataset allegedly containing V*** customer records; the reported breach and dataset claims are not independently confirmed.
Countries
MexicoH*** is a property and casualty insurance company headquartered in Mexico and is the Mexican subsidiary of the H*** brand, which belongs to the German insurance group ***.United KingdomT*** is a global payment and card processing service company headquartered in London, UK,.United Statesis a global asset management company based in the United States that provides ETF and asset management products, and operates investment· asset management services for individual and institutional investors.
Industries
Asset managementData from the American asset management and investment advisory firm The V***, Inc.InsuranceAccess credentials (FTP, SSH, RDP) for a Mexican insurance company (h***.mx) were leaked and offered for sale on the LeakBase forum, with claims of backdoor access and potential for ransomware deployment.