
AhnLab Reports January Infostealer Trends, Including ACRStealer Encryption Changes
Summary
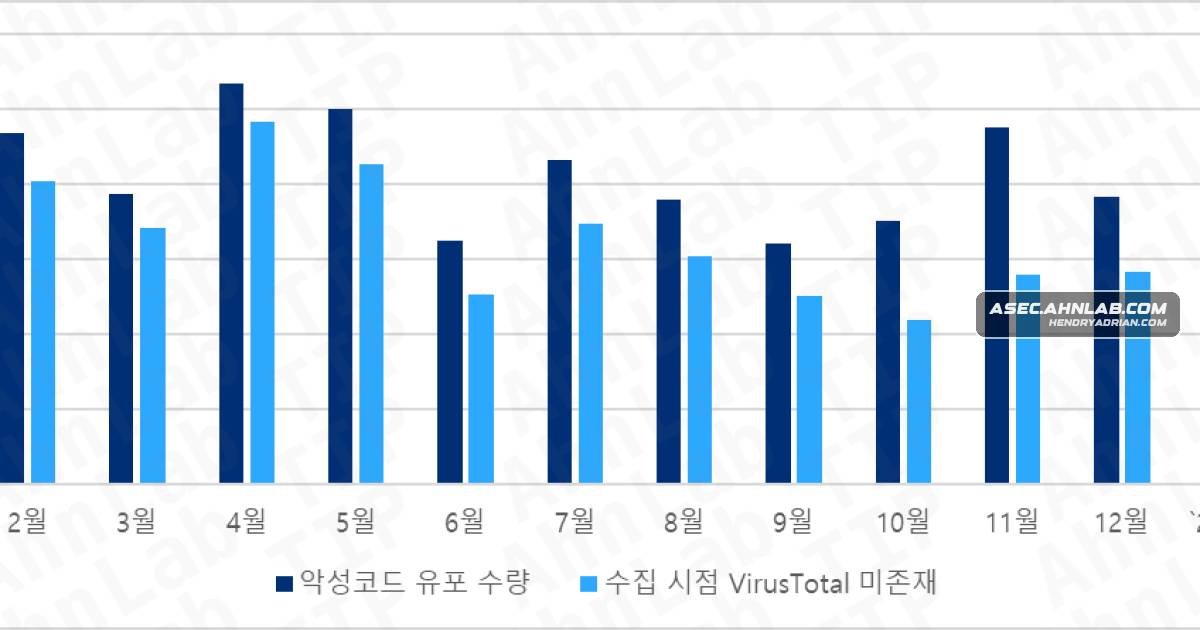
AhnLab’s January 2026 report tracks infostealer distribution and techniques. It highlights SEO-poisoned downloads, Windows DLL sideloading, macOS ClickFix delivery, ACRStealer’s new encryption, and MacSync Stealer.
Key points
- AhnLab used automated collection and analysis systems to track infostealer samples and C2 information, providing IOCs through its ATIP service.
- Attackers used SEO poisoning and posts on legitimate forums, corporate Q&A pages, and poorly managed WordPress sites to promote disguised malware.
- Windows samples were about 70.8% EXE and 29.2% DLL sideloading; AhnLab warns that modified malicious DLLs may resemble legitimate files.
- macOS delivery included ClickFix-style terminal commands and Bash scripts, with payloads delivered as Fatbin binaries or executed through osascript; sample hashes changed rapidly.
- AhnLab observed ACRStealer variants switching from a hardcoded AES key to ECDH key exchange and ChaCha20-Poly1305, with a C2-issued X-Requests-Key header.
- The MacSync Stealer case used a GitHub-impersonating page to induce command execution; its script collected system information and sent it to C2.
Article Details
- Publisher
- AhnLab Security Intelligence Center (ASEC)
- Report Period
- January 2026
- Scope
- Automated collection and analysis of infostealers distributed through crack/keygen pages and other online posts, including Windows and macOS distribution methods and obfuscation.
- Key Statistics
- In January 2026, approximately 70.8% of observed infostealer samples were EXE files and 29.2% used DLL SideLoading.
- Recommendations
- Exercise caution with DLL SideLoading samples, which may visually resemble their original benign DLLs.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | sestraining[.]com | MacSync Stealer C2 domain used to deliver scripts and receive collected data. |
| DOMAIN | www[.]corvix[.]life | Domain identified in the report as an infostealer distribution site. |
| IPV4 | 146[.]103[.]102[.]11 | C2 IP address associated with samples in the report. |
| IPV4 | 94[.]103[.]95[.]97 | C2 IP address associated with samples in the report. |
| MD5 | 01d120f0c69e3d3d46954bfab810ca5f | AhnLab-listed infostealer sample hash for detection. |
| MD5 | 039d3ed581a75ae7f85a38aeec34bd52 | AhnLab-listed infostealer sample hash for detection. |
| MD5 | 03d1fcf73519768d598b4ba895b7e30d | AhnLab-listed infostealer sample hash for detection. |
| MD5 | 05b9ff47314c60e6458af6e385c79234 | AhnLab-listed infostealer sample hash for detection. |
| MD5 | 07b6dc68f629a8cf24cd8a1dd53df8fc | AhnLab-listed infostealer sample hash for detection. |
| MD5 | 4aab18983ab8c00f3c619b75033ce548 | Hash identified in the report as MacSync Stealer. |
| MD5 | 73600d113646a95d2e459dd940c18e1e | Hash of the MacSync Stealer script identified in the report. |
| MD5 | 74e17b926dc6cc5ab247aa0e059916c1 | Hash of the MacSync Stealer decoding script identified in the report. |
| SHA256 | 7a5c704e85df3dec08c9ab17857c4ac13337c23f43616d2736653963de7f91f2 | AhnLab-reported sample hash associated with ACRStealer. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe report describes Base64 encoding, gzip compression, and rapid malware hash changes used to hinder detection or analysis.T1059.004 · Unix ShellmacOS distribution used Bash or zsh commands, including commands that decoded and executed Base64-encoded content.T1059.006 · PythonMacSync Stealer used osascript-based payloads to collect information and communicate with C2.T1071.001 · Web ProtocolsThe report describes C2 communication over HTTP/S, including encrypted exchanges and a custom X-Requests-Key header.T1204 · User ExecutionDistribution pages prompted users to copy commands and paste them into a terminal for execution.T1574 · Hijack Execution FlowInfostealers used DLL SideLoading: a malicious DLL placed beside a normal executable was loaded when that executable ran.
Malware
ACRStealerNotable findings include ACRStealer’s shift to ECDH + ChaCha20-Poly1305 for C2 encryption and rapid macOS sample churn with terminal copy-paste (ClickFix) and osascript-based payloads.LummaC2Primary families observed in January were LummaC2, Vidar, and ACRStealer, with macOS families like MacSync Stealer also actively distributed.MacSync StealerPrimary families observed in January were LummaC2, Vidar, and ACRStealer, with macOS families like MacSync Stealer also actively distributed.VidarPrimary families observed in January were LummaC2, Vidar, and ACRStealer, with macOS families like MacSync Stealer also actively distributed.