
Proofpoint Uncovers TrustConnect RAT Masquerading as an RMM Tool
Summary
Proofpoint analyzed TrustConnect, a MaaS RAT posing as an RMM tool, detailing signed installers, phishing delivery and remote-control C2. After disruption, operators pivoted to DocConnect; a Redline link is assessed with moderate confidence.
Key points
- TrustConnect was sold as a $300-per-month MaaS and used an Extended Validation certificate to sign its installers. The certificate was revoked on 6 February 2026, though previously signed files remained valid.
- Email campaigns used lures and executables such as MsTeams.exe to install TrustConnectAgent.exe, which communicated with the RAT’s C2.
- The web dashboard supported device management, command execution, file transfer, remote desktop, screen recording and branded installer generation.
- Operators also deployed legitimate remote-access tools, including ScreenConnect and Level RMM; Proofpoint reported an abused Level RMM account that the vendor disabled.
- Proofpoint coordinated remediation of TrustConnect infrastructure, completed around 17 February 2026. Researchers then identified a pivot to DocConnect, also called SHIELD OS v1.0, with a new agent and C2 architecture.
- Proofpoint assessed with moderate confidence that the TrustConnect actor was likely a Redline customer, based on campaign artifacts, infrastructure and malware delivery; the article notes the Telegram handle could have been used by another actor.
Article Details
- Attack Vectors
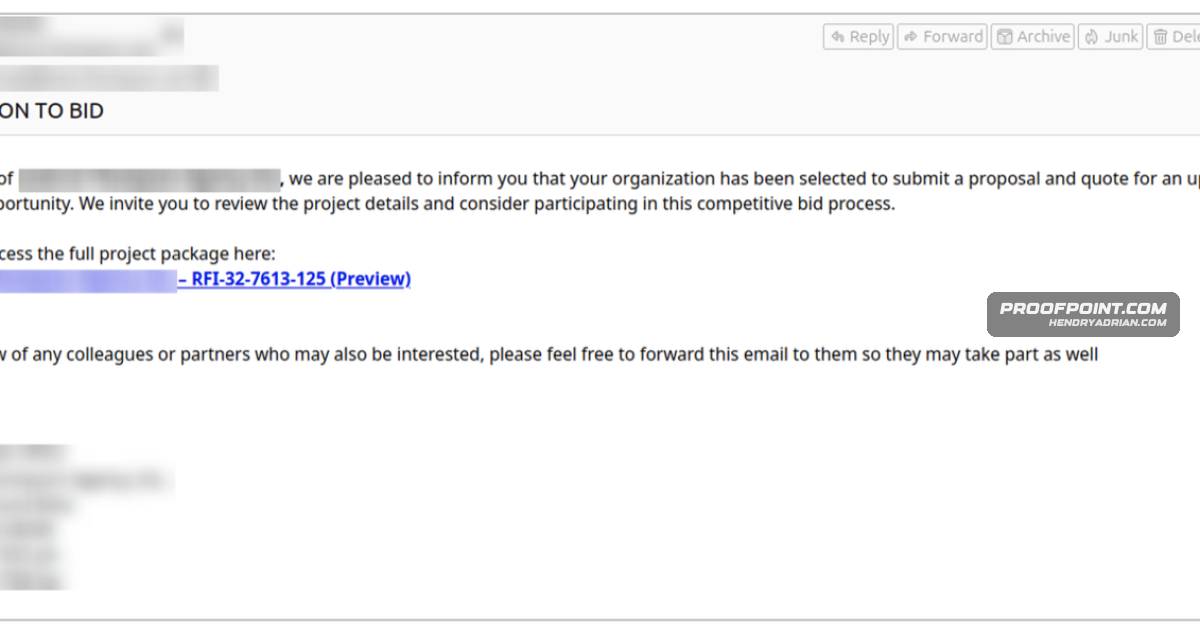
- Email campaigns sent from compromised senders used bid, event, tax, document-share, meeting, and government lures with URLs to executable payloads, including MsTeams.exe.
- The delivered executable dropped TrustConnectAgent.exe, which communicated with the TrustConnect C2. The platform also provided a PowerShell one-liner that ran a remote intermediate installation script; Proofpoint noted it might be used in ClickFix attacks.
- TrustConnect operators used branded installers for delivery and deployed follow-on remote-access software, including ScreenConnect and Level RMM. ScreenConnect installers were delivered from self-hosted servers, and Level RMM was deployed via an abused account.
- Defensive Notes
- The EV certificate used to sign TrustConnect malware was revoked on 6 February 2026, but the revocation was not backdated, so previously signed files remained valid.
- Proofpoint reported that coordinated remediation of TrustConnect infrastructure concluded at approximately 00:00 UTC on 17 February 2026.
- Proofpoint listed Emerging Threats rules 2067351–2067352 and 2067682–2067690 for TrustConnect domain and agent activity, and rules 2067801–2067806 for DocConnect domain and agent activity.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | adobe[.]caladzy[.]com | Identified as a payload-staging domain. |
| DOMAIN | ametax[.]net | Identified as a payload-staging domain. |
| DOMAIN | elev8souvenirs[.]com | Listed in the article’s example IOC set associated with the reported activity; its specific role is not stated. |
| DOMAIN | networkservice[.]cyou | DocConnect C2 domain. |
| DOMAIN | statementstview[.]online | Listed in the article’s example IOC set associated with the reported activity; its specific role is not stated. |
| DOMAIN | trustconnectsoftware[.]com | TrustConnect malware portal and C2 domain. |
| DOMAIN | vurul[.]click | Listed in the article’s example IOC set associated with the reported activity; its specific role is not stated. |
| DOMAIN | worldwide-www19[.]pages[.]dev | Listed in the article’s example IOC set associated with the reported activity; its specific role is not stated. |
| IPV4 | 178[.]128[.]69[.]245 | IP address of the TrustConnect C2 server. |
| SHA256 | 162c0d3e671ddf4f7f3ae5681da5272111eab6588bc53843cc604fc386634594 | SHA-256 hash identified as a DocConnect testing payload. |
| SHA256 | cee6895f7df01da489c10bf5b83770ceede79ed4e1c8c4f8ea9787a4d035c79b | SHA-256 hash of a TrustConnectAgent.exe malware sample. |
| SHA256 | cf85a4816715b8fa6c1eb5b50d1c70cfef116522742f6f1c77cb8689166b9f40 | SHA-256 hash of a MsTeams.exe malware sample. |
| URL | hxxp[:]//192[.]159[.]99[.]83/Bin/ScreenConnect[.]ClientSetup[.]msi?e=Access&y=Guest | Payload URL used to deliver a ScreenConnect installer. |
| URL | hxxp[:]//192[.]227[.]211[.]41:8040/Bin/ScreenConnect[.]ClientSetup[.]msi?e=Access&y=Guest | Payload URL used to deliver a ScreenConnect installer. |
| URL | hxxps[:]//aerobickarlaurbanovas[.]top/Bin/ScreenConnect[.]ClientSetup[.]msi?e=Access&y=Guest= | Payload URL used to deliver a ScreenConnect installer. |
| URL | hxxps[:]//memphiswawu[.]com/Bin/ScreenConnect[.]ClientSetup[.]msi?e=Access&y=Guest | Payload URL used to deliver a ScreenConnect installer. |
| URL | hxxps[:]//smallmartdirectintense[.]com/Bin/ScreenConnect[.]ClientSetup[.]msi?e=Access&y=Guest= | Payload URL used to deliver a ScreenConnect installer. |
| URL | hxxps[:]//stewise[.]top/Bin/ScreenConnect[.]ClientSetup[.]msi?e=Access&y=Guest | Payload URL used to deliver a ScreenConnect installer. |
MITRE ATT&CK
T1021 · Remote ServicesThe report describes RDP and remote-desktop functionality for controlling compromised devices.T1059.001 · PowerShellTrustConnect provided a PowerShell one-liner that ran a remote intermediate script to install the RAT.T1071.001 · Web ProtocolsThe malware communicated with its C2 using the web panel’s API over standard SSL/TLS, and its remote-desktop stream used WebSockets.T1105 · Ingress Tool TransferOperators delivered additional tools, including ScreenConnect installers, from payload URLs.T1204 · User ExecutionRecipients had to execute delivered files for them to drop TrustConnectAgent.exe.T1219 · Remote Access ToolsOperators deployed legitimate remote-access tools, including ScreenConnect and Level RMM, for follow-on access.T1553 · Subvert Trust ControlsThe operator used an Extended Validation certificate to sign malware, which Proofpoint said could help evade signature-based detections.T1566 · PhishingEmail campaigns used lures and URLs leading to malicious executables, including MsTeams.exe.
Malware
DocConnectand IP 178[.]128[.]69[.]245), but the actor showed resilience by pivoting to a new agent named DocConnect; the operation is linked to a Telegram handle seen in prior Redline activity.RedLineby pivoting to a new agent named DocConnect; the operation is linked to a Telegram handle seen in prior Redline activity.SHIELD OS v1.0but observed a pivot to a reworked platform and payload under the names DocConnect / SHIELD OS v1.0 using React/Supabase and SignalR.TrustConnectProofpoint identified a new malware-as-a-service (MaaS) called TrustConnect that masqueraded as a legitimate remote monitoring and management (RMM) tool, used an EV code signing certificate to sign branded installers,
Vendors
ConnectWiseProofpoint would like to thank our colleagues at ConnectWise ScreenConnect for collaborating on taking down abused instances.⯠LevelTrustConnect operators deployed follow-on legitimate remote-access tooling (ScreenConnect, Level RMM) from abused or pirated instances to enable handsâonâkeyboard activity.
Products
Level RMMTrustConnect operators deployed follow-on legitimate remote-access tooling (ScreenConnect, Level RMM) from abused or pirated instances to enable handsâonâkeyboard activity.LogMeIn Resolve03 February: observed messages contained URLs leading to an executable file which, if executed, installs LogMeIn Resolve.ScreenConnectTrustConnect operators deployed follow-on legitimate remote-access tooling (ScreenConnect, Level RMM) from abused or pirated instances to enable handsâonâkeyboard activity.