
Bitpanda-Themed Phishing Campaign Targets Credentials and Personal Data
Summary
Cofense analysts describe a Bitpanda impersonation campaign that used a lookalike domain and multi-step verification pages to harvest login credentials and personal information before redirecting users to the legitimate site.
Key points
- The phishing email impersonated Bitpanda and threatened to block users’ accounts to prompt them to click a “Start Update” button.
- The campaign used account-bitpanda[.]com, a lookalike domain registered shortly before analysis; the article identifies account.bitpanda[.]com as the legitimate domain.
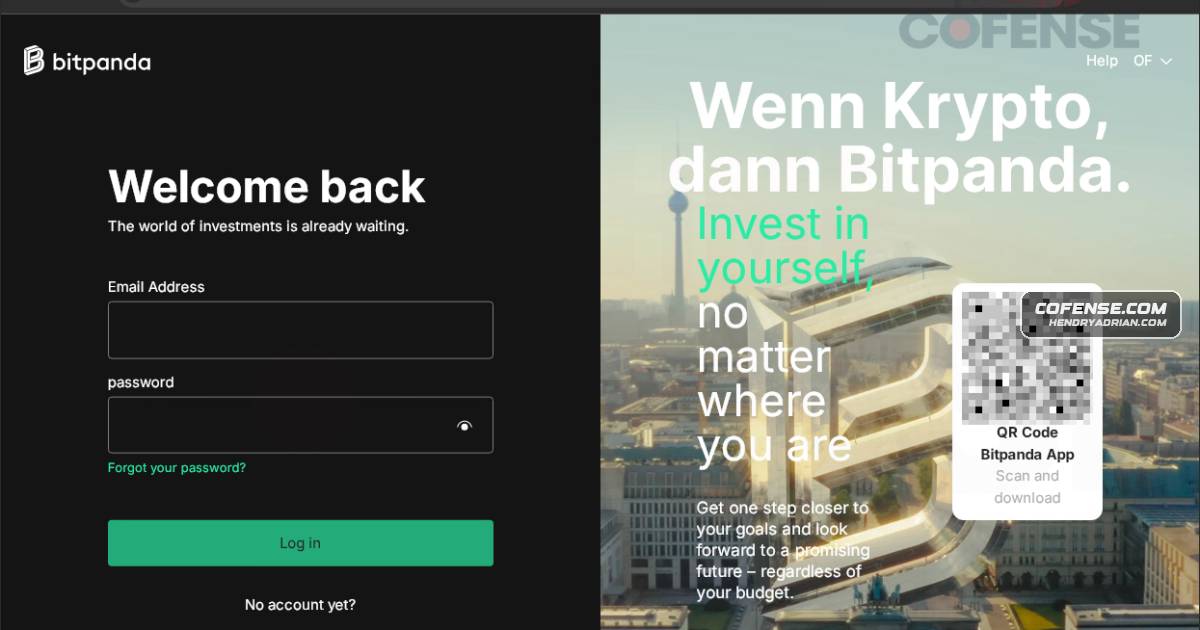
- Fake pages requested login credentials, then users’ names, phone numbers, addresses, and dates of birth under the guise of verification.
- A QR code linking to the official Bitpanda app download page helped make the fake site appear legitimate.
- After the final form, the site displayed a successful-verification message and redirected users to the real Bitpanda login page.
- Cofense says the campaign bypassed a secure email gateway but was detected and remediated by its Managed Phishing Remediation service.
Article Details
- Attack Vectors
- A phishing email impersonated Bitpanda and used a threat to block the recipient’s account to encourage clicking a “Start Update” link.
- The link led to account-bitpanda[.]com, a recently registered lookalike domain with replica Bitpanda pages that collected login credentials and personal information, including names, phone numbers, addresses, and dates of birth.
- After the information-collection steps, the phishing site redirected victims to the real Bitpanda login page.
- Defensive Notes
- The campaign bypassed a secure email gateway, but Cofense Managed Phishing Remediation detected and remediated it.
- Treat urgent account-blocking messages and verification links as suspicious; verify the destination domain before entering credentials or personal information.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | account-bitpanda[.]com | Lookalike phishing domain used to collect Bitpanda login credentials and personal information. |
MITRE ATT&CK
T1036 · MasqueradingThe campaign used account-bitpanda[.]com and replica pages to impersonate Bitpanda.T1204.002 · Malicious FileThe account-blocking scare message encouraged recipients to click the link and submit information.T1566.002 · Spearphishing LinkThe phishing email contained a link to the credential- and personal-information-harvesting site.
Vendors
BitpandaCofense PDC observed a Bitpanda-themed phishing campaign that used a deceptive, similarly named domain and highly convincing replica pages to harvest login credentials and multiple pieces of PII (name, phone, address,CofenseCofense PDC observed a Bitpanda-themed phishing campaign that used a deceptive, similarly named domain and highly convincing replica pages to harvest login credentials and multiple pieces of PII (name, phone, address,