
Wormable XMRig Campaign Uses BYOVD and a Time-Based Logic Bomb
Summary
Trellix describes a cryptojacking campaign using pirated-software lures, removable-media propagation and WinRing0x64.sys (CVE-2020-14979) to boost XMRig mining; its binary was set to self-decommission after Dec. 23, 2025.
Key points
- Trellix says pirated software bundles, including fake premium software installers, were used to deliver the miner.
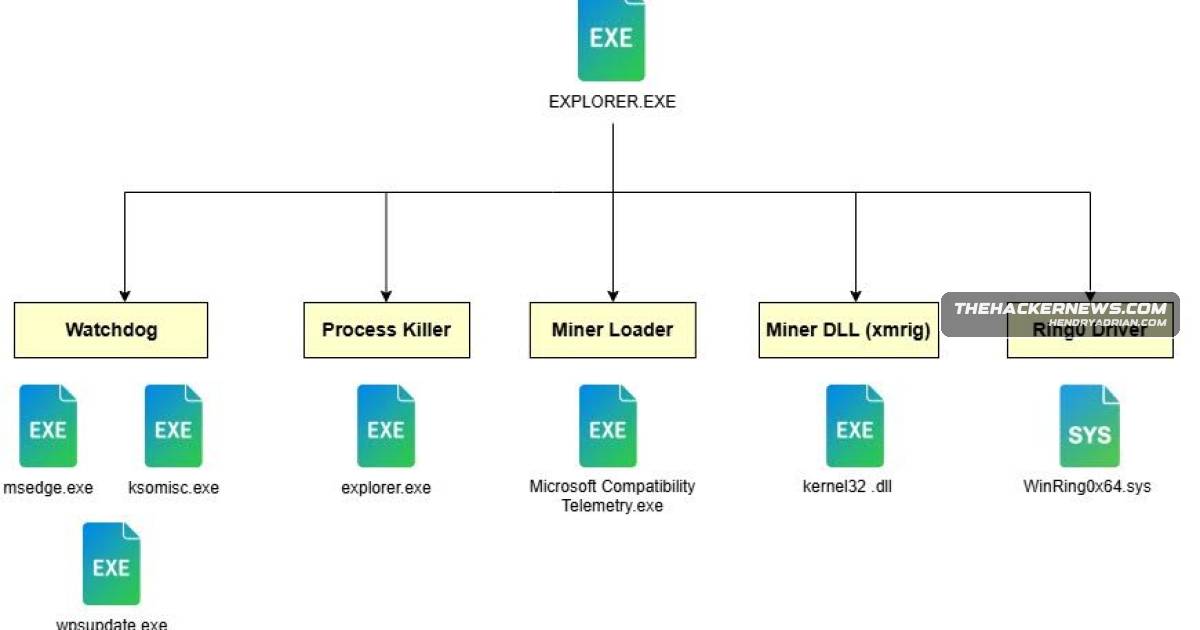
- A modular binary served as installer, watchdog, payload manager and cleaner, switching functions through command-line arguments.
- The malware used a legitimate Windows Telemetry service executable to sideload the miner DLL and deployed files for persistence and security-tool termination.
- The campaign used the vulnerable WinRing0x64.sys driver (CVE-2020-14979) for BYOVD privilege escalation; Trellix reports this increased RandomX hashrate by 15% to 50%.
- The miner spread through removable media, enabling worm-like propagation, including to air-gapped environments.
- A time-based logic bomb was set to trigger self-decommissioning after Dec. 23, 2025; Trellix observed mining activity in November 2025 and a spike on Dec. 8.
- In separate related reporting, Darktrace described React2Shell exploitation linked to XMRig deployment on more than 90 hosts, while WhoisXML API reported ILOVEPOOP scanning for vulnerable systems.
Article Details
- Attack Vectors
- Pirated software bundles advertise free premium software and deliver malware-laced executables.
- The campaign uses the vulnerable WinRing0x64.sys driver (CVE-2020-14979) to gain kernel-level privileges and increase mining performance.
- The miner spreads to removable media, enabling worm-like propagation to other systems.
- A separate React2Shell (CVE-2025-55182) exploitation report describes downloading a Python toolkit that runs a shell command to deploy an XMRig miner.
- The ILOVEPOOP toolkit scans for exposed systems vulnerable to React2Shell.
MITRE ATT&CK
T1046 · Network Service DiscoveryILOVEPOOP is used to scan for exposed systems vulnerable to React2Shell.T1059 · Command and Scripting InterpreterThe downloaded Python toolkit uses a shell command to run the XMRig miner.T1068 · Exploitation for Privilege EscalationThe malware uses WinRing0x64.sys and CVE-2020-14979 to escalate privileges to the kernel level.T1091 · Replication Through Removable MediaThe malware propagates to other systems through removable media.T1105 · Ingress Tool TransferThe React2Shell exploit activity downloads a Python toolkit used to deploy an XMRig miner.T1190 · Exploit Public-Facing ApplicationThe separate React2Shell activity exploits CVE-2025-55182 on exposed systems.T1204.002 · Malicious FileUsers are lured into downloading and running malware-laced executables bundled as pirated software.T1496 · Resource HijackingThe deployed XMRig miner uses compromised hosts’ CPU resources for cryptocurrency mining.T1574.002 · DLL Side-LoadingA legitimate Windows Telemetry service executable is used to sideload the miner DLL.
CVE
CVE-2020-14979Evga · Precision x1; Winring0 project · Winring0The operation leverages BYOVD via WinRing0x64.sys (CVE-2020-14979) to escalate privileges and boost RandomX hashrates, spreads like a worm via removable media, includes a December 23, 2025 time-based logic bomb forCVE-2025-55182Meta · react-server-dom-parcel; Meta · react-server-dom-turbopack; +1 more2025 time-based logic bomb for controlled decommissioning, and shows links to AI-aided React2Shell (CVE-2025-55182) exploits and the ILOVEPOOP scanning toolkit, per Trellix, Darktrace, and WhoisXML API.
People
Alex RonquilloWhoisXML API vice president of product who discussed ILOVEPOOP’s construction and its scanning activity.Aswath ATrellix researcher who analyzed the recovered dropper, persistence triggers, and mining payload in the campaign.Nathaniel BillDarktrace researcher who reported on malware exploiting React2Shell to download a Python toolkit and deploy an XMRig miner.Nathaniel JonesDarktrace researcher who reported on malware exploiting React2Shell to download a Python toolkit and deploy an XMRig miner.
Malware
Vendors
Darktraceto AI-aided React2Shell (CVE-2025-55182) exploits and the ILOVEPOOP scanning toolkit, per Trellix, Darktrace, and WhoisXML API.Trellixshows links to AI-aided React2Shell (CVE-2025-55182) exploits and the ILOVEPOOP scanning toolkit, per Trellix, Darktrace, and WhoisXML API.WhoisXML APIReact2Shell (CVE-2025-55182) exploits and the ILOVEPOOP scanning toolkit, per Trellix, Darktrace, and WhoisXML API.
Products
Tools
Countries
Industries
DefenseResearchers linked AI-assisted React2Shell (CVE-2025-55182) exploitation and the ILOVEPOOP scanning toolkit to the campaign, which targeted government, defense, finance, and industrial sectors.financeResearchers linked AI-assisted React2Shell (CVE-2025-55182) exploitation and the ILOVEPOOP scanning toolkit to the campaign, which targeted government, defense, finance, and industrial sectors.GovernmentResearchers linked AI-assisted React2Shell (CVE-2025-55182) exploitation and the ILOVEPOOP scanning toolkit to the campaign, which targeted government, defense, finance, and industrial sectors.IndustrialResearchers linked AI-assisted React2Shell (CVE-2025-55182) exploitation and the ILOVEPOOP scanning toolkit to the campaign, which targeted government, defense, finance, and industrial sectors.