
SURXRAT’s Latest Variant Conditionally Downloads a >23GB LLM Module
Summary
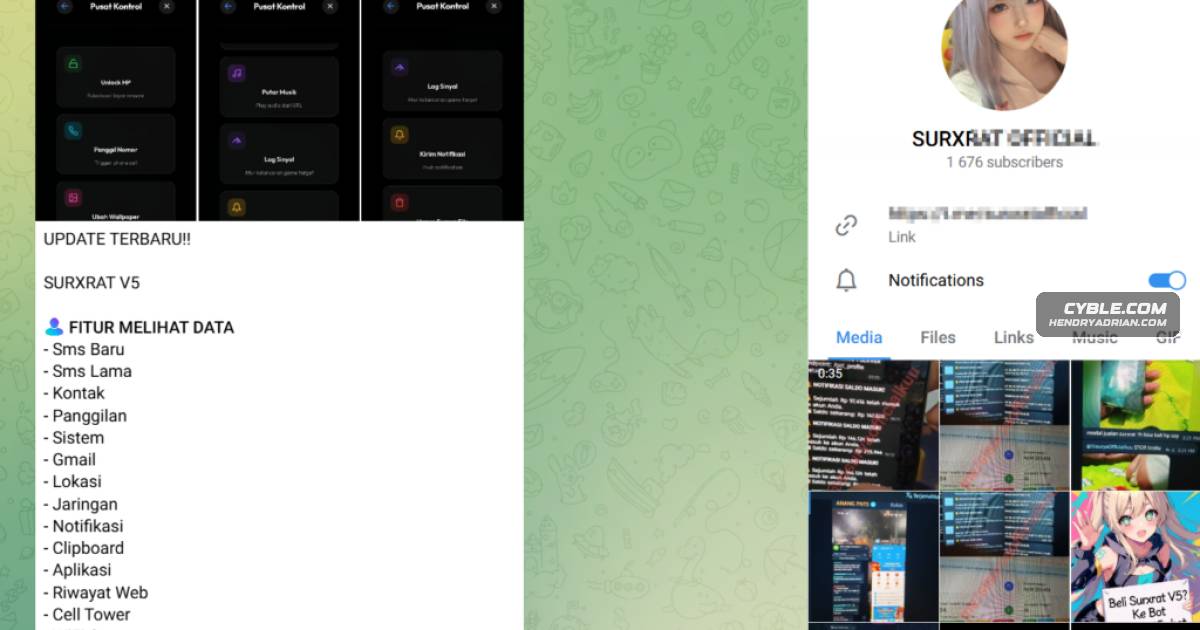
Cyble analyzes SURXRAT, which likely evolved from ArsinkRAT based on code similarities. The Android RAT abuses Accessibility, exfiltrates data via Firebase, enables remote control and screen locking, and conditionally downloads a >23GB LLM module.
Key points
- Cyble researchers identified more than 180 SURXRAT-related samples and describe an actively developed Android RAT marketed through a Telegram-based reseller and partner ecosystem.
- Code references and functional similarities suggest SURXRAT likely evolved from ArsinkRAT.
- SURXRAT prompts users for high-risk permissions, including Accessibility Services, and can use them for surveillance and automated remote actions.
- The RAT registers devices with UUIDs and sends data—including contacts, SMS, call logs, location, and device information—to a Firebase Realtime Database backend.
- Its remote commands support surveillance and device control, including audio and camera capture, calls and SMS, screen locking, and storage wiping.
- The latest analyzed variant conditionally downloads a >23GB LLM module when specified gaming apps are active or when target package names are provided by the backend. The article describes possible uses such as latency manipulation or future AI-driven functions as experimentation, not confirmed capabilities.
Article Details
- Attack Vectors
- SURXRAT is marketed through a Telegram-based MaaS ecosystem with reseller and partner licensing that enables affiliates to generate customized builds.
- The malware prompts users to grant high-risk permissions and enable Accessibility Services, which it uses for surveillance and remote actions.
- SURXRAT registers infected devices with a Firebase Realtime Database backend, polls for commands, and sends collected data to the backend.
- The malware conditionally downloads a large LLM module when specified gaming applications are active or when target package names are supplied by its backend.
- Defensive Notes
- Install apps only from trusted sources and avoid third-party app stores or links received through messages or social media.
- Do not install apps or grant permissions unless the app's legitimacy is established; be cautious of requests to enable Accessibility Services.
- Use multi-factor authentication for banking and financial apps, and install a mobile security application with real-time scanning.
- Keep Android and apps updated. If compromise is suspected, report it to the bank and local authorities, reset credentials, and perform a factory reset if necessary.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| URL | hxxps[:]//xrat-sisuriya-default-rtdb[.]firebaseio[.]com | Firebase C2 URL used for device registration, command polling, and data exfiltration. |
MITRE ATT&CK
T1414SURXRAT collects clipboard content.T1418SURXRAT retrieves the list of installed applications.T1420SURXRAT enumerates external storage and files.T1426SURXRAT collects device information, including device metadata.T1429SURXRAT can record audio using the device microphone.T1430SURXRAT collects the victim device's location.T1437.001SURXRAT communicates with its Firebase backend over HTTPS.T1533SURXRAT collects files from external storage.T1624.001SURXRAT registers a BOOT_COMPLETED broadcast receiver to activate the screen locker.T1629.001The article reports that SURXRAT prevents its uninstallation to maintain presence on the device.T1636.002SURXRAT collects call logs from the device.T1636.003SURXRAT collects contact data from the device.T1636.004SURXRAT reads SMS messages from the device.T1646SURXRAT sends collected victim data to its Firebase C2 backend.T1662SURXRAT can wipe external storage on a compromised device.
Malware
ArsinkRATRemote Access Trojan marketed via a Telegram-based MaaS ecosystem (SURXRAT V5) that evolved from ArsinkRAT, abuses Accessibility permissions, and uses a Firebase Realtime Database backend to exfiltrate extensiveSURXRATSURXRAT is an actively developed Android Remote Access Trojan marketed via a Telegram-based MaaS ecosystem (SURXRAT V5) that evolved from ArsinkRAT, abuses Accessibility permissions, and uses a Firebase Realtime
Products
AndroidSURXRAT is an actively developed Android Remote Access Trojan marketed via a Telegram-based MaaS ecosystem (SURXRAT V5) that evolved from ArsinkRAT, abuses Accessibility permissions, and uses a Firebase RealtimeFirebase Realtime Database(SURXRAT V5) that evolved from ArsinkRAT, abuses Accessibility permissions, and uses a Firebase Realtime Database backend to exfiltrate extensive user data and perform remote device control and locking.Free Fire MAX x JUJUTSU KAISENtriggered when specific gaming applications are active on the victim’s device, namely Free Fire MAX x JUJUTSU KAISEN (com.dts.freefiremax) and Free Fire x JUJUTSU KAISEN (com.dts.freefireth), or when theFree Fire x JUJUTSU KAISENactive on the victim’s device, namely Free Fire MAX x JUJUTSU KAISEN (com.dts.freefiremax) and Free Fire x JUJUTSU KAISEN (com.dts.freefireth), or when the malware receives alternative target package names dynamicallyHugging FaceThe latest variants conditionally download a >23GB LLM module from Hugging Face—triggered by specific game package names—indicating experimentation with AI-driven capabilities, performance manipulation, and expandedTelegramSURXRAT is an actively developed Android Remote Access Trojan marketed via a Telegram-based MaaS ecosystem (SURXRAT V5) that evolved from ArsinkRAT, abuses Accessibility permissions, and uses a Firebase Realtime