
BreachForums Seller Claims to Offer CEO’s OpenClaw Data and Root Access
Summary
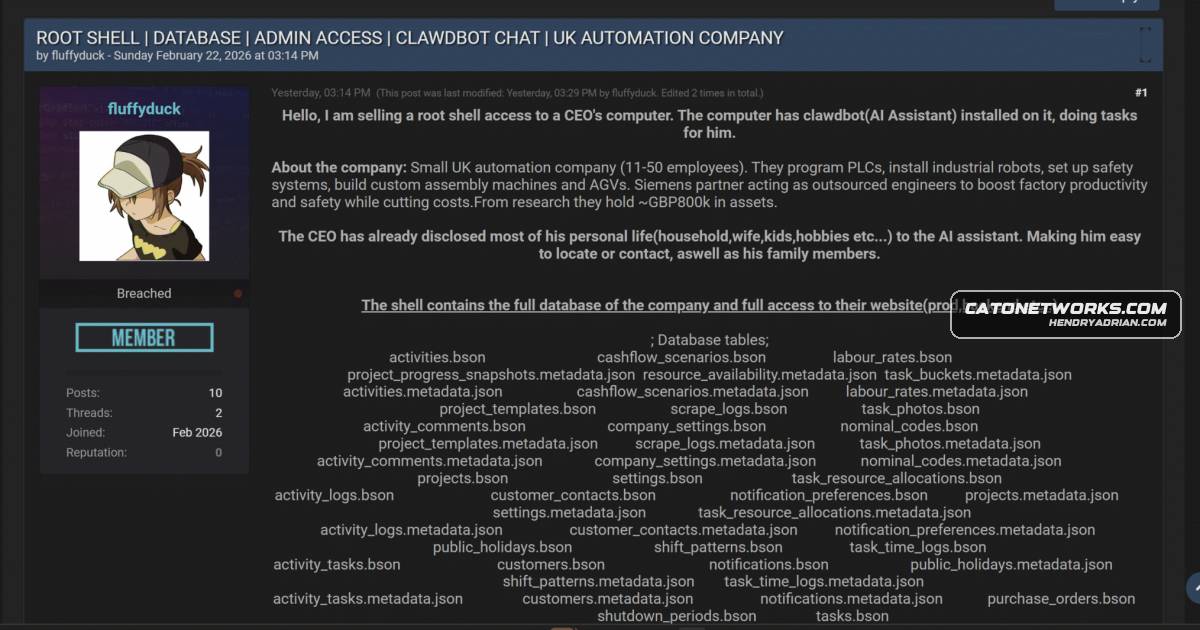
Cato CTRL reports that a BreachForums seller claims to offer root access to a UK automation-company CEO’s computer for $25,000, along with OpenClaw data and credentials. The listing is unverified.
Key points
- Cato says a BreachForums user named “fluffyduck” posted the offer on February 22, 2026; the access and data claims are not independently confirmed.
- The listing reportedly includes OpenClaw conversations, a company production database, Telegram bot credentials, and Trading 212 API keys.
- The article says OpenClaw runs locally with host access and stores conversations in plaintext Markdown files and secrets in a .env file.
- The article describes three OpenClaw vulnerabilities: CVE-2026-24763 (container escape), CVE-2026-25157 (OS command injection), and CVE-2026-25253 (token theft and gateway compromise).
- It cites more than 45,000 internet-facing instances, attributing the figure to Shodan, and 824 malicious ClawHub skills, attributing that figure to Koi.
- Cato recommends shadow AI discovery, DLP policies, and ZTNA controls to find unauthorized assistants and restrict their access to corporate resources.
Article Details
- Victim Organization
- Not disclosed
- Incident Type
- A BreachForums listing claimed to offer root shell access to a CEO's computer and access to the CEO's OpenClaw assistant and company data.
- Data Types Exposed
- Personal conversations and information
- Company production database and business information
- Telegram bot credentials
- Trading 212 API keys
- OpenClaw dashboard credentials
- Affected Records
- Not disclosed
- Affected Data Size
- Not disclosed
- Operational Impact
- The seller claimed to have root shell access, company database and website access, and access to the CEO's OpenClaw assistant. The article does not confirm the compromise or report operational disruption.
- Ransom Or Extortion
- The seller reportedly offered the access for $25,000 in Monero or Litecoin. No ransom demand or extortion of the victim is reported.
- Claim Status
- claimed
MITRE ATT&CK
T1059 · Command and Scripting InterpreterThe article describes command injection through unsanitized SSH target strings and arbitrary command execution as an OpenClaw vulnerability; it does not confirm this behavior occurred in the reported incident.T1078 · Valid AccountsThe listing reportedly included Telegram bot credentials, Trading 212 API keys, and OpenClaw dashboard credentials. The article does not confirm that these credentials were used to access services.T1190 · Exploit Public-Facing ApplicationThe article describes a malicious webpage stealing an authentication token and exploiting OpenClaw to bypass authentication and escape a container. It does not establish that this was the method used in the reported compromise.T1552 · Unsecured CredentialsThe article reports that OpenClaw stores conversations and secrets in plaintext files, including API keys in a .env file. This is described as an exposure risk, not confirmed evidence of how the seller obtained access.T1611 · Escape to HostThe article describes an OpenClaw Docker sandbox escape that could enable host command execution; it does not confirm this technique was used in the reported compromise.
CVE
CVE-2026-24763clawdbot · clawdbotMultiple high-severity CVEs with public exploits impact OpenClaw (CVE-2026-24763, CVE-2026-25157, CVE-2026-25253), enabling container escape, command injection, and token exfiltration.CVE-2026-25157openclaw · openclawMultiple high-severity CVEs with public exploits impact OpenClaw (CVE-2026-24763, CVE-2026-25157, CVE-2026-25253), enabling container escape, command injection, and token exfiltration.CVE-2026-25253OpenClaw · OpenClawMultiple high-severity CVEs with public exploits impact OpenClaw (CVE-2026-24763, CVE-2026-25157, CVE-2026-25253), enabling container escape, command injection, and token exfiltration.