
Threat Actors Abuse Windows File Explorer and WebDAV to Deliver RATs
Summary
Cofense details campaigns using Windows File Explorer and WebDAV links hosted on short-lived Cloudflare Tunnel demos to deliver RATs. 87% of observed reports delivered multiple RATs, including XWorm, Async RAT and DcRAT.
Key points
- The report says threat actors exploit File Explorer’s native WebDAV support to present remote files outside typical browser download flows, potentially bypassing some EDR controls.
- Campaigns use .url and .lnk shortcuts, UNC paths, and script chains to access remote WebDAV servers and download or run payloads.
- The observed servers use short-lived Cloudflare Tunnel demo instances on trycloudflare[.]com, which can make malicious activity harder to recognize and analyze.
- Cofense reports that 87% of observed Active Threat Reports using this tactic delivered multiple RATs; XWorm, Async RAT and DcRAT were among the common payloads.
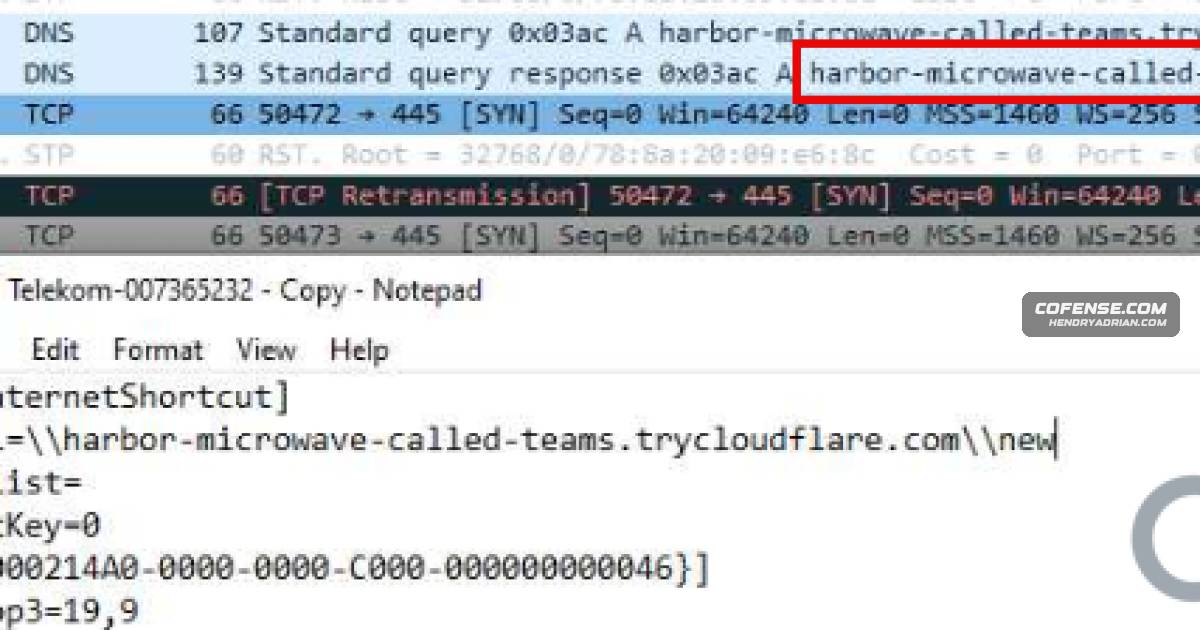
- Some URL shortcuts containing UNC paths can trigger DNS lookups and outbound connections when a user browses the directory containing them.
- The report recommends checking File Explorer’s address bar, using EDR behavioral detections for shortcuts that run remote files, and hunting for traffic to trycloudflare[.]com demo instances.
Article Details
- Attack Vectors
- Threat actors use .url and .lnk shortcuts, UNC paths, and direct File Explorer links to open remote WebDAV resources.
- LNK commands can use bitsadmin to download a WSH script from a WebDAV server and wscript to execute it.
- Campaigns host WebDAV servers and malware payloads on short-lived Cloudflare Tunnel demo domains under trycloudflare[.]com.
- The report says 87% of observed Active Threat Reports using this tactic delivered multiple RATs, including XWorm RAT, Async RAT, and DcRAT.
- Defensive Notes
- Educate users to check the Windows File Explorer address bar for unfamiliar remote addresses and to treat network-file warnings cautiously.
- Use EDR behavioral analysis to detect .url and .lnk files that execute files or commands from remote file servers.
- Threat hunt for network traffic to Cloudflare Tunnel demo instances on trycloudflare[.]com.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | discounted-pressed-lc-vcr[.]trycloudflare[.]com | Example Cloudflare Tunnel domain found in Active Threat Reports using the described delivery tactic. |
| DOMAIN | earl-dont-princess-bit[.]trycloudflare[.]com | Cloudflare Tunnel demo domain in an LNK example that accesses a remote WSH script. |
| DOMAIN | everything-teach-pearl-eat[.]trycloudflare[.]com | Cloudflare Tunnel demo domain used as a WebDAV host in a File Explorer link example. |
| DOMAIN | frontier-shops-timothy-cal[.]trycloudflare[.]com | Cloudflare Tunnel demo domain used in WebDAV delivery examples, including a WSH payload download. |
| DOMAIN | lose-croatia-acdbentity-lt[.]trycloudflare[.]com | Example Cloudflare Tunnel domain found in Active Threat Reports using the described delivery tactic. |
| DOMAIN | module-brush-sort-factory[.]trycloudflare[.]com | Cloudflare Tunnel demo domain identified as hosting a WebDAV server used in malware delivery. |
| DOMAIN | nasdaq-aged-sf-cheers[.]trycloudflare[.]com | Example Cloudflare Tunnel domain found in Active Threat Reports using the described delivery tactic. |
| DOMAIN | publicity-jenny-paintball-gilbert[.]trycloudflare[.]com | Example Cloudflare Tunnel domain found in Active Threat Reports using the described delivery tactic. |
| DOMAIN | skills-statute-alberta-demand[.]trycloudflare[.]com | Example Cloudflare Tunnel domain found in Active Threat Reports using the described delivery tactic. |
| DOMAIN | tiny-fixtures-glossary-advantage[.]trycloudflare[.]com | Example Cloudflare Tunnel domain found in Active Threat Reports using the described delivery tactic. |
| DOMAIN | whats-menu-familiar-zshops[.]trycloudflare[.]com | Example Cloudflare Tunnel domain found in Active Threat Reports using the described delivery tactic. |
| URL | hxxps[:]//frontier-shops-timothy-cal[.]trycloudflare[.]com/rec.wsh | Specific remote WSH script URL used in an example command that downloads the script before execution. |
MITRE ATT&CK
T1059 · Command and Scripting InterpreterThe example delivery chain executes a downloaded WSH script with wscript.exe; the script language is not specified.T1059.003 · Windows Command ShellAn example LNK command invokes cmd.exe to run bitsadmin and then execute the downloaded script.T1105 · Ingress Tool TransferAn example LNK command uses bitsadmin to download rec.wsh from a remote WebDAV host.T1204.001 · Malicious LinkVictims are tricked into opening WebDAV links in File Explorer through direct links or shortcut files.T1204.002 · Malicious FileThe delivery chains use .url and .lnk files to prompt victims to access or run remote files.
Malware
Async RATCampaigns use .url and .lnk shortcuts, UNC paths, and script chains to fetch payloads such as XWorm, Async RAT, and DcRAT from trycloudflare[.]com instancesDCRatCampaigns use .url and .lnk shortcuts, UNC paths, and script chains to fetch payloads such as XWorm, Async RAT, and DcRAT from trycloudflare[.]com instancesXWormSome of the most popular RATs include XWorm RAT, Async RAT, and DcRAT.
Vendors
Products
Cloudflare TunnelThis report describes how threat actors abuse WebDAV access via Windows File Explorer to deliver remote access trojans (RATs) by hosting payloads on short-lived Cloudflare Tunnel demo domains.Windows File ExplorerThis report describes how threat actors abuse WebDAV access via Windows File Explorer to deliver remote access trojans (RATs) by hosting payloads on short-lived Cloudflare Tunnel demo domains.