
ReliaQuest Details ShinyHunters’ Subdomain Impersonation and AiTM Phishing
Summary
ReliaQuest reports that ShinyHunters is combining subdomain impersonation, phone-guided mobile AiTM phishing, and outsourced vishing to steal SSO sessions and access SaaS data; it recommends stronger MFA and rapid session containment.
Key points
- ReliaQuest attributes the observed domains to ShinyHunters with high confidence, citing hands-on use during vishing, intrusion sequences consistent with public reporting, and clustered registration patterns.
- The group places organization branding in subdomains on generic, SSO-themed registered domains, potentially evading controls focused on newly registered or lookalike domains.
- Observed AiTM phishing kits proxy login flows to capture credentials, MFA challenges, and authenticated sessions during phone-guided, mobile-first lures.
- ReliaQuest says targets often opened lures from mobile devices and, in several cases, outside typical corporate egress, reducing visibility to some enterprise controls.
- The group is likely reusing exposed CRM, ERP, and HR data to select targets and make social-engineering pretexts more credible.
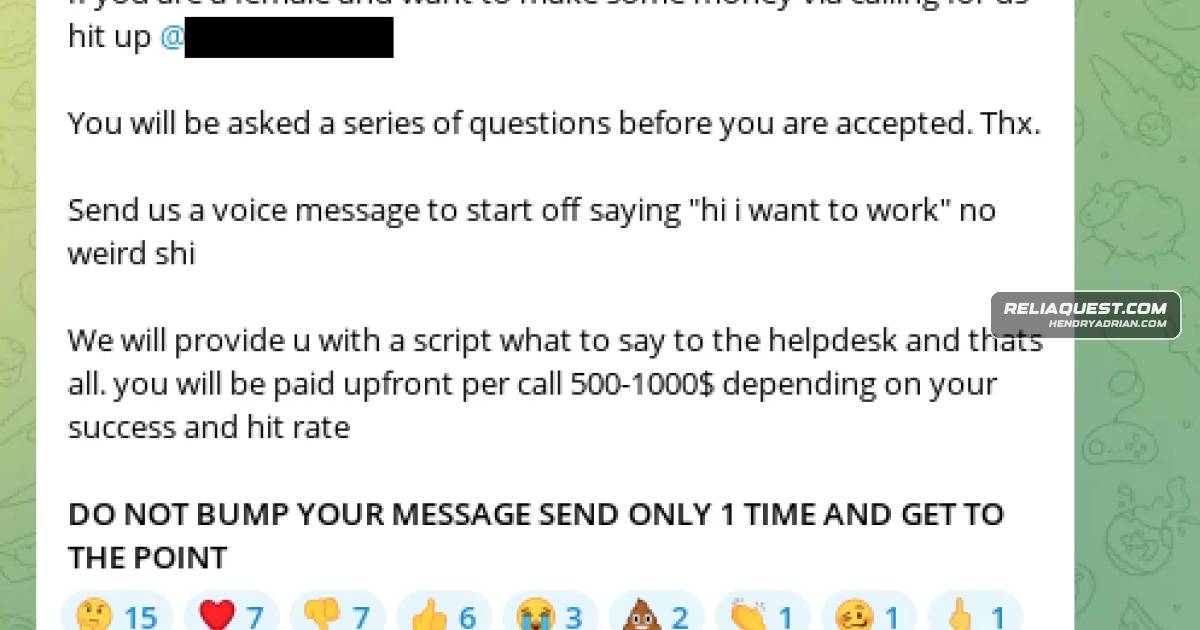
- ReliaQuest observed recruitment of voice operators and advertised paid spam and disruption services as part of ShinyHunters’ “SLH Operations Centre.”
- Recommended defenses include phishing-resistant MFA, stronger help-desk and MFA-reset verification, SaaS and identity telemetry, and rapid session revocation.
Article Details
- Attack Vectors
- ShinyHunters uses organization-branded subdomains on generic SSO- or login-themed domains to host phishing pages and evade detections focused on registered domains.
- Phone-guided, mobile-first adversary-in-the-middle phishing proxies SSO login flows to capture credentials, MFA challenges, and authenticated sessions.
- Operators use help-desk or support pretexts to guide users through authentication and MFA, and may exploit help-desk-driven MFA resets or re-enrollment.
- The group likely reuses previously exposed CRM, ERP, HR, and productivity data to identify and socially engineer employees positioned to approve access or reset credentials.
- ShinyHunters outsources call-center-style vishing and pressure tasks, including email bombing, call flooding, and SMS spamming.
- Defensive Notes
- Require phishing-resistant MFA, such as FIDO2 or WebAuthn, and apply risk-based step-up authentication or session binding where feasible.
- Harden help-desk identity verification and add controls to MFA reset and re-enrollment workflows.
- Monitor identity and SaaS audit telemetry for anomalous sign-ins, new MFA enrollment, unusual access, and bulk downloads; rapidly revoke suspicious sessions and disable compromised accounts.
- Apply conditional access to sensitive SaaS applications and restrict access from unmanaged or untrusted devices and locations where possible.
- Improve visibility into mobile sign-ins and sessions, and supplement domain monitoring with URL-level detection for branded subdomain lures.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | access-terms[.]com | The article identifies this domain family as targeting UK organizations in the subdomain-impersonation activity. |
| DOMAIN | acess-terms[.]com | Listed as a subdomain-impersonation domain used to host phishing pages and AiTM kits. |
| DOMAIN | desk-okta[.]com | Listed as a subdomain-impersonation domain used to host phishing pages and AiTM kits. |
| DOMAIN | help-okta[.]com | Listed as a subdomain-impersonation domain used to host phishing pages and AiTM kits. |
| DOMAIN | lock-okta[.]com | Listed as a subdomain-impersonation domain used to host phishing pages and AiTM kits. |
| DOMAIN | okta[.]domains | Listed as a subdomain-impersonation domain used to host phishing pages and AiTM kits. |
| DOMAIN | okta[.]guide | Listed as a phishing and AiTM domain; the article reports it is associated with targeting health care and pharmaceutical brands. |
| DOMAIN | prod-okta[.]com | Listed as a subdomain-impersonation domain used to host phishing pages and AiTM kits. |
| DOMAIN | safe-okta[.]com | Listed as a subdomain-impersonation domain used to host phishing pages and AiTM kits. |
| DOMAIN | setup-okta[.]com | Listed as a subdomain-impersonation domain used to host phishing pages and AiTM kits. |
| DOMAIN | sso[.]guide | Listed as a phishing and AiTM domain; the article reports it is associated with targeting health care and pharmaceutical brands. |
MITRE ATT&CK
T1078 · Valid AccountsAttackers use captured credentials or valid SSO sessions to access SaaS applications.T1098 · Account ManipulationThe article describes help-desk-driven MFA resets and MFA re-enrollment as routes to account access.T1557 · Adversary-in-the-MiddleAiTM phishing kits proxy SSO login flows to capture credentials, MFA challenges, and authenticated sessions in real time.T1566 · PhishingShinyHunters uses phone- and SMS-driven phishing and help-desk pretexts to direct users to impersonation subdomains.T1567 · Exfiltration Over Web ServiceAttackers use captured authenticated sessions to access and exfiltrate SaaS data.T1589 · Gather Victim Identity InformationThe group likely reuses exposed CRM, ERP, and HR records to identify employees and craft social-engineering pretexts.
Threat Actors
Scattered SpiderThe article says the subdomain-impersonation patterns resemble tactics seen from Scattered Spider and notes similarities in vishing campaigns, while stating that direct coordination with ShinyHunters is unclear.ShinyHuntersReliaQuest attributes the subdomain impersonation and phone-guided AiTM activity to ShinyHunters with high confidence. The article says the group appears to be reusing exposed SaaS data and outsourcing vishing and pressure tasks.