
ScarCruft Campaign Uses Cloud Services and Removable Media to Reach Air-Gapped Systems
Summary
Zscaler ThreatLabz attributes the Ruby Jumper campaign to ScarCruft. Its malware uses Zoho WorkDrive for C2 and removable media to transfer commands and data between internet-connected and air-gapped systems.
Key points
- The campaign begins with a malicious LNK file that runs PowerShell to extract multiple embedded payloads.
- RESTLEAF runs in memory, uses Zoho WorkDrive for C2, and downloads shellcode that is executed through process injection.
- SNAKEDROPPER installs a Ruby runtime, establishes persistence with a scheduled task, and deploys THUMBSBD and VIRUSTASK.
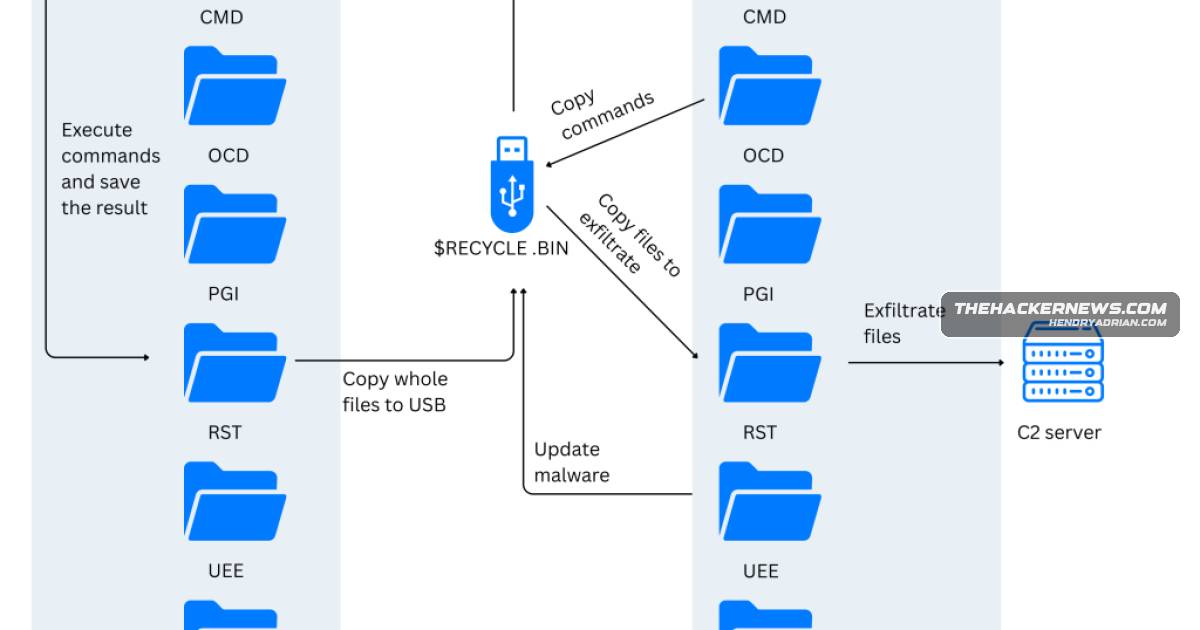
- THUMBSBD uses removable media to relay commands and data between connected and air-gapped systems; it can also harvest system information and exfiltrate files.
- VIRUSTASK uses removable media to propagate to air-gapped systems, while THUMBSBD can deliver FOOTWINE and BLUELIGHT.
- FOOTWINE supports keylogging and audio and video capture; BLUELIGHT uses cloud providers for C2 and file operations.
Article Details
- Attack Vectors
- A victim opening a malicious LNK file triggers PowerShell, which extracts embedded payloads and advances the infection chain.
- RESTLEAF authenticates to Zoho WorkDrive with an access token, downloads shellcode, and uses process injection to deploy SNAKEDROPPER.
- THUMBSBD and VIRUSTASK use removable media to move commands, data, or malware between internet-connected and air-gapped systems.
MITRE ATT&CK
T1053.005 · Scheduled TaskSNAKEDROPPER establishes persistence using a scheduled task.T1055 · Process InjectionRESTLEAF executes downloaded shellcode through process injection.T1056.001 · KeyloggingFOOTWINE includes keylogging capabilities.T1059.001 · PowerShellThe LNK launches PowerShell to locate itself and extract embedded payloads; later stages also launch PowerShell.T1082 · System Information DiscoveryTHUMBSBD can harvest system information.T1083 · File and Directory DiscoveryBLUELIGHT can enumerate the file system.T1091 · Replication Through Removable MediaTHUMBSBD and VIRUSTASK use removable media to transfer commands, data, or malware to air-gapped systems.T1102.002 · Bidirectional CommunicationRESTLEAF uses Zoho WorkDrive for C2, while BLUELIGHT uses cloud services to receive commands and communicate.T1105 · Ingress Tool TransferRESTLEAF downloads shellcode through Zoho WorkDrive, and THUMBSBD can download a secondary payload from a remote server.T1113 · Screen CaptureFOOTWINE can take screenshots.T1123 · Audio CaptureFOOTWINE can capture audio for surveillance.T1125 · Video CaptureFOOTWINE can capture video for surveillance.T1140 · Deobfuscate/Decode Files or InformationThe PowerShell stages carve embedded payloads from the LNK, and shellcode is decrypted before loading.T1204.002 · Malicious FileThe infection chain begins when a victim opens the malicious LNK file.T1567.002 · Exfiltration to Cloud StorageBLUELIGHT uses cloud services to upload files.
People
Threat Actors
Malware
BLUELIGHTand deploy a multi-stage toolset including RESTLEAF, SNAKEDROPPER, THUMBSBD, VIRUSTASK, FOOTWINE, and BLUELIGHT.FOOTWINEpayloads and deploy a multi-stage toolset including RESTLEAF, SNAKEDROPPER, THUMBSBD, VIRUSTASK, FOOTWINE, and BLUELIGHT.RESTLEAFLNK file and embedded PowerShell to carve multiple payloads and deploy a multi-stage toolset including RESTLEAF, SNAKEDROPPER, THUMBSBD, VIRUSTASK, FOOTWINE, and BLUELIGHT.SNAKEDROPPERembedded PowerShell to carve multiple payloads and deploy a multi-stage toolset including RESTLEAF, SNAKEDROPPER, THUMBSBD, VIRUSTASK, FOOTWINE, and BLUELIGHT.THUMBSBDPowerShell to carve multiple payloads and deploy a multi-stage toolset including RESTLEAF, SNAKEDROPPER, THUMBSBD, VIRUSTASK, FOOTWINE, and BLUELIGHT.VIRUSTASKto carve multiple payloads and deploy a multi-stage toolset including RESTLEAF, SNAKEDROPPER, THUMBSBD, VIRUSTASK, FOOTWINE, and BLUELIGHT.
Vendors
Backblazemalware weaponizes legitimate cloud providers, including Google Drive, Microsoft OneDrive, pCloud, and BackBlaze, for C2 to run arbitrary commands, enumerate the file system, download additional payloads, uploadGoogleThe malware weaponizes legitimate cloud providers, including Google Drive, Microsoft OneDrive, pCloud, and BackBlaze, for C2 to run arbitrary commands, enumerate the file system, download additional payloads, uploadMicrosoftThe malware weaponizes legitimate cloud providers, including Google Drive, Microsoft OneDrive, pCloud, and BackBlaze, for C2 to run arbitrary commands, enumerate the file system, download additional payloads, uploadpCloudThe malware weaponizes legitimate cloud providers, including Google Drive, Microsoft OneDrive, pCloud, and BackBlaze, for C2 to run arbitrary commands, enumerate the file system, download additional payloads, uploadZohoNotably, RESTLEAF abuses Zoho WorkDrive for C2 communications while THUMBSBD and VIRUSTASK weaponize removable media to bridge internet-connected and air-gapped systems for surveillance and data exfiltration.
Products
BackBlazemalware weaponizes legitimate cloud providers, including Google Drive, Microsoft OneDrive, pCloud, and BackBlaze, for C2 to run arbitrary commands, enumerate the file system, download additional payloads, uploadGoogle DriveThe malware weaponizes legitimate cloud providers, including Google Drive, Microsoft OneDrive, pCloud, and BackBlaze, for C2 to run arbitrary commands, enumerate the file system, download additional payloads, uploadMicrosoft OneDriveThe malware weaponizes legitimate cloud providers, including Google Drive, Microsoft OneDrive, pCloud, and BackBlaze, for C2 to run arbitrary commands, enumerate the file system, download additional payloads, uploadpCloudThe malware weaponizes legitimate cloud providers, including Google Drive, Microsoft OneDrive, pCloud, and BackBlaze, for C2 to run arbitrary commands, enumerate the file system, download additional payloads, uploadZoho WorkDriveNotably, RESTLEAF abuses Zoho WorkDrive for C2 communications while THUMBSBD and VIRUSTASK weaponize removable media to bridge internet-connected and air-gapped systems for surveillance and data exfiltration.