
Andariel Profile Details DPRK Espionage and Ransomware Operations
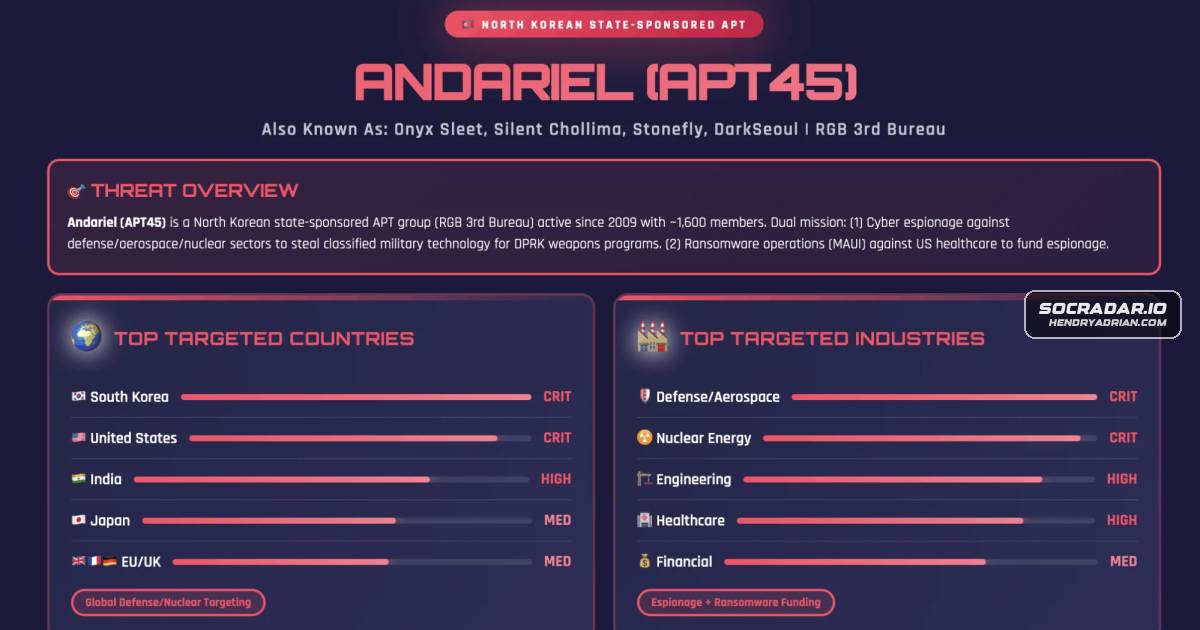
Summary
The profile describes Andariel as a DPRK-linked group conducting espionage and revenue-driven operations. It outlines the group’s access methods, malware, credential theft, data exfiltration and ransomware, and recommends defenses.
Key points
- Researchers assess Andariel as a DPRK-linked unit under the Lazarus umbrella, with espionage and financially motivated operations.
- The article describes exploitation of exposed systems, including use of CVE-2021-44228, alongside spear-phishing and watering-hole attacks.
- Post-compromise activity includes credential dumping and lateral movement using native Windows tools and remote services.
- The profile says operators stage and upload data, and may use ransomware such as Maui and SHATTEREDGLASS for extortion.
- It describes malware including DTrack, TigerRAT, EarlyRat, Atharvan and Dora RAT, with techniques such as process hollowing and DLL side-loading.
- Recommended defenses include prompt patching, MFA, network segmentation, endpoint monitoring, protocol monitoring and offline backups.
Article Details
- Attack Vectors
- Exploitation of internet-facing systems, including Log4Shell and vulnerabilities affecting VMware Horizon, Apache Tomcat, and on-premises Microsoft SharePoint.
- Spear-phishing using job-seeking lures and ZIP attachments containing LNK files or HTA scripts.
- Compromised watering-hole websites used to distribute malware to visitors from targeted sectors.
- Credential dumping followed by lateral movement using RDP, SSH, and SMB.
- Local staging and compression of collected data, followed by uploads to cloud storage or C2 tunneling; some operations proceed to ransomware deployment.
- Defensive Notes
- Rapidly patch critical vulnerabilities, prioritizing externally exposed assets and high-privilege services.
- Enforce MFA across user and administrative accounts, and audit suspicious account creation.
- Segment critical infrastructure and sensitive repositories; restrict east-west movement and administrative shares.
- Use endpoint monitoring to detect LSASS memory access, tunneling and proxy utilities, and abuse of vulnerable signed drivers.
- Monitor internal RDP and SMB traffic, apply least privilege, and maintain immutable offline backups.
MITRE ATT&CK
T1003 · OS Credential DumpingMimikatz, ProcDump, and CredentialsFileView were used to extract credentials from LSASS memory and registry stores.T1021 · Remote ServicesHarvested credentials enabled lateral access through RDP, SSH, and SMB.T1036 · MasqueradingAtharvan disguised C2 traffic as legitimate Microsoft update traffic.T1047 · Windows Management InstrumentationThe group used WMI as a living-off-the-land mechanism for remote execution and management.T1055.012 · Process HollowingNewer DTrack variants used process hollowing against legitimate processes such as explorer.exe.T1059.001 · PowerShellThe group abused PowerShell to execute payloads and reduce detection risk.T1071.001 · Web ProtocolsTigerRAT used encrypted HTTP-like communications.T1074 · Data StagedCollected data was staged locally and compressed before transfer.T1189 · Drive-by CompromiseCompromised watering-hole websites distributed malware to visitors from targeted sectors.T1190 · Exploit Public-Facing ApplicationAndariel exploited N-day vulnerabilities, including CVE-2021-44228, against VMware Horizon and other internet-facing services.T1486 · Data Encrypted for ImpactAndariel deployed Maui and SHATTEREDGLASS ransomware to encrypt systems after data theft.T1566.001 · Spearphishing AttachmentSpear-phishing lures impersonated recruiters or reputable organizations and delivered ZIP archives containing LNK files or HTA scripts.T1567 · Exfiltration Over Web ServiceOperators uploaded stolen data to cloud storage services such as MEGA using WinSCP and PuTTY.T1572 · Protocol Tunneling3Proxy, PLINK, and Stunnel were used to tunnel C2 traffic over legitimate protocols.T1574.001 · DLLDora RAT was delivered through DLL side-loading via WinRAR SFX.
CVE
Threat Actors
AndarielThe article describes Andariel as a North Korea-linked RGB cyber cluster assessed by researchers as a Lazarus sub-cluster. It attributes espionage, ransomware deployment, cryptocurrency theft, and other intrusions to the group.APT45Listed by the article as a vendor tracking alias for Andariel.Dark SeoulListed by the article as an alias used by researchers for Andariel.Onyx SleetListed by the article as a vendor tracking alias for Andariel.PlutoniumListed by the article as an alias used by researchers for Andariel.Silent ChollimaListed by the article as a vendor tracking alias for Andariel.StoneflyListed by the article as a vendor tracking alias for Andariel.WassoniteListed by the article as an alias used by researchers for Andariel.
Malware
Atharvan[T1036 ] Masquerading – C2 traffic and components were disguised as legitimate update traffic to avoid detection (‘Atharvan: … disguising C2 traffic as legitimate Microsoft update traffic.’)Dora RAT[T1574.001 ] DLL Side-Loading – DLL side-loading techniques were used to load malicious payloads (e.g., Dora RAT via WinRAR SFX) (‘Dora RAT (DLL side-loading via WinRAR SFX)’)DTrackThe group uses vulnerability exploitation, spear-phishing, living-off-the-land techniques, credential dumping, C2 tunneling and strains like Maui and DTrack to both collect intelligence and extract funds.DurianBeacon[Malware ] observed families and payloads – Maui, DTrack, and 6 more families including TigerRAT, EarlyRat, Atharvan, Dora RAT, DurianBeacon, NukeSpedEarlyRAT[Malware ] observed families and payloads – Maui, DTrack, and 6 more families including TigerRAT, EarlyRat, Atharvan, Dora RAT, DurianBeacon, NukeSpedMauiThe group uses vulnerability exploitation, spear-phishing, living-off-the-land techniques, credential dumping, C2 tunneling and strains like Maui and DTrack to both collect intelligence and extract funds.NukeSped RAT[T1112 ] Modify Registry – Some malware families stored configuration in the registry as part of persistence and configuration management (‘NukeSped lineage malware with registry-based configuration storage.’)SHATTEREDGLASSWhen aligned with regime priorities, Andariel pivots to ransomware and extortion (Maui, SHATTEREDGLASS) after data theft to maximize leverage and revenue.TigerRAT[T1071.001 ] Application Layer Protocol: Web Protocols – Malware used encrypted HTTP-like communications for C2 (e.g., TigerRAT) (‘TigerRAT: … encrypted HTTP-like communications.’)
Vendors
Microsoft(Log4Shell) affecting VMware Horizon, as well as vulnerabilities in Apache Tomcat and on-premises Microsoft SharePoint servers.’)VMwarePublic-Facing Application – Andariel leveraged N-day flaws including CVE-2021-44228 (Log4Shell) against VMware Horizon and other internet-facing services (‘leveraged N-day flaws, including CVE-2021-44228 (Log4Shell)
Products
Apache Tomcatflaws, including CVE-2021-44228 (Log4Shell) affecting VMware Horizon, as well as vulnerabilities in Apache Tomcat and on-premises Microsoft SharePoint servers.’)Microsoft SharePoint(Log4Shell) affecting VMware Horizon, as well as vulnerabilities in Apache Tomcat and on-premises Microsoft SharePoint servers.’)Microsoft Windows(‘spear-phishing…impersonating recruiters or reputable organizations…ZIP archives containing Microsoft Windows Shortcut (LNK) files or HTML Application (HTA) scripts.’)VMware HorizonApplication – Andariel leveraged N-day flaws including CVE-2021-44228 (Log4Shell) against VMware Horizon and other internet-facing services (‘leveraged N-day flaws, including CVE-2021-44228 (Log4Shell)
Tools
3proxyData staging and exfiltration often use local compression and cloud uploads (MEGA, WinSCP/Putty), with C2 traffic tunneled via 3Proxy, PLINK, and Stunnel to mask communications.CredentialsFileView[T1003 ] Credential Dumping – Tools like Mimikatz, ProcDump, and CredentialsFileView were used to extract credentials from LSASS memory and registry stores (‘tools like Mimikatz, ProcDump, and NirSoft’sMimikatzPost-compromise activity emphasizes credential access and lateral movement using LotL tools (PowerShell, WMI), credential dumping (Mimikatz, ProcDump), and remote services (RDP/SSH/SMB).PlinkData staging and exfiltration often use local compression and cloud uploads (MEGA, WinSCP/Putty), with C2 traffic tunneled via 3Proxy, PLINK, and Stunnel to mask communications.ProcDumpPost-compromise activity emphasizes credential access and lateral movement using LotL tools (PowerShell, WMI), credential dumping (Mimikatz, ProcDump), and remote services (RDP/SSH/SMB).PuTTYData staging and exfiltration often use local compression and cloud uploads (MEGA, WinSCP/Putty), with C2 traffic tunneled via 3Proxy, PLINK, and Stunnel to mask communications.StunnelData staging and exfiltration often use local compression and cloud uploads (MEGA, WinSCP/Putty), with C2 traffic tunneled via 3Proxy, PLINK, and Stunnel to mask communications.WinSCPData staging and exfiltration often use local compression and cloud uploads (MEGA, WinSCP/Putty), with C2 traffic tunneled via 3Proxy, PLINK, and Stunnel to mask communications.
Countries
JapanThe group targets defense, nuclear, aerospace, healthcare, financial institutions, and software/ERP supply chains across South Korea, the U.S., Japan, Europe, and parts of Asia.North KoreaAndariel is a North Korea–linked RGB cyber cluster operating under the Lazarus umbrella that blends strategic espionage against defense, nuclear, aerospace, and supply-chain targets with revenue-driven operations suchSouth KoreaThe group targets defense, nuclear, aerospace, healthcare, financial institutions, and software/ERP supply chains across South Korea, the U.S., Japan, Europe, and parts of Asia.United StatesThe group targets defense, nuclear, aerospace, healthcare, financial institutions, and software/ERP supply chains across South Korea, the U.S., Japan, Europe, and parts of Asia.
Industries
Aerospacecluster operating under the Lazarus umbrella that blends strategic espionage against defense, nuclear, aerospace, and supply-chain targets with revenue-driven operations such as ransomware and cryptocurrency theft.DefenseRGB cyber cluster operating under the Lazarus umbrella that blends strategic espionage against defense, nuclear, aerospace, and supply-chain targets with revenue-driven operations such as ransomware andEnergyIT Services, Energy, DefenseEngineeringThe group targets defense contractors, nuclear engineering firms, financial institutions, healthcare providers, and software vendors.HealthcareThe group targets defense, nuclear, aerospace, healthcare, financial institutions, and software/ERP supply chains across South Korea, the U.S., Japan, Europe, and parts of Asia.nuclearRGB cyber cluster operating under the Lazarus umbrella that blends strategic espionage against defense, nuclear, aerospace, and supply-chain targets with revenue-driven operations such as ransomware and cryptocurrencysemiconductorIn South Korea and Japan, it concentrates on defense manufacturers, telecommunications providers, semiconductor firms, and engineering companies.SoftwareThe group targets defense, nuclear, aerospace, healthcare, financial institutions, and software/ERP supply chains across South Korea, the U.S., Japan, Europe, and parts of Asia.TelecommunicationsIn South Korea and Japan, it concentrates on defense manufacturers, telecommunications providers, semiconductor firms, and engineering companies.