
Arctic Wolf Links SloppyLemming to Dual-Malware Campaign in Pakistan and Bangladesh
Summary
Arctic Wolf reports that SloppyLemming targeted organizations in Pakistan and Bangladesh from January 2025 to January 2026, using phishing and two malware chains to deploy the BurrowShell backdoor and a Rust-based keylogger.
Key points
- Arctic Wolf attributes activity from January 2025 to January 2026 to SloppyLemming, targeting government and critical-infrastructure organizations in Pakistan and Bangladesh.
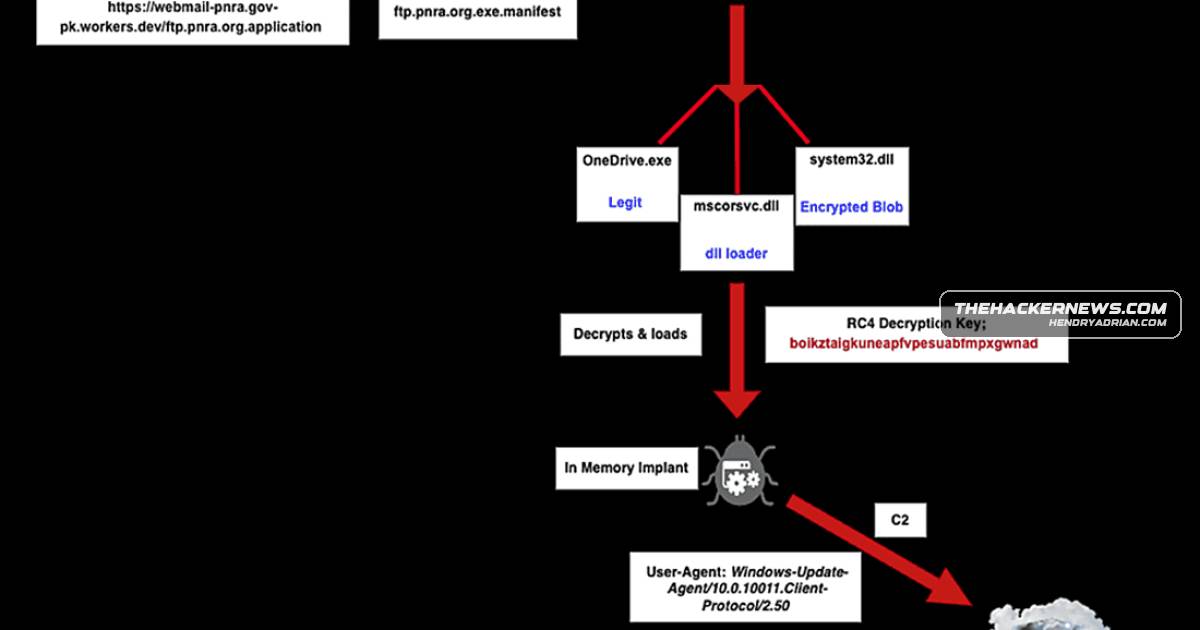
- One chain used PDF lures leading to ClickOnce manifests and DLL side-loading to execute BurrowShell; another used macro-enabled Excel documents to deliver a Rust-based keylogger.
- BurrowShell supports file manipulation, screenshots, remote shells, and SOCKS proxying; its command-and-control traffic reportedly masquerades as Windows Update and uses RC4 encryption.
- The keylogger chain also includes port scanning and network enumeration capabilities.
- Arctic Wolf identified 112 Cloudflare Workers domains used during the period, compared with 13 flagged by Cloudflare in September 2024.
- The SloppyLemming attribution is based on infrastructure and targeting patterns, Havoc C2 use, and DLL side-loading; some ClickOnce tradecraft overlaps with a SideWinder campaign reported by Trellix.
Article Details
- Attack Vectors
- Spear-phishing emails delivered PDF lures and macro-enabled Excel documents.
- URLs in PDF decoys led victims to ClickOnce application manifests.
- A malicious loader was executed through DLL side-loading to decrypt and run the BurrowShell shellcode implant.
- Malicious Excel macros dropped a Rust-based keylogger.
MITRE ATT&CK
T1036 · MasqueradingBurrowShell disguised its command-and-control traffic as Windows Update service communications.T1046 · Network Service DiscoveryThe keylogger malware also included port-scanning functionality.T1056.001 · KeyloggingThe second attack chain deployed a keylogger for information theft.T1090 · ProxyBurrowShell provided SOCKS proxy capabilities for network tunneling.T1113 · Screen CaptureBurrowShell included screenshot-capture capabilities.T1140 · Deobfuscate/Decode Files or InformationThe loader decrypted the custom x64 shellcode implant BurrowShell.T1204.002 · Malicious FileThe infection chains used victim-facing PDF and macro-enabled Excel files to initiate execution.T1566.001 · Spearphishing AttachmentSpear-phishing emails delivered PDF lures and macro-enabled Excel documents.T1566.002 · Spearphishing LinkURLs in PDF decoys led victims to ClickOnce application manifests.T1573.001 · Symmetric CryptographyBurrowShell used RC4 encryption with a 32-character key for payload protection.T1574.002 · DLL Side-LoadingThe malicious mscorsvc.dll loader was launched through DLL side-loading alongside NGenTask.exe.
Threat Actors
Fishing ElephantThe article identifies Fishing Elephant as another name under which the SloppyLemming threat activity cluster is tracked.Outrider TigerThe article identifies Outrider Tiger as another name under which the SloppyLemming threat activity cluster is tracked.SloppyLemmingArctic Wolf attributes the January 2025–January 2026 campaign targeting government and critical infrastructure in Pakistan and Bangladesh to SloppyLemming.
Malware
Ares RATPrior campaigns mounted by the hacking crew have leveraged malware families like Ares RAT and WarHawk, which are often attributed to SideCopy and SideWinder, respectively.BurrowShelland critical infrastructure in Pakistan and Bangladesh that used two attack chains to deploy BurrowShell and a Rust-based keylogger.NekroWire RATlanguages and borrowed adversary simulation frameworks such as Cobalt Strike, Havoc, and the custom NekroWire RAT,” the cybersecurity company said in a report shared with The Hacker News.WarHawkPrior campaigns mounted by the hacking crew have leveraged malware families like Ares RAT and WarHawk, which are often attributed to SideCopy and SideWinder, respectively.
Vendors
CloudflareThe actor abused over 112 Cloudflare Workers domains and reused Havoc C2, DLL side-loading, and typo-squatted government-themed infrastructure consistent with prior campaigns.MicrosoftThe PDF decoys contain URLs designed to lead victims to ClickOnce application manifests, which then deploy a legitimate Microsoft .NET runtime executable (“NGenTask.exe”) and a malicious loader (“mscorsvc.dll”).
Products
Cloudflare WorkersThe actor abused over 112 Cloudflare Workers domains and reused Havoc C2, DLL side-loading, and typo-squatted government-themed infrastructure consistent with prior campaigns.ExcelThe intrusions relied on spear-phishing with PDF and macro-enabled Excel lures, ClickOnce and DLL side-loading to run NGenTask.exe/mscorsvc.dll and disguise C2 traffic as Windows Update.Microsoft .NETThe PDF decoys contain URLs designed to lead victims to ClickOnce application manifests, which then deploy a legitimate Microsoft .NET runtime executable (“NGenTask.exe”) and a malicious loader (“mscorsvc.dll”).Windows UpdateThe intrusions relied on spear-phishing with PDF and macro-enabled Excel lures, ClickOnce and DLL side-loading to run NGenTask.exe/mscorsvc.dll and disguise C2 traffic as Windows Update.
Tools
Cobalt Strikeactor using only traditional compiled languages and borrowed adversary simulation frameworks such as Cobalt Strike, Havoc, and the custom NekroWire RAT,” the cybersecurity company said in a report shared with TheHavocThe actor abused over 112 Cloudflare Workers domains and reused Havoc C2, DLL side-loading, and typo-squatted government-themed infrastructure consistent with prior campaigns.
Countries
Bangladeshcampaign (Jan 2025–Jan 2026) against government and critical infrastructure in Pakistan and Bangladesh that used two attack chains to deploy BurrowShell and a Rust-based keylogger.Pakistana year-long SloppyLemming campaign (Jan 2025–Jan 2026) against government and critical infrastructure in Pakistan and Bangladesh that used two attack chains to deploy BurrowShell and a Rust-based keylogger.
Industries
Defense“In particular, the targeting of Pakistani nuclear regulatory bodies, defense logistics organizations, and telecommunications infrastructure – alongside Bangladeshi energy utilities and financial institutions – alignsEnergySloppyLemming targeted government, energy, telecommunications, and financial entities in Pakistan and Bangladesh between Jan 2025 and Jan 2026.GovernmentArctic Wolf attributes a year-long SloppyLemming campaign (Jan 2025–Jan 2026) against government and critical infrastructure in Pakistan and Bangladesh that used two attack chains to deploy BurrowShell and a Rust-basednuclear“In particular, the targeting of Pakistani nuclear regulatory bodies, defense logistics organizations, and telecommunications infrastructure – alongside Bangladeshi energy utilities and financial institutions – alignsTelecommunicationsSloppyLemming targeted government, energy, telecommunications, and financial entities in Pakistan and Bangladesh between Jan 2025 and Jan 2026.