
UNC6426 Used nx npm Supply-Chain Compromise to Gain AWS Admin Access in 72 Hours
Summary
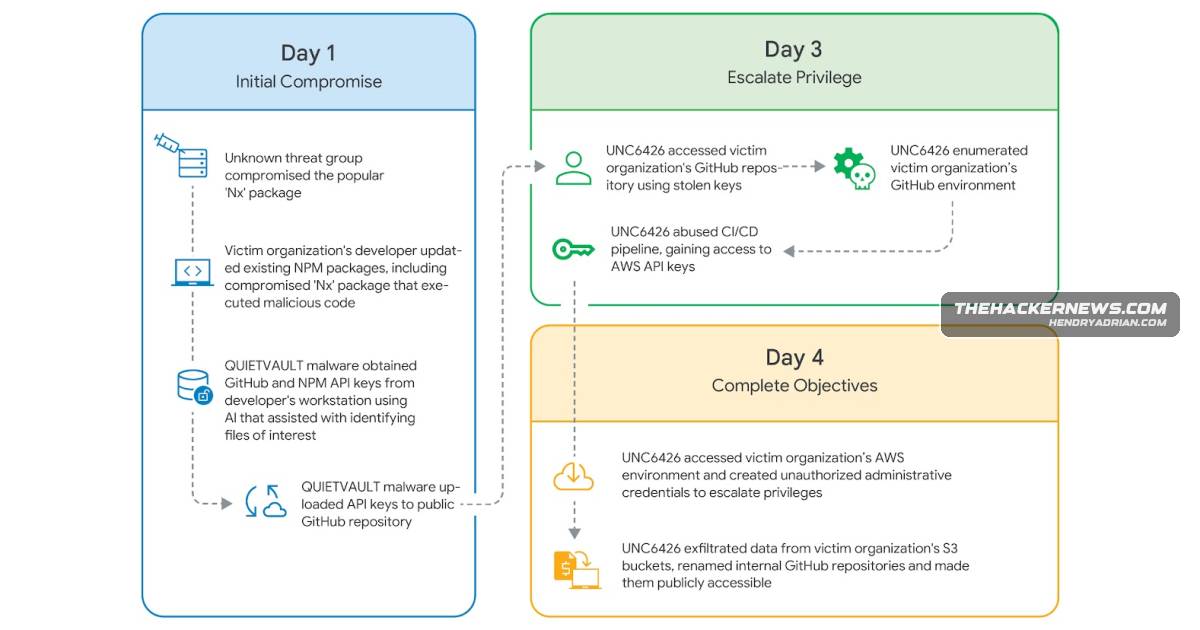
Google reported that UNC6426 used credentials stolen through the nx npm compromise to gain AWS administrator access within 72 hours, exfiltrate S3 data, destroy production resources, and expose internal GitHub repositories.
Key points
- The article attributes the incident details to Google, which said UNC6426 used credentials stolen after the nx npm supply-chain compromise in August 2025.
- A trojanized package’s postinstall script launched QUIETVAULT, which searched for environment variables and tokens using an LLM tool and uploaded data to a public GitHub repository.
- UNC6426 reportedly used stolen GitHub personal access tokens and the Nord Stream tool to obtain a GitHub service account’s credentials.
- The actor abused GitHub-to-AWS OIDC trust and an overly permissive role to deploy a CloudFormation stack that created an AWS Administrator role.
- With administrator access, the actor reportedly accessed S3 objects, terminated production EC2 and RDS instances, decrypted application keys, and made internal GitHub repositories public.
- Suggested defenses include disabling or sandboxing postinstall scripts, applying least privilege to CI/CD and OIDC roles, limiting PAT scope and lifetime, and monitoring unusual IAM activity.
Article Details
- Victim Organization
- Not disclosed
- Incident Type
- Supply-chain compromise followed by credential theft, unauthorized AWS access, S3 data exfiltration, and destructive cloud activity.
- Data Types Exposed
- Environment variables
- System information
- GitHub Personal Access Tokens and other credentials
- S3 files
- Application keys
- Internal GitHub repositories
- Affected Records
- Not disclosed
- Affected Data Size
- Not disclosed
- Operational Impact
- Production EC2 and RDS instances were terminated, application keys were decrypted, and the victim’s internal GitHub repositories were renamed and made public.
- Ransom Or Extortion
- None reported
- Claim Status
- confirmed
MITRE ATT&CK
T1078 · Valid AccountsUNC6426 reportedly used stolen GitHub Personal Access Tokens and a compromised GitHub service account to access the victim’s environment.T1098.003 · Additional Cloud RolesUNC6426 reportedly created an AWS IAM role with AdministratorAccess after abusing the GitHub-to-AWS OIDC trust.T1195.002 · Compromise Software Supply ChainTrojanized nx npm packages were distributed after attackers exploited a pull_request_target workflow in a Pwn Request supply-chain attack.T1485 · Data DestructionThe report describes destructive activity in production cloud environments, including terminating production EC2 and RDS instances.T1530 · Data from Cloud StorageThe threat actor reportedly enumerated and accessed objects in the victim’s S3 buckets.
Threat Actors
Malware
Vendors
Amazon Web ServicesThey weaponized a postinstall script that deployed the QUIETVAULT credential stealer, abused GitHub-to-AWS OIDC trust to create an Administrator role via CloudFormation, exfiltrated S3 data, and destroyed productionGitHubThey weaponized a postinstall script that deployed the QUIETVAULT credential stealer, abused GitHub-to-AWS OIDC trust to create an Administrator role via CloudFormation, exfiltrated S3 data, and destroyed productionnpmA threat actor known as UNC6426 used credentials stolen via an August 2025 supply-chain compromise of the nx npm package to fully breach a victim’s cloud environment within 72 hours.
Products
AWSThey weaponized a postinstall script that deployed the QUIETVAULT credential stealer, abused GitHub-to-AWS OIDC trust to create an Administrator role via CloudFormation, exfiltrated S3 data, and destroyed productionEC2The actor exfiltrated S3 data, terminated EC2 and RDS instances, decrypted application keys, and made internal GitHub repos public; mitigations include disabling postinstall scripts, enforcing least privilege,GitHubThey weaponized a postinstall script that deployed the QUIETVAULT credential stealer, abused GitHub-to-AWS OIDC trust to create an Administrator role via CloudFormation, exfiltrated S3 data, and destroyed productionNxA threat actor known as UNC6426 used credentials stolen via an August 2025 supply-chain compromise of the nx npm package to fully breach a victim’s cloud environment within 72 hours.Nx ConsoleGoogle said an employee at the victim organization ran a code editor application that used the Nx Console plugin, triggering an update in the process and resulting in the execution of QUIETVAULT.RDSThe actor exfiltrated S3 data, terminated EC2 and RDS instances, decrypted application keys, and made internal GitHub repos public; mitigations include disabling postinstall scripts, enforcing least privilege,S3stealer, abused GitHub-to-AWS OIDC trust to create an Administrator role via CloudFormation, exfiltrated S3 data, and destroyed production resources.