Report: Revolut Hackers Used Infostealer-Stolen Government Credentials in Social-Engineering Scheme
Summary
Duel alleges hackers used compromised Italian government email accounts to send fraudulent information requests to Revolut over five months. Hudson Rock found about 300 compromised logins for the government domain and says existing infostealer logs may have supplied the
Key points
- Duel says the hackers accessed Italian government email accounts using infostealer credentials, then added a recovery address, monitored inboxes and concealed their messages.
- The alleged attackers targeted Revolut Bank UAB with fraudulent requests made to appear to come from the Italian government.
- The article says Revolut reportedly complied with requests over a five-month period, including providing guidance after the attacker sent an incorrect document.
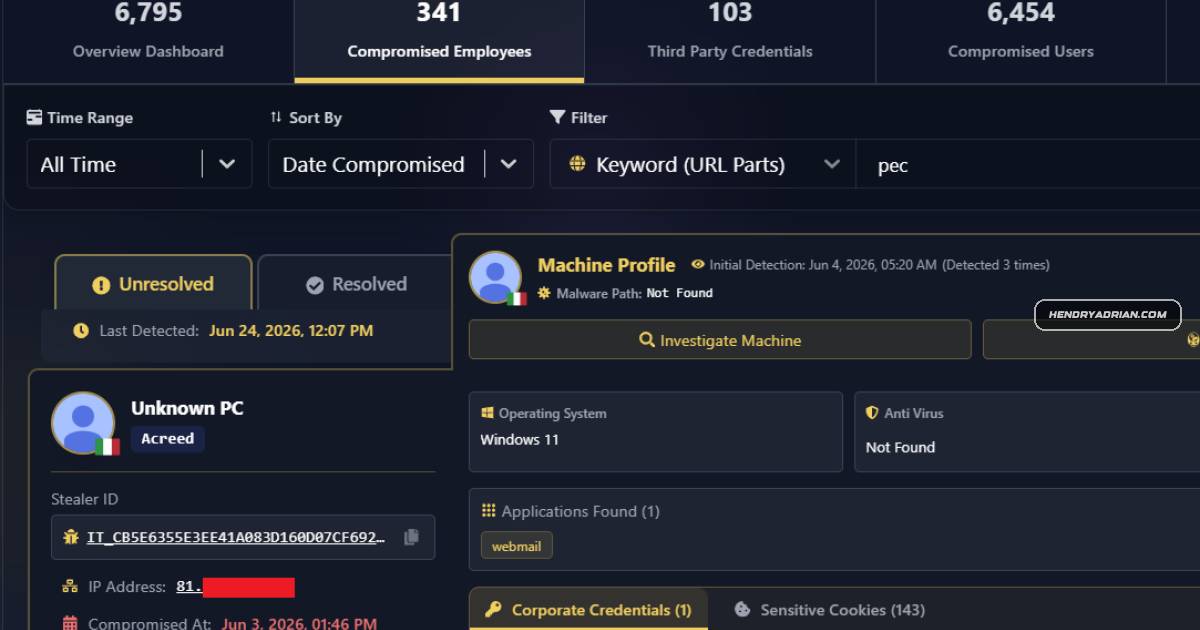
- Hudson Rock identified about 300 compromised webmail logins for the Italian Ministry of the Interior’s pec.interno.it domain.
- Hudson Rock assesses that the hackers likely used existing infostealer logs rather than infecting the specific government employees themselves.
- The article reports credible kidnapping threats against victims, but the incident details are presented as claims from Duel and the hacker.
Article Details
- Victim Organization
- Revolut, including Revolut Bank UAB
- Incident Type
- Alleged unauthorized disclosure of customer information in response to fraudulent government requests sent from compromised Italian government email accounts
- Data Types Exposed
- Customer information; specific data types were not disclosed
- Operational Impact
- According to the Duel Investigations Team, Revolut provided information in response to repeated fraudulent requests over approximately five months. The article does not independently confirm the extent of the disclosure.
- Claim Status
- alleged
MITRE ATT&CK
T1070.008 · Clear Mailbox DataThe attacker reportedly deleted sent messages and incoming replies from compromised mailboxes to conceal the correspondence.T1078 · Valid AccountsThe attacker reportedly used credentials for compromised Italian government employee email accounts to send requests.T1114.002 · Remote Email CollectionThe attacker reportedly monitored compromised inboxes and downloaded replies as .eml files.