
ReliaQuest Details LeakNet’s ClickFix Lures and Deno-Based In-Memory Loader
Summary
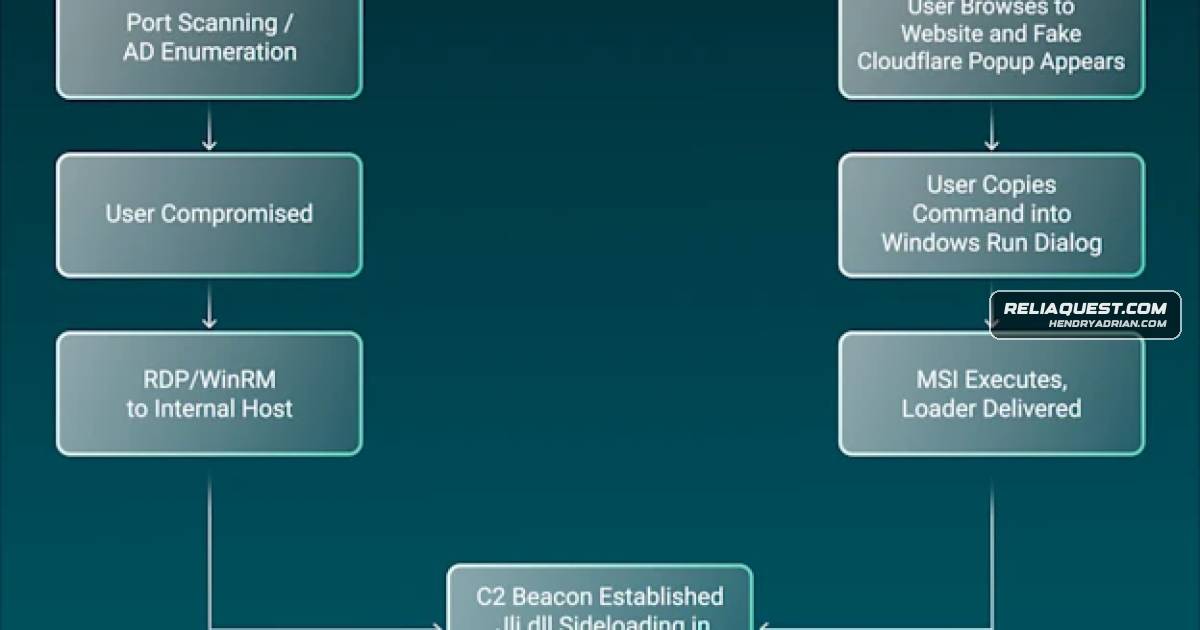
ReliaQuest reports that LeakNet is using ClickFix lures and a Deno-based in-memory loader, followed by recurring jli.dll sideloading, PsExec lateral movement, and S3 staging. A similar Deno-loader incident had inconclusive attribution.
Key points
- ReliaQuest attributes ClickFix activity on compromised legitimate websites to LeakNet with high confidence, based on infrastructure and TTP overlap with previously confirmed activity.
- The lures prompt users to run an msiexec command that downloads and executes the group’s loader.
- The Deno loader runs base64-encoded JavaScript in memory, fingerprints hosts, selects a C2 endpoint, and repeatedly retrieves and executes additional code.
- Across confirmed LeakNet incidents, ReliaQuest observed jli.dll sideloading from C:\ProgramData\USOShared, PsExec lateral movement, and S3 buckets used for payload staging.
- ReliaQuest recommends behavioral detections for unusual msiexec activity, Deno outside development environments, DLL sideloading, anomalous PsExec use, and unexpected outbound S3 traffic.
- A separate incident involving Microsoft Teams phishing and a similar Deno loader was remediated quickly; attribution remained inconclusive.
Article Details
- Attack Vectors
- ClickFix lures on compromised legitimate websites prompt users to run malicious msiexec commands that download and execute a loader.
- A Deno-based loader runs base64-encoded JavaScript in memory, fingerprints the host, and establishes staged C2.
- In a separate incident with inconclusive attribution, Microsoft Teams phishing led a user to run an MSI and VBS file that launched a similar Deno loader.
- Post-compromise activity includes jli.dll DLL sideloading, PsExec-based lateral movement, and S3 bucket payload staging.
- Defensive Notes
- Detect suspicious msiexec commands spawned by browsers and unusual command-line or network activity from Deno, especially outside development environments.
- Monitor for jli.dll sideloading from C:\ProgramData\USOShared and anomalous PsExec usage.
- Monitor unexpected outbound connections and repeated beaconing to external infrastructure, including S3 buckets.
- Block newly registered domains, restrict Win-R and PsExec to authorized administrators, and ban known malicious file hashes.
- Isolate affected hosts when post-exploitation activity is confirmed.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | apiclofront[.]com | Identified as a ClickFix domain. |
| DOMAIN | binclloudapp[.]com | Listed in the article's LeakNet campaign IOC table; its specific role is not individually stated. |
| DOMAIN | cnoocim[.]com | Listed in the article's LeakNet campaign IOC table; its specific role is not individually stated. |
| DOMAIN | crahdhduf[.]com | Listed in the article's LeakNet campaign IOC table; its specific role is not individually stated. |
| DOMAIN | delhedghogeggs[.]com | Listed in the article's LeakNet campaign IOC table; its specific role is not individually stated. |
| DOMAIN | mshealthmetrics[.]com | Listed in the article's LeakNet campaign IOC table; its specific role is not individually stated. |
| DOMAIN | ndibstersoft[.]com | Listed in the article's LeakNet campaign IOC table; its specific role is not individually stated. |
| DOMAIN | neremedysoft[.]com | Identified as a C2 domain associated with jli.dll sideloading. |
| DOMAIN | okobojirent[.]com | Identified as a Deno C2 domain. |
| DOMAIN | sendtokenscf[.]com | Listed as campaign infrastructure in the article's IOC section, which identifies it among ClickFix and Deno C2 domains. |
| DOMAIN | serialmenot[.]com | Listed in the article's LeakNet campaign IOC table; its specific role is not individually stated. |
| DOMAIN | tools[.]usersway[.]net | Listed as a ClickFix domain on compromised websites used in the LeakNet campaign. |
| DOMAIN | verify-safeguard[.]top | Listed in the article's LeakNet campaign IOC table; its specific role is not individually stated. |
| DOMAIN | weaplink[.]com | Listed in the article's LeakNet campaign IOC table; its specific role is not individually stated. |
| DOMAIN | windowallclean[.]com | Listed in the article's LeakNet campaign IOC table; its specific role is not individually stated. |
| HOSTNAME | backupdailyawss[.]s3[.]us-east-1[.]amazonaws[.]com | Identified as a malicious S3 bucket used for payload staging. |
| HOSTNAME | fastdlvrss[.]s3[.]us-east-1[.]amazonaws[.]com | Identified as a malicious S3 bucket used for payload staging. |
| IPV4 | 144[.]31[.]2[.]161 | Listed as attacker infrastructure in the article's LeakNet IOC section. |
| IPV4 | 144[.]31[.]224[.]98 | Listed as attacker infrastructure in the article's LeakNet IOC section. |
| IPV4 | 144[.]31[.]54[.]243 | Listed as attacker infrastructure in the article's LeakNet IOC section. |
| IPV4 | 194[.]31[.]223[.]42 | Identified as a Deno C2 IP address. |
| IPV4 | 87[.]121[.]79[.]25 | Listed as attacker infrastructure in the article's LeakNet IOC section. |
| IPV4 | 87[.]121[.]79[.]6 | Listed as attacker infrastructure in the article's LeakNet IOC section. |
MITRE ATT&CK
T1021.002 · SMB/Windows Admin SharesLeakNet used PsExec for lateral movement after checking available credentials with klist.T1059.007 · JavaScriptThe Deno runtime executed base64-encoded JavaScript passed in a data URL.T1071.001 · Web ProtocolsThe Deno loader and post-exploitation activity used HTTP(S) beaconing to attacker-controlled C2 infrastructure.T1102.002 · Bidirectional CommunicationLeakNet used S3 buckets and web services for payload staging and reported exfiltration activity.T1189 · Drive-by CompromiseLeakNet delivered ClickFix lures through compromised legitimate websites.T1204.004 · Malicious Copy and PasteThe lure socially engineered users into manually running an msiexec command.T1218.007 · MsiexecClickFix lures prompted users to run msiexec to download and execute the loader.T1574.001 · DLLLeakNet placed a malicious jli.dll beside a legitimate Java process in C:\ProgramData\USOShared for DLL sideloading.T1620 · Reflective Code LoadingDeno decoded and executed the loader's base64-encoded JavaScript directly in memory.
Threat Actors
Products
Denoshifted from buying access to running ClickFix lures on compromised legitimate websites and introduced a Deno-based, in-memory loader that executes base64-encoded payloads, fingerprints hosts, and establishes C2 withMicrosoft TeamsReliaQuest also observed a separate intrusion attempt in which threat actors used Microsoft Teams phishing to socially engineer a user into launching a payload chain that ended in a similar Deno-based loader.