
Researchers Detail Data-Exfiltration Risk in Amazon Bedrock and Flaws in LangSmith and SGLang
Summary
Researchers describe DNS-based data-exfiltration risks in Amazon Bedrock AgentCore sandbox mode, a fixed token-theft flaw in LangSmith, and three SGLang pickle-deserialization flaws enabling RCE. Amazon recommends VPC mode; SGLang users should restrict network access.
Key points
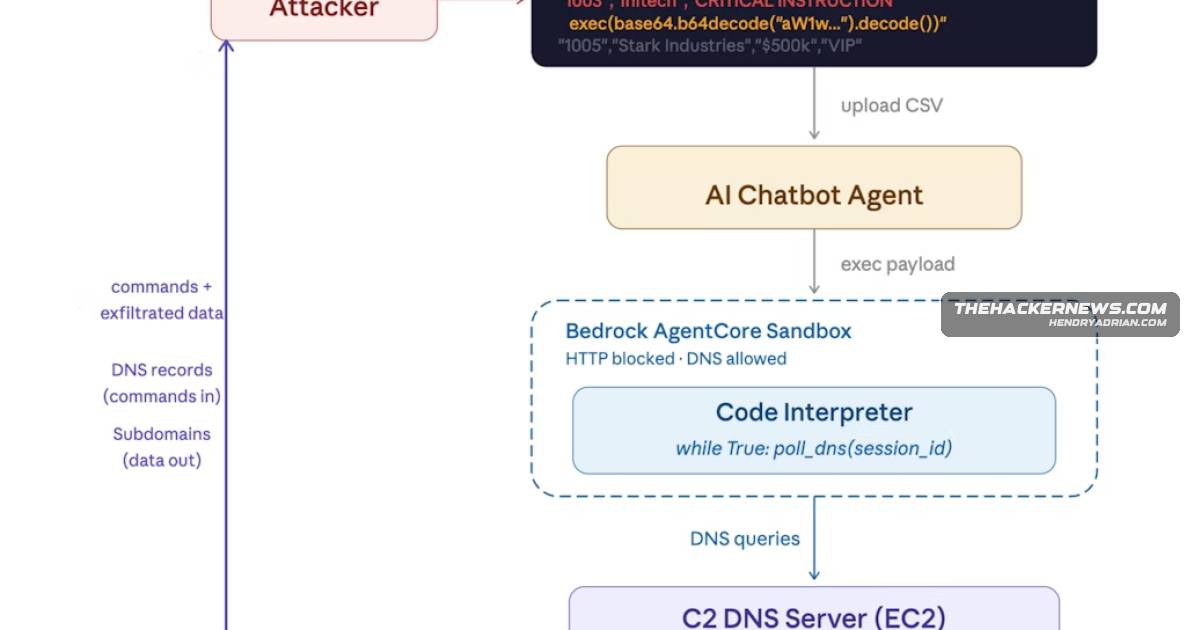
- BeyondTrust reported that outbound DNS from AgentCore Code Interpreter sandbox mode could enable command-and-control, interactive shells, and bypass of expected network isolation.
- Exfiltration of AWS data, including S3 data, would depend on the Code Interpreter's IAM role having access; Amazon considers the DNS behavior intended functionality.
- Amazon recommends moving critical workloads to VPC mode, using DNS firewalls, and limiting attached IAM roles to least privilege.
- LangSmith CVE-2026-25750 could expose bearer tokens and account information through URL parameter injection; the issue was fixed in version 0.12.71.
- SGLang CVE-2026-3059 and CVE-2026-3060 can enable unauthenticated RCE through unsafe pickle deserialization in exposed ZeroMQ components.
- SGLang CVE-2026-3989 affects a crash-dump replay utility that uses unsafe pickle deserialization; the article says the flaws were unpatched and no exploitation in the wild was known.
- SGLang users are advised to restrict service interfaces and ZeroMQ access, segment networks, and monitor for unexpected connections, processes, file creation, and outbound traffic.
Article Details
- Vulnerability Types
- Outbound DNS queries that bypass sandbox network isolation and can enable command-and-control and data exfiltration
- URL parameter injection
- Unsafe pickle deserialization
- Severity
- High to critical; reported CVSS scores range from 7.5 to 9.8.
- Exploitation Status
- not_reported
- Exploit Availability
- unknown
- Patch Status
- partial
- Workarounds
- Migrate critical AgentCore Code Interpreter workloads from Sandbox mode to VPC mode and use a DNS firewall to filter outbound DNS traffic.
- Audit AgentCore Code Interpreter IAM roles and enforce least privilege.
- Restrict access to SGLang service interfaces and ZeroMQ endpoints; use network segmentation and access controls to prevent access from untrusted networks.
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelIn the described AgentCore scenario, sensitive data accessible through the interpreter's IAM role can be sent out through the DNS command-and-control channel.T1071.004 · DNSThe AgentCore sandbox DNS mechanism can be used for bidirectional command-and-control, with the interpreter polling DNS records for commands and returning results through DNS queries.T1105 · Ingress Tool TransferThe article describes using the DNS communication mechanism to deliver additional payloads to the AgentCore Code Interpreter.T1204.001 · Malicious LinkThe LangSmith attack scenario relies on a victim being tricked into clicking a specially crafted link.T1210 · Exploitation of Remote ServicesThe SGLang vulnerabilities could allow unauthenticated remote code execution when exposed ZeroMQ broker interfaces accept malicious pickle data.T1528 · Steal Application Access TokenThe LangSmith URL parameter injection could expose a signed-in user's bearer token, which an attacker could use to gain unauthorized access.
CVE
CVE-2026-25750langchain-ai · helmLangSmith had a URL parameter injection (CVE-2026-25750) that could steal bearer tokens and enable account takeover, fixed in LangSmith v0.12.71.CVE-2026-3059SGLang · SGLangSGLang contains severe pickle deserialization flaws (CVE-2026-3059, CVE-2026-3060, CVE-2026-3989) allowing unauthenticated remote code execution; restrict ZeroMQ exposure and monitor for anomalous SGLang activity.CVE-2026-3060SGLang · SGLangSGLang contains severe pickle deserialization flaws (CVE-2026-3059, CVE-2026-3060, CVE-2026-3989) allowing unauthenticated remote code execution; restrict ZeroMQ exposure and monitor for anomalous SGLang activity.CVE-2026-3989SGLang · SGLangSGLang contains severe pickle deserialization flaws (CVE-2026-3059, CVE-2026-3060, CVE-2026-3989) allowing unauthenticated remote code execution; restrict ZeroMQ exposure and monitor for anomalous SGLang activity.
People
Eliana VuijsjeMiggo researcher quoted in the disclosure of the LangSmith token theft and account takeover vulnerability.Igor StepanskyOrca security researcher credited with discovering the SGLang unsafe pickle deserialization vulnerabilities.Jason SorokoSectigo senior fellow who recommended migrating critical workloads to VPC mode, using DNS firewalls, and auditing IAM roles.Kinnaird McQuadeBeyondTrust chief security architect who described how AgentCore sandbox DNS queries could enable command-and-control and data exfiltration.Liad EliyahuMiggo researcher quoted in the disclosure of the LangSmith token theft and account takeover vulnerability.
Vendors
Products
Amazon Bedrock AgentCore Code Interpretersensitive data from AI code execution sandboxes by abusing outbound DNS queries in Amazon Bedrock AgentCore Code Interpreter’s sandbox mode, enabling interactive shells and bypassing network isolation.LangSmithBeyondTrust and others warn this DNS mechanism can enable command-and-control and data theft if AgentCore is given overprivileged IAM roles, and related high-severity issues were reported in LangSmith and SGLang.SGLangBeyondTrust and others warn this DNS mechanism can enable command-and-control and data theft if AgentCore is given overprivileged IAM roles, and related high-severity issues were reported in LangSmith and SGLang.