
NetExec Tutorial Shows Remote Command Execution Across Six Protocols
Summary
A hands-on NetExec tutorial demonstrates remote command execution over SMB, WinRM, WMI, MSSQL, RDP and SSH, including password, hash, Kerberos-ticket and certificate authentication; it notes MSSQL xp_cmdshell can run commands as the SQL Server service account.
Key points
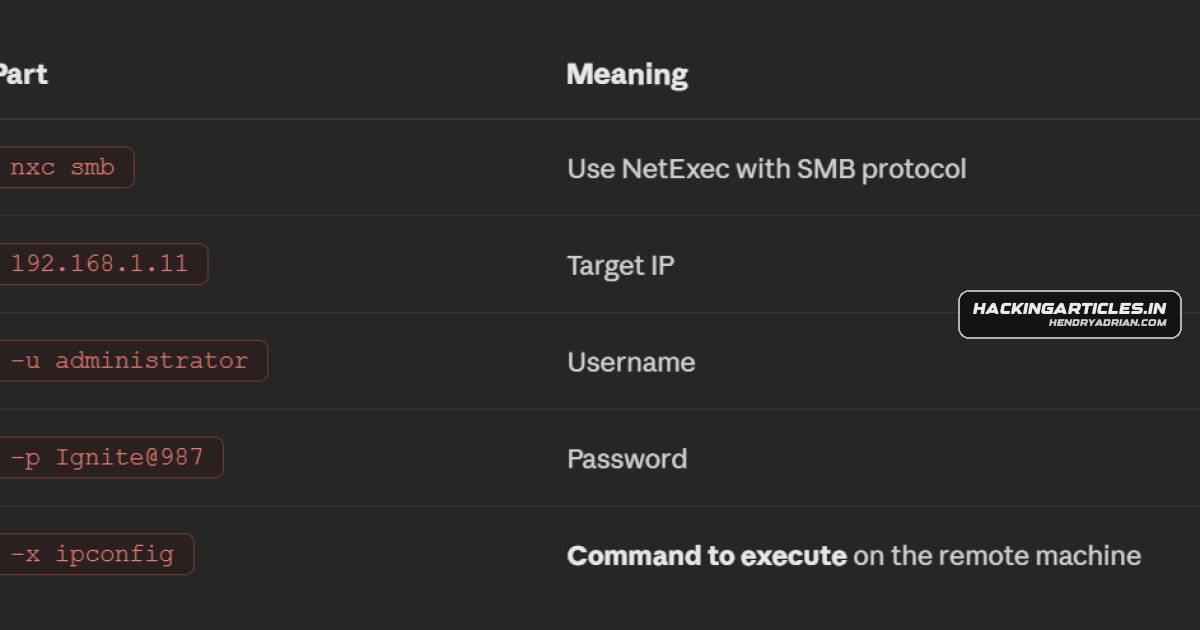
- The tutorial demonstrates NetExec command execution over SMB, WinRM, WMI, MSSQL, RDP and SSH.
- Examples cover authentication with passwords, NTLM hashes, Kerberos tickets and certificates.
- It explains that certificate authentication can use AD CS certificates with Kerberos PKINIT.
- The MSSQL examples use xp_cmdshell, which the article says can run commands in the SQL Server service account's context when enabled with SA privileges.
- The RDP example uses clipboard injection and timing delays to enter and execute commands.
Article Details
- Topic
- NetExec command execution and authentication techniques for penetration testing across remote protocols
MITRE ATT&CK
T1021.001 · Remote Desktop ProtocolThe article describes command execution through an RDP session.T1021.002 · SMB/Windows Admin SharesThe article describes executing commands remotely over SMB.T1021.004 · SSHThe article describes authenticated remote command-line access over SSH.T1021.006 · Windows Remote ManagementThe article describes executing commands remotely over WinRM.T1047 · Windows Management InstrumentationThe article describes executing commands through WMI.T1078 · Valid AccountsThe article describes authenticating to remote systems with valid credentials.T1550.002 · Pass the HashThe article describes Pass-the-Hash authentication using NTLM hashes to access remote services.T1550.003 · Pass the TicketThe article describes using Kerberos tickets for Pass-the-Ticket authentication.T1649 · Steal or Forge Authentication CertificatesThe article describes using stolen or forged Active Directory certificates for authentication through PKINIT.
Products
Microsoft Active Directorylike Pass-the-Hash, Pass-the-Ticket, and Pass-the-Certificate (PKINIT) for moving laterally in Active Directory environments and can leverage services like xp_cmdshell for SYSTEM-level escalation.Microsoft WindowsSMB (Server Message Block) is the most commonly targeted protocol for lateral movement in Windows Active Directory environments.SQL ServerNetExec can leverage SQL Server’s built-in xp_cmdshell stored procedure to run OS commands.
Tools
CrackMapExecIt is the modern successor to CrackMapExec and is widely used in Active Directory environments.NetExecNetExec (nxc) is a modern post-exploitation and lateral movement tool that enables penetration testers to execute commands across SMB, WinRM, WMI, MSSQL, RDP, and SSH using credentials, hashes, tickets, or certificates.