
FBI, CISA Urge Intune Hardening After Stryker Device-Wiping Attack
Summary
After more than 200,000 Stryker devices were reportedly wiped, CISA and the FBI urged Microsoft Intune users to adopt stronger access controls and dual-admin approval. Federal authorities also seized a website linked to Handala.
Key points
- CISA and the FBI said they are coordinating on the response to the Stryker attack, in which more than 200,000 company devices were reportedly wiped.
- The article says attackers used legitimate access to Microsoft Intune rather than malware; the attack is linked to the Handala group.
- CISA advised Intune users to apply role-based access controls and require multi-factor authentication for accounts.
- The agencies recommended Microsoft Entra ID and requiring a second administrator’s approval for sensitive actions such as device wipes.
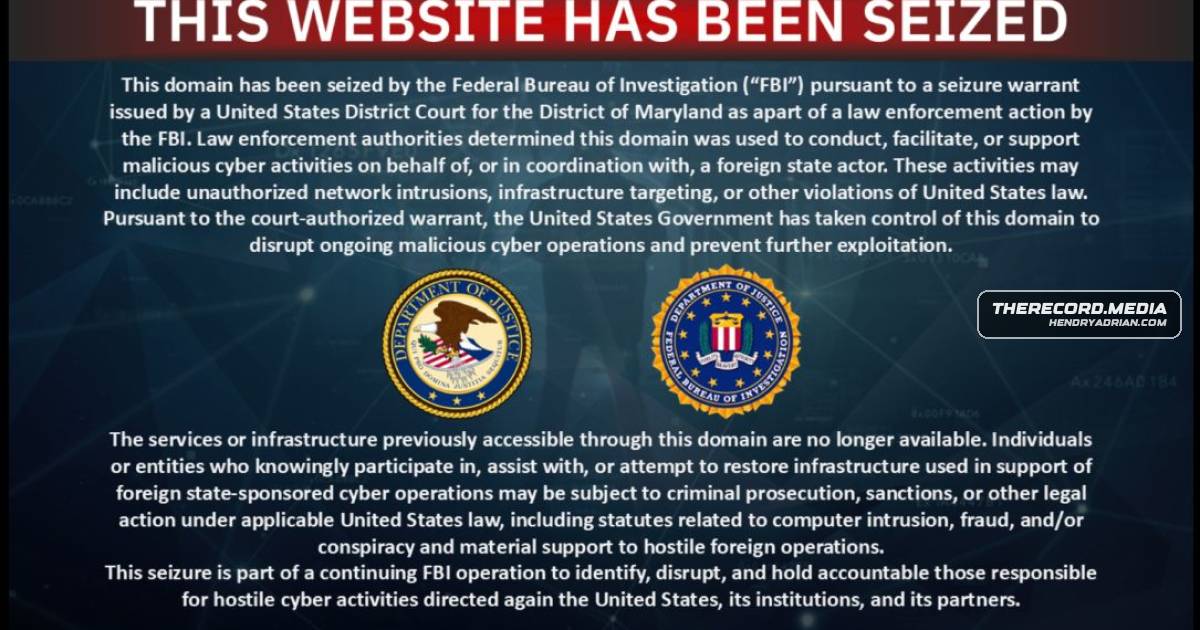
- Federal authorities seized a website linked to Handala, saying it had supported malicious cyber activities.
Article Details
- Event Type
- Cyberattack on Stryker and federal cybersecurity advisory
- Impact
- More than 200,000 company devices were wiped, leaving employees locked out of critical systems and disrupting work at factories in the U.S., Ireland, India, and other countries. The attackers reportedly used legitimate Microsoft Intune access rather than malware; some employees said personal devices and non-company data were also wiped.
Threat Actors
Vendors
Products
IntuneFederal cybersecurity agencies urged organizations to harden Microsoft Intune deployments after an alleged Iran-linked cyberattack wiped more than 200,000 devices at medical device firm Stryker.Microsoft Entra IDCISA and the FBI advised using role-based access, multi-factor authentication, Microsoft Entra ID, and dual-admin approval policies while federal authorities disrupted the Handala group’s infrastructure.
Countries
Indialocked out of critical systems and struggling to continue working at factories across the U.S., Ireland, India and other countries.IranFederal cybersecurity agencies urged organizations to harden Microsoft Intune deployments after an alleged Iran-linked cyberattack wiped more than 200,000 devices at medical device firm Stryker.Irelandlocked out of critical systems and struggling to continue working at factories across the U.S., Ireland, India and other countries.United Statesemployees locked out of critical systems and struggling to continue working at factories across the U.S., Ireland, India and other countries.