
Play Claims Ascent Asset Group Was Targeted in a Ransomware Incident
Summary
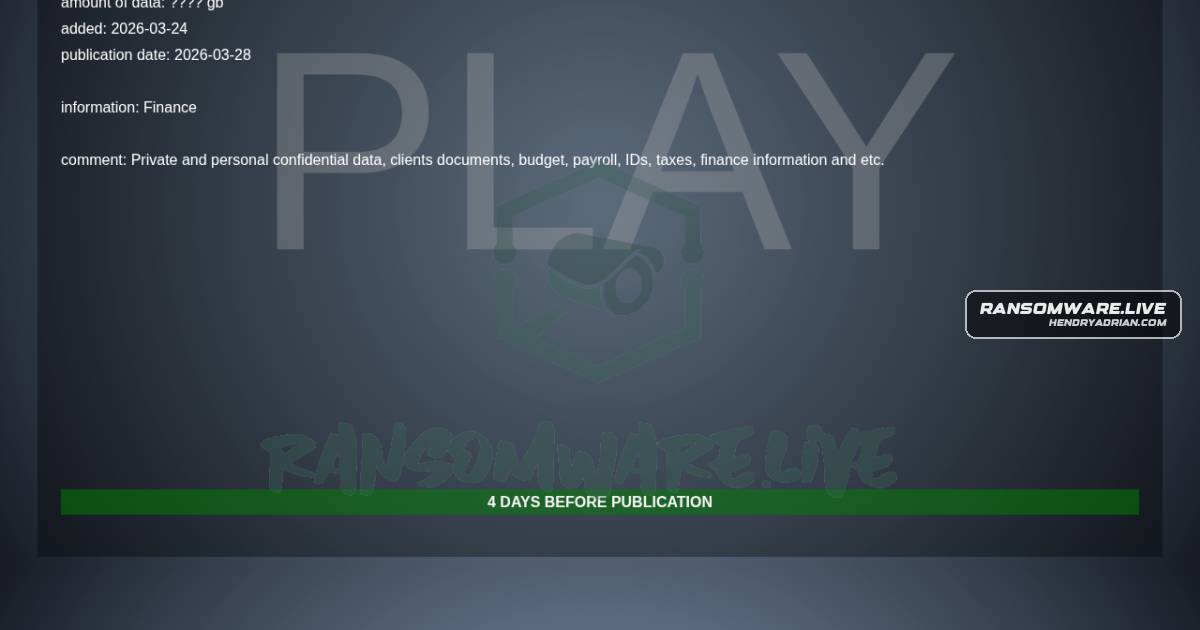
Play claims it targeted U.S. financial services firm Ascent Asset Group, encrypted files and demanded a ransom. The post says impact and possible data exfiltration are still being assessed; the claims are unconfirmed.
Key points
- The named victim is Ascent Asset Group, a financial services organization in the United States.
- The post attributes the claim to the Play threat actor and links to a leak-site listing.
- The claim alleges file encryption and a ransom demand.
- The post says impact and possible data exfiltration are still being assessed.
- The monitoring post says it cannot confirm the accuracy of the group's claims.
Article Details
- Victim
- Ascent Asset Group
- Claim Date
- 2026-03-24
- Encryption Status
- The ransomware claim says files were encrypted; this is not independently confirmed.
- Exfiltration Status
- Unknown; the claim says potential data exfiltration is still being assessed.
- Exfiltrated Data
- No specific data type is reported; potential exfiltration is under assessment.
- Ransom Demand
- The claim reports a ransom demand, but no amount is disclosed.
- Leak Status
- Unknown; no leak or publication status is reported.