
Play Claims Ransomware Attack on Capital Wholesale Drug
Summary
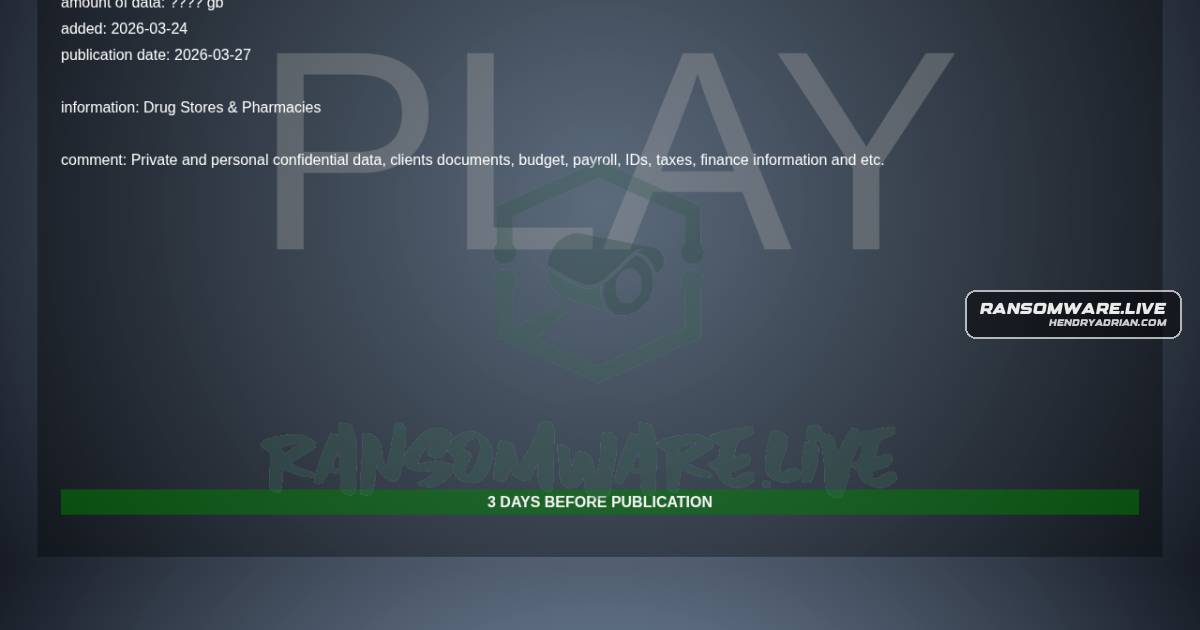
Ransomware[.]live lists Capital Wholesale Drug as a Play ransomware claim, alleging file encryption and possible data exfiltration. The post says the claim is unconfirmed.
Key points
- The monitoring record names Capital Wholesale Drug, a healthcare organization in the United States, as the alleged victim.
- The claim is attributed to the Play threat actor and alleges file encryption and possible data exfiltration.
- The record lists the claim as discovered and published on March 24, 2026.
- The post states that the information is based on public claims and has not been confirmed.
Article Details
- Victim
- Capital Wholesale Drug
- Victim Domain
- Unknown
- Claim Date
- 2026-03-24
- Encryption Status
- Alleged by Play; unconfirmed.
- Encrypted Size
- Not disclosed
- Exfiltration Status
- Potential exfiltration alleged; unconfirmed.
- Exfiltrated Data
- Specific data not disclosed.
- Exfiltrated Size
- Not disclosed
- Ransom Demand
- Not disclosed
- Leak Status
- Not disclosed