
Play Claims Ransomware Attack on TPIS Industrial Services
Summary
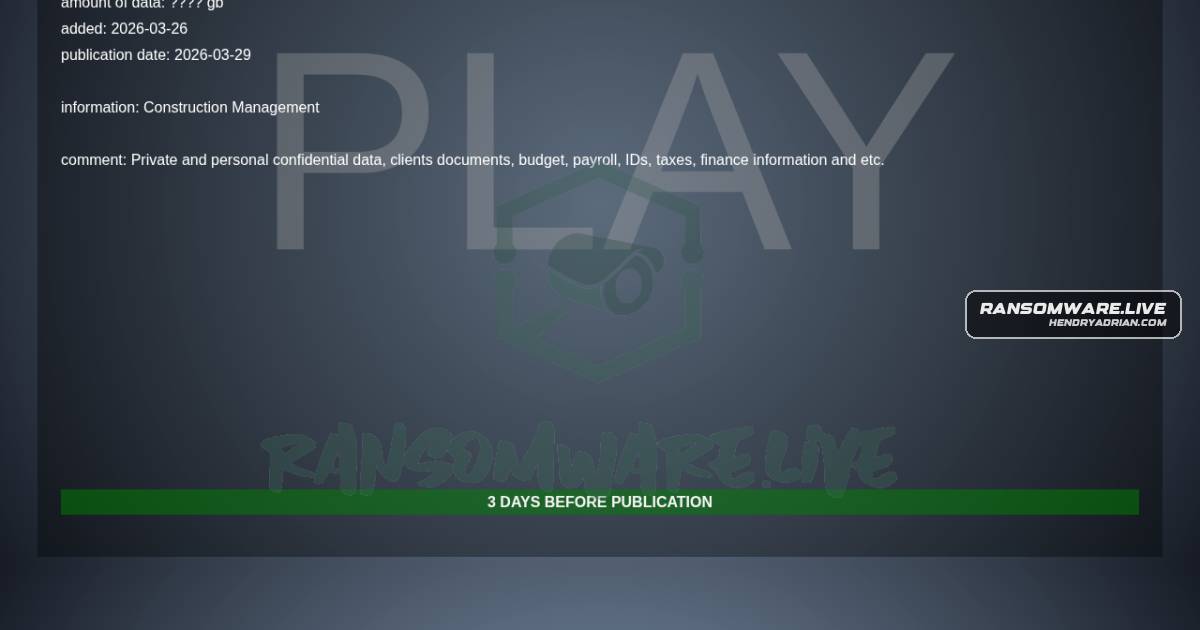
A ransomware monitoring post attributes to Play claims that TPIS Industrial Services’ systems were encrypted and data may have been exfiltrated. The post says the claims are unconfirmed.
Key points
- The monitoring record names TPIS Industrial Services in the United States as the claimed victim.
- The ransomware claim is attributed to the Play group and linked to its public post.
- The post claims systems were encrypted and data may have been exfiltrated; these claims are unconfirmed.
- The record lists the incident as discovered and published on March 26, 2026.
Article Details
- Victim
- TPIS Industrial Services
- Claim Date
- 2026-03-26
- Encryption Status
- The ransomware group claims systems were encrypted; this is unconfirmed by the victim.
- Exfiltration Status
- Potential data exfiltration was claimed; this is unconfirmed.
- Exfiltrated Data
- No specific data types were identified.
- Ransom Demand
- Not disclosed
- Leak Status
- The group published a claim; actual data publication and the authenticity of any data are not confirmed.