
Fake VS Code Security Alerts on GitHub Target Developers With Malware
Summary
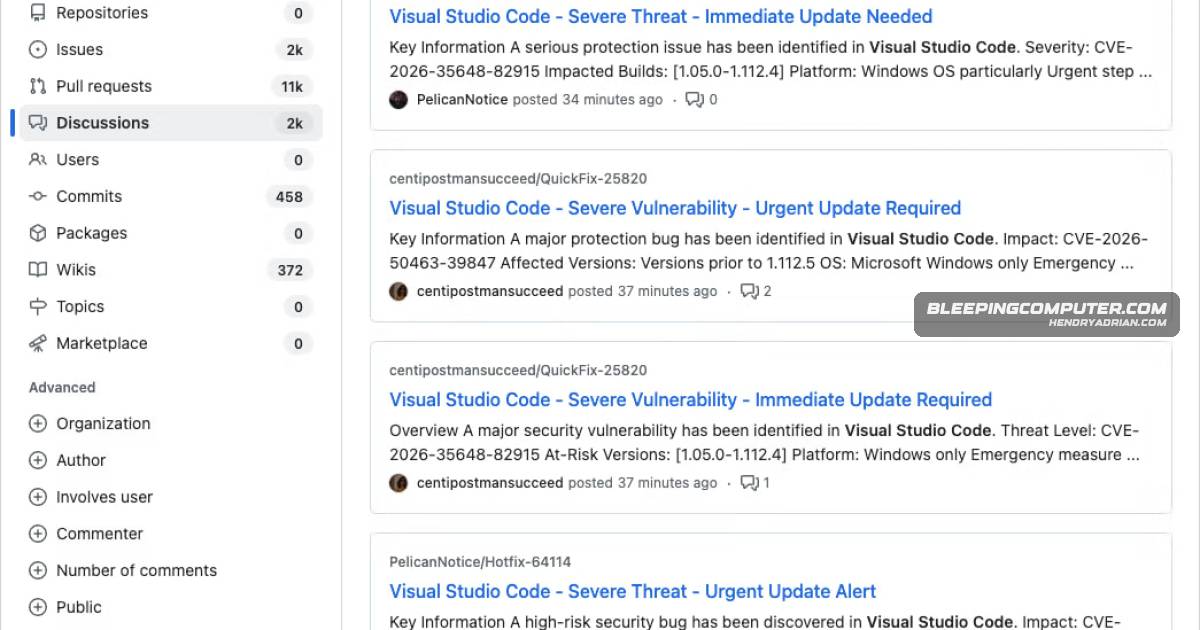
A campaign is flooding GitHub Discussions with fake VS Code security alerts that impersonate maintainers and link to downloads. A redirect leads to JavaScript that profiles visitors; Socket says it did not capture the second-stage payload.
Key points
- Socket says thousands of similar posts appeared across repositories, often within minutes, from newly created or low-activity accounts.
- The posts impersonate maintainers, use fake CVE IDs and mass-tag users to make fraudulent advisories appear urgent and legitimate.
- Links to supposed patched extensions can redirect users to drnatashachinn[.]com, where a JavaScript script profiles visitors.
- The script collects timezone, locale, user-agent, operating-system and automation-indicator data, then sends it to a command-and-control server.
- Socket describes the profiling as a filtering step before possible second-stage delivery; it did not capture that payload and says the script does not directly capture credentials.
- Users are advised to verify vulnerability IDs through authoritative sources and be wary of external download links and mass tagging.
Article Details
- Event Type
- A large-scale malware-distribution campaign using fake Visual Studio Code security alerts in GitHub Discussions.
- Impact
- The posts direct developers through external links to drnatashachinn[.]com, where a JavaScript script profiles visitors and sends collected data to command-and-control for victim filtering. Socket did not capture the second-stage payload and reported that the script does not attempt to capture credentials.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | drnatashachinn[.]com | Redirect destination that runs a JavaScript reconnaissance script to profile visitors and send collected data to command-and-control. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe collected profiling data is sent to command-and-control via a POST request.T1082 · System Information DiscoveryThe JavaScript reconnaissance script collects victims’ operating-system details.T1204.001 · Malicious LinkUsers who click the links in the fraudulent GitHub Discussions alerts are redirected toward the reconnaissance script.T1614.001 · System Language DiscoveryThe JavaScript reconnaissance script collects victims’ timezone information.
Products
GitHubA large-scale campaign is targeting developers on GitHub by posting fake Visual Studio Code security alerts in repository Discussions to trick users into downloading malware.VSCodeA large-scale campaign is targeting developers on GitHub by posting fake Visual Studio Code security alerts in repository Discussions to trick users into downloading malware.