China-Nexus UNC6508 Used INFINITERED to Target North American Medical and Research Organizations
Summary
Google says UNC6508 compromised North American research organizations through REDCap servers, using custom INFINITERED malware to steal credentials and maintain access before exfiltrating email through covert compliance rules.
Key points
- GTIG attributes the campaign to China-nexus threat actor UNC6508 with high confidence and says the earliest known compromise occurred in September 2023.
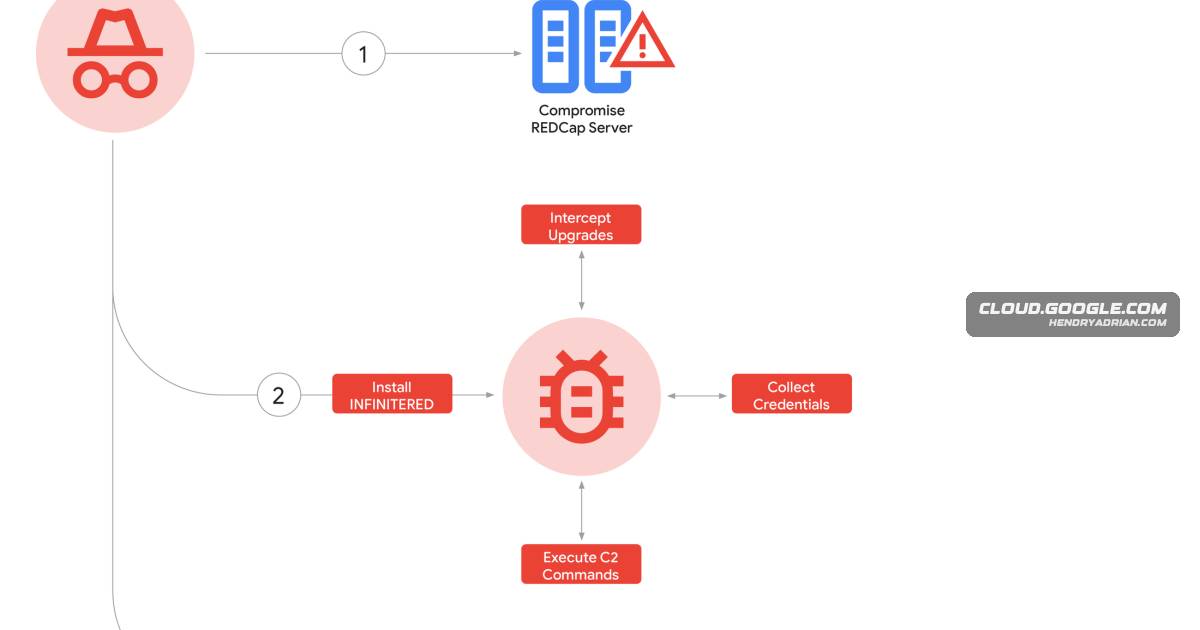
- The actor exploited externally facing REDCap systems, deployed a web shell, and later installed INFINITERED, which captured login credentials and persisted through software upgrades.
- INFINITERED’s backdoor could execute commands, run database queries, transfer files, and return system and database information.
- Using harvested credentials, UNC6508 accessed an administrator account and created a content compliance rule that silently forwarded matching email to an actor-controlled Gmail account.
- The targeted organizations included medical, academic, and military research entities; collection interests included defense, AI, cyber programs, and medical research.
- GTIG says it disrupted associated infrastructure, notified affected organizations, and disabled the Gmail account used for exfiltration.
- Recommended defenses include updating and removing legacy REDCap versions, scanning for INFINITERED, enabling phishing-resistant two-step verification, and auditing compliance rules and logs.
Article Details
- Attack Vectors
- UNC6508 exploited externally facing REDCap servers, including by probing for vulnerable legacy versions; GTIG could not confirm the initial access method.
- INFINITERED captured credentials submitted through REDCap login POST requests, then UNC6508 replayed harvested credentials to access internal networks and an administrator account.
- INFINITERED maintained persistence by modifying REDCap files and intercepting software upgrades; the actor also deployed the help.php web shell.
- UNC6508 used REDCap content compliance rules to silently BCC-forward selected email to an actor-controlled account for data exfiltration.
- INFINITERED accepted commands through the REDCAP-TOKEN HTTP cookie, including shell commands, SQL queries, and file transfers.
- Defensive Notes
- Patch REDCap to the latest version and remove older versions to reduce exposure to downgrade attacks.
- Scan REDCap servers for INFINITERED using the provided YARA rule and IOCs.
- Enforce phishing-resistant 2-Step Verification for enterprise administrators, including through third-party Identity Providers, and use unique credentials across security domains.
- Review administrator audit logs and content compliance rules for unauthorized changes; enable audit logging and monitor for changes to data.
- Use Data Loss Prevention rules to block or alert on external sharing of sensitive data.
- For highly sensitive accounts, consider Advanced Protection and enforce Device Bound Session Credentials with CAA on Windows devices.
- Include Workspace logs in SIEM coverage and use Chrome Enterprise Password Leak Detection to identify potentially compromised password use.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
bebitabarefoot774@gmail[.]com | Actor-controlled Gmail account used to receive silently forwarded email for data exfiltration. | |
| IPV4 | 23[.]169[.]65[.]49 | Source IP used to log in to the compromised administrator account; identified as a compromised ASUS router. |
| SHA256 | 4efbef69eb3b09bacff892d6a55778d07c418e7f15eba3cf1245e8cdfd8dda0b | File hash listed for the INFINITERED dropper. |
| SHA256 | 51a57bfc9ed3eb6451c1c289607814d59e1698c666fb97ac5f694c398f23d045 | File hash listed for the help.php persistence artifact. |
| SHA256 | 58bb25777e0aa86bcd2125101e0bca4e8732b03d91bd8d2f205b446a2a8d5c86 | File hash listed for the INFINITERED dropper. |
| SHA256 | 8f0158855a656b629ca76ebca565f18bc25563ded34b65d6771632c20edb68ec | File hash listed for the help.php persistence artifact. |
| SHA256 | ba6b73b0ca0dc7f86b3b397893ac32d729fd53f9df20643288f141f29d020af7 | File hash listed for the help.php persistence artifact. |
| SHA256 | c1ac43d23f89d41eb4ff131678ab562ab2cfed9aa334b13767ef141d303b0e5b | File hash listed for the help.php persistence artifact. |
| SHA256 | db65c1b9f9e4cb4d729f45ad4b6fcf3e277caf9eb4c875425dec93fd883f9136 | File hash listed for the help.php persistence artifact. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationINFINITERED used Base64-encoded payload markers and code within PHP files.T1056.003 · Web Portal CaptureINFINITERED captured usernames and passwords submitted in REDCap login POST requests.T1071.001 · Web ProtocolsINFINITERED received backdoor commands through the REDCAP-TOKEN HTTP cookie.T1090.003 · Multi-hop ProxyThe article describes traffic routed through compromised routers and other devices in OBF networks.T1114.003 · Email Forwarding RuleUNC6508 created the Patroit content compliance rule to forward matching emails to an actor-controlled account.T1190 · Exploit Public-Facing ApplicationUNC6508 exploited externally facing REDCap servers.T1213 · Data from Information RepositoriesThe actor used keyword patterns in compliance rules to collect selected email communications relating to strategic subjects.T1505.003 · Web ShellThe actor deployed the help.php web shell on the REDCap application.T1554 · Compromise Host Software BinaryINFINITERED modified REDCap system files and injected code during software upgrades.T1555 · Credentials from Password StoresThe actor obtained database and service-account credentials from local configuration information.T1567 · Exfiltration Over Web ServiceThe article identifies email forwarding to an actor-controlled Gmail account as a means of exfiltrating sensitive data.T1689 · Downgrade AttackUNC6508 probed vulnerable legacy REDCap versions and the article describes downgrade attacks.
People
Threat Actors
Malware
Products
Advanced Protection ProgramAdvanced Protection: Consider enrolling highly sensitive accounts in our Advanced Protection Program for additional safeguards against malware and phishing attacks.Chrome Enterprise Password Leak DetectionPassword Protection: Use Chrome Enterprise Password Leak Detection to alert when potentially compromised password use is detected.Google Security OperationsWe have updated Google Security Operations (SecOps) with relevant intelligence, enabling defenders to identify indicators of compromise (IOCs) within their networks.REDCapThe threat actor exploited externally facing REDCap (Research Electronic Data Capture) servers and deployed custom malware named INFINITERED to capture legitimate REDCap login credentials.
Tools
Countries
Industries
Academica People's Republic of China (PRC)-nexus threat actor, targeting institutions in the North American academic, medical, and military research community.MedicalRepublic of China (PRC)-nexus threat actor, targeting institutions in the North American academic, medical, and military research community.Militaryof China (PRC)-nexus threat actor, targeting institutions in the North American academic, medical, and military research community.