
Proofpoint Reports Over 100 Tax-Themed Campaigns Using RMM Tools and Credential Phishing
Summary
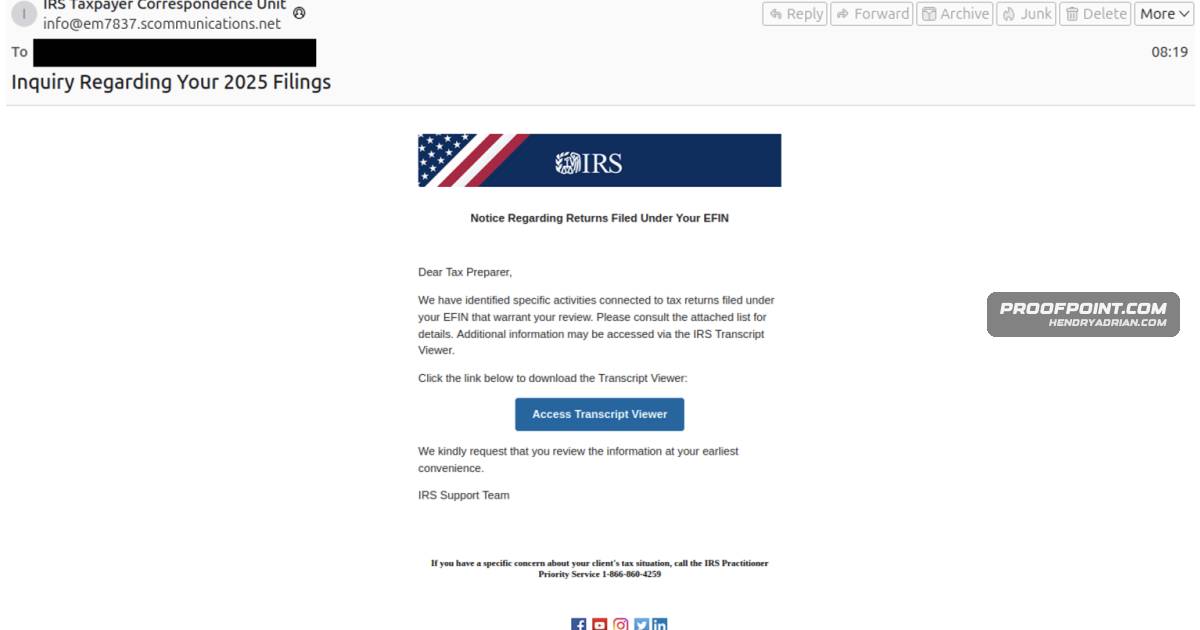
Proofpoint observed over 100 tax-themed campaigns in 2026, using RMM tools, malware, fraud and credential-phishing lures. The campaigns included TA4922 impersonation and TA2730 investment-account phishing.
Key points
- Proofpoint observed over 100 tax-themed campaigns in 2026, mostly targeting the U.S., with activity also reported across countries including Canada, Australia, Switzerland and Japan.
- RMM tools such as Datto, N-Able, RemotePC, Zoho Assist and ScreenConnect were the most common payloads; Proofpoint warned that trusted-tool allow-listing can help prevent abuse.
- TA4922 used tax-authority impersonation and, in some campaigns, requested phone numbers to move communication off email; Proofpoint linked the actor to Winos4.0/ValleyRAT ecosystem components.
- TA2730 used W-8BEN lures and counterfeit investment-account login pages to seek credentials, with campaigns targeting countries including Switzerland and Canada.
- BEC actors impersonated executives or HR contacts to request employee W-2 or W-9 information, which could enable identity theft and follow-on fraud.
- Proofpoint recommends educating users about timely tax-themed lures and notes that such campaigns can occur outside tax-filing season.
Article Details
- Event Type
- Tax-themed phishing, impersonation, and business email compromise campaigns delivering remote-access software and malware, harvesting credentials, and seeking tax and financial information.
- Impact
- Proofpoint observed over a hundred tax-themed campaigns in 2026, predominantly targeting the United States and also affecting organizations and users in multiple other countries. Reported objectives and impacts include gaining remote access, stealing information, taking over investment accounts, and collecting employee tax data that could enable identity theft and follow-on fraud.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | akcjdrya[.]com | Listed among TA2730 phishing domains. |
| DOMAIN | bksgcefzqyb[.]com | Identified as a TA2730 phishing landing domain. |
| DOMAIN | buwxkiy[.]com | Listed among TA2730 phishing domains. |
| DOMAIN | eodrggi[.]com | Listed among TA2730 phishing domains. |
| DOMAIN | gyglowcq[.]com | Listed among TA2730 phishing domains. |
| DOMAIN | iuzndfqr[.]com | Listed among TA2730 phishing domains. |
| DOMAIN | nirbsff[.]com | Listed among TA2730 phishing domains. |
| DOMAIN | rmwztbrr[.]com | Listed among TA2730 phishing domains. |
| DOMAIN | whghfpytehu[.]com | Listed among TA2730 phishing landing domains. |
| DOMAIN | wijgzsfh[.]com | Listed among TA2730 phishing domains. |
aubrey162243her@hotmail[.]com | Listed as a TA4922 sender email associated with tax-themed campaigns. | |
yobutler[.]jonasd8nc29@yahoo[.]com | Listed as a TA4922 reply-to email associated with tax-themed campaigns. | |
| IPV4 | 121[.]127[.]232[.]253 | TA4922 information stealer C2 infrastructure; the article lists it with port 8443. |
| SHA256 | 844202972ff19afa760447fc87963de0fbbc0ebc69d50164f03ecf5d4e67952f | Identified as the N-Able RMM payload hash from a fake IRS campaign. |
| SHA256 | d338a7f85737cac1a7b4b5a1cca94e33d0aa8260548667c6733225d4c20cb848 | Identified as a TA4922 information stealer SHA-256 hash. |
| URL | hxxps[:]//bitbucket[.]org/pmlasobjekightailsians/rgww/downloads/amzn-s3-EfinTranscriptViewer.cm10_14_4_.EXE | Specific Bitbucket payload URL identified in a fake IRS campaign; the downloaded executable installed N-able RMM if executed. |
| URL | hxxps[:]//www[.]upsystems[.]one/Alex[.]exe | Identified as a TA4922 payload URL hosting an executable. |
MITRE ATT&CK
T1071.001 · Web ProtocolsThe article reports web-protocol command-and-control for a TA4922 information stealer.T1105 · Ingress Tool TransferExternal URLs, including a Bitbucket payload URL, were used to deliver executables and tooling.T1204.002 · Malicious FileSome payloads required recipients to execute a file to install RMM software or other malware.T1219 · Remote Access ToolsCampaigns delivered legitimate RMM products that threat actors abused to gain remote access.T1566 · PhishingTax-themed phishing and impersonation messages were used to harvest credentials and prompt follow-on actions.T1566.002 · Spearphishing LinkPhishing emails used links to deliver executables or credential-harvesting landing pages.
Threat Actors
TA2730Proofpoint tracks this credential-phishing actor, which targets financial institutions, especially investment-focused organizations, using phishing kits and counterfeit authentication pages to harvest credentials for investment-account takeover.TA4922Proofpoint tracks this financially motivated actor, which seeks remote access likely for monetization and delivers Winos4.0 ecosystem malware, loaders, and stealers. Proofpoint says the actor is likely based in East Asia and probably Chinese-speaking; reported overlap with the Silver Fox and Void Arachne ecosystem is attributed to third-party researchers.
Malware
ValleyRATTA4922 (likely East Asia–based) delivers Winos4.0/ValleyRAT ecosystem components, information stealers and fraud efforts, frequently impersonates tax authorities, and requests phone numbers to move communicationsWinos4.0TA4922 (likely East Asia–based) delivers Winos4.0/ValleyRAT ecosystem components, information stealers and fraud efforts, frequently impersonates tax authorities, and requests phone numbers to move communications
Products
DattoRMM tools (Datto, NâAble, RemotePC, Zoho Assist, ScreenConnect) were the most common payloads, abused because they are legitimate enterprise software that can evade detection if allow-listing is not enforced.N-Able[T1204.002 ] User Execution: Malicious File – Payloads required user execution to install RMM or stealers (“‘which, if executed, installed N-able RMM.’”).RemotePCRMM tools (Datto, NâAble, RemotePC, Zoho Assist, ScreenConnect) were the most common payloads, abused because they are legitimate enterprise software that can evade detection if allow-listing is not enforced.ScreenConnectRMM tools (Datto, NâAble, RemotePC, Zoho Assist, ScreenConnect) were the most common payloads, abused because they are legitimate enterprise software that can evade detection if allow-listing is not enforced.Zoho AssistRMM tools (Datto, NâAble, RemotePC, Zoho Assist, ScreenConnect) were the most common payloads, abused because they are legitimate enterprise software that can evade detection if allow-listing is not enforced.
Countries
Australiafraud, and credential-phishing lures, predominantly targeting the United States but also Canada, Australia, Switzerland, Japan, and others.CanadaRMM payloads, fraud, and credential-phishing lures, predominantly targeting the United States but also Canada, Australia, Switzerland, Japan, and others.IndiaProofpoint has also observed this actor impersonate revenue agencies of other countries and target users in those regions, including India, Taiwan, Indonesia, Malaysia, and, unusually, Italy.IndonesiaProofpoint has also observed this actor impersonate revenue agencies of other countries and target users in those regions, including India, Taiwan, Indonesia, Malaysia, and, unusually, Italy.ItalyProofpoint has also observed this actor impersonate revenue agencies of other countries and target users in those regions, including India, Taiwan, Indonesia, Malaysia, and, unusually, Italy.Japanlures, predominantly targeting the United States but also Canada, Australia, Switzerland, Japan, and others.MalaysiaProofpoint has also observed this actor impersonate revenue agencies of other countries and target users in those regions, including India, Taiwan, Indonesia, Malaysia, and, unusually, Italy.SingaporeThe actor targets many countries, with its most frequent geographies of interest being Canada, Australia, Singapore, Switzerland and Japan.Switzerlandand credential-phishing lures, predominantly targeting the United States but also Canada, Australia, Switzerland, Japan, and others.TaiwanProofpoint has also observed this actor impersonate revenue agencies of other countries and target users in those regions, including India, Taiwan, Indonesia, Malaysia, and, unusually, Italy.United Statesdelivered malware, RMM payloads, fraud, and credential-phishing lures, predominantly targeting the United States but also Canada, Australia, Switzerland, Japan, and others.