
Analysis of Picus Red Report 2026 Enriches 147 Indicators Across 11 Threats
Summary
An analysis of 11 threats featured in Picus’s Red Report 2026 examined 147 network indicators and related DNS and WHOIS data, finding typosquatting clusters, early risk signals and additional potentially malicious infrastructure.
Key points
- The analysis covered 147 network indicators from 11 threats: 104 domains, 26 subdomains and 17 IP addresses.
- DNS history showed 5,823 domain-to-IP resolutions across 101 indicator domains; sample traffic included 616 client IPs making 4,138 queries to five domains.
- Of the indicator domains, 23 were in bulk-registered typosquatting groups, and 28 were assessed as likely malicious 46–516 days before being reported as indicators.
- WHOIS and email-linkage enrichment found 7,770 additional email-connected domains; the article reports that 25 were weaponized.
- Further enrichment identified 56 additional IP addresses, 46 reported as confirmed malicious, and 186 IP-connected domains, 143 reported as confirmed malicious.
- The article cautions that some entities identified as threats or malicious could later be deemed harmless and recommends further investigation.
Article Details
- Publisher
- CircleID; Picus Security (Red Report 2026)
- Report Period
- Attacks analyzed from 2025; enrichment includes data through 2026-02-19
- Scope
- Picus Security's analysis of 11 featured attacks and associated network indicators
- Sample Size
- 11 attacks; 147 network IoCs
- Key Statistics
- The 147 network IoCs comprised 104 domains, 26 subdomains, and 17 IP addresses.
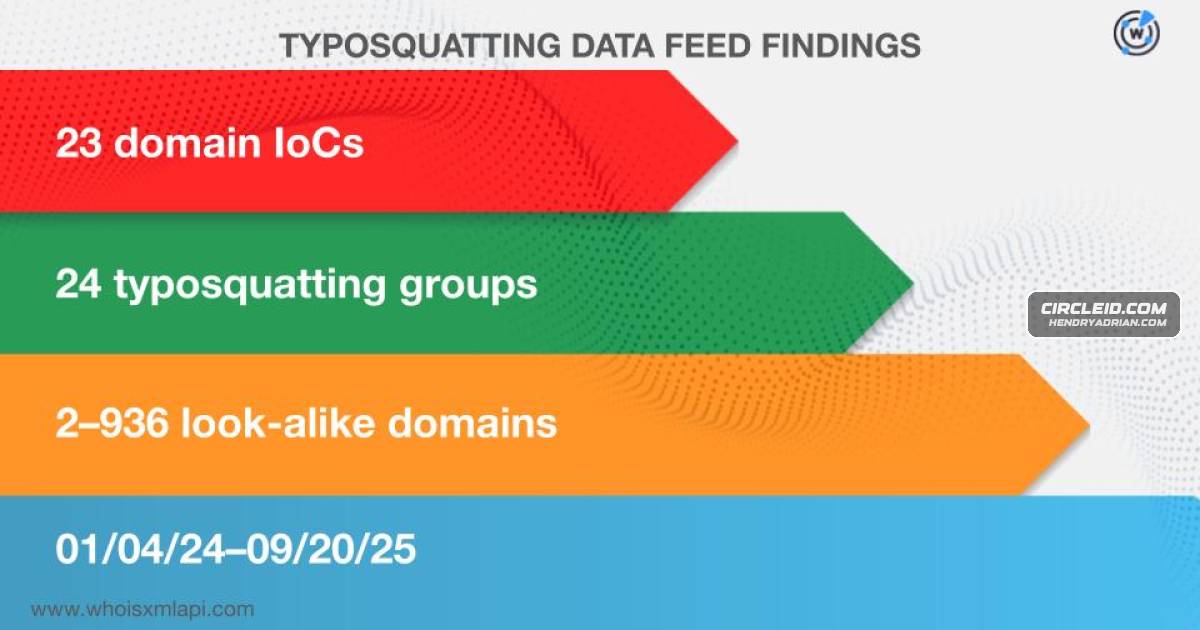
- 23 IoC domains were among 24 typosquatting groups; each was bulk-registered with 2–936 look-alike domains.
- 28 IoC domains were assessed as likely to have turned malicious 46–516 days before being reported as IoCs.
- Between 2026-01-21 and 2026-02-19, 616 unique client IP addresses made 4,138 DNS queries to five IoC domains.
- Threat-intelligence checks identified 25 weaponized domains among 7,770 email-connected domains.
- Recommendations
- Conduct supplementary investigations to corroborate entities identified as threats or malicious, as recommended by the report.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | alace5[.]com | Reported IoC domain associated with XLoader 6 and 7. |
| DOMAIN | carpmaxxbait[.]online | Reported IoC domain associated with XLoader 6 and 7. |
| DOMAIN | cat-watches-site[.]xyz | Reported IoC domain associated with Chihuahua Stealer. |
| DOMAIN | galaxyswapper[.]pro | Reported IoC domain associated with ClickFix. |
| DOMAIN | groupewadesecurity[.]com | Reported IoC domain associated with ClickFix. |
| DOMAIN | lionsdenim[.]xyz | Reported IoC domain associated with APT36 Python-Based ELF Malware. |
| DOMAIN | mediareleaseupdates[.]com | Reported IoC domain associated with STATICPLUGIN. |
| DOMAIN | secssl[.]com | Reported IoC domain associated with SadBridge. |
| DOMAIN | solscan[.]live | Reported IoC domain associated with the Docker Swarm and Kubernetes attack. |
| DOMAIN | symantecsecuritycloud[.]com | Reported IoC domain associated with Earth Ammit. |
| DOMAIN | upload-microsoft[.]com | Reported IoC domain associated with Earth Alux. |
| DOMAIN | wellfitplan[.]ru | Reported IoC domain associated with Operation BarrelFire. |
| IPV4 | 141[.]98[.]80[.]175 | Reported IoC IP address associated with ClickFix. |
| IPV4 | 166[.]88[.]2[.]90 | Reported IoC IP address associated with STATICPLUGIN. |
| IPV4 | 185[.]235[.]137[.]90 | Reported IoC IP address associated with APT36 Python-Based ELF Malware. |
| IPV4 | 192[.]155[.]94[.]199 | Reported IoC IP address associated with the Docker Swarm and Kubernetes attack. |
| IPV4 | 45[.]121[.]50[.]30 | Reported IoC IP address associated with Earth Ammit. |
| IPV4 | 47[.]242[.]198[.]250 | Reported IoC IP address associated with PlushDaemon. |
| IPV4 | 8[.]218[.]222[.]216 | Reported IoC IP address associated with Earth Alux. |
MITRE ATT&CK
T1036 · MasqueradingThe report describes masquerading to disguise malicious files or infrastructure.T1036.008 · Masquerade File TypeUNC6384 reportedly used file-type masquerading to deliver STATICPLUGIN.T1055 · Process InjectionThe report describes multiple threats injecting or hijacking execution in legitimate processes.T1055.002 · Portable Executable InjectionClickFix reportedly used PE injection to execute its final payload in memory.T1055.003 · Thread Execution HijackingNoisyBear reportedly used thread execution hijacking in Operation BarrelFire.T1055.004 · Asynchronous Procedure CallSadBridge Loader and XLoader 6 and 7 reportedly used APC injection to execute code within legitimate processes.T1059 · Command and Scripting InterpreterThe report describes Python and PowerShell use to deliver or execute payloads.T1059.001 · PowerShellChihuahua Stealer reportedly used PowerShell to decode and execute a Base64 payload in memory.T1059.006 · PythonAPT36 or Transparent Tribe reportedly used Python-based ELF malware.T1555 · Credentials from Password StoresEarth Ammit reportedly enumerated credentials saved on compromised systems.T1555.004 · Windows Credential ManagerThe report states that Earth Ammit targeted Windows Credential Manager to enumerate saved credentials.T1562 · Impair DefensesThe report describes defenses being modified, including firewall rules used to intercept and manipulate traffic.T1562.004 · Disable or Modify System FirewallPlushDaemon reportedly modified iptables firewall rules on compromised systems.
Threat Actors
APT36The report states that APT36, or Transparent Tribe, used Python-based ELF malware; it presents the group attribution as an alternative naming rather than independently confirming it.Earth AluxThe report describes Earth Alux querying MachineGUID as a persistent identifier for target hosts.Earth AmmitThe report associates Earth Ammit with credential enumeration on compromised systems.NoisyBearThe report says NoisyBear used thread execution hijacking in Operation BarrelFire.PlushDaemonThe report says PlushDaemon modified firewall rules on compromised systems to intercept and manipulate network traffic.Transparent TribeThe report states that APT36, or Transparent Tribe, used Python-based ELF malware; it presents the group attribution as an alternative naming rather than independently confirming it.UNC6384The report attributes file-type masquerading to UNC6384 in delivering STATICPLUGIN to diplomatic targets.
Malware
Chihuahua StealerSadBridge Loader, XLoader (6 & 7), NoisyBear (Operation BarrelFire), ClickFix, APT36 (Python ELF), Chihuahua Stealer, Earth Ammit, PlushDaemon, Docker Swarm/Kubernetes cryptojacking, and Earth Alux.NoisyBearNotable malware and groups observed include STATICPLUGIN, SadBridge Loader, XLoader (6 & 7), NoisyBear (Operation BarrelFire), ClickFix, APT36 (Python ELF), Chihuahua Stealer, Earth Ammit, PlushDaemon, DockerSadBridge LoaderNotable malware and groups observed include STATICPLUGIN, SadBridge Loader, XLoader (6 & 7), NoisyBear (Operation BarrelFire), ClickFix, APT36 (Python ELF), Chihuahua Stealer, Earth Ammit, PlushDaemon, DockerSTATICPLUGINNotable malware and groups observed include STATICPLUGIN, SadBridge Loader, XLoader (6 & 7), NoisyBear (Operation BarrelFire), ClickFix, APT36 (Python ELF), Chihuahua Stealer, Earth Ammit, PlushDaemon, DockerXLoaderNotable malware and groups observed include STATICPLUGIN, SadBridge Loader, XLoader (6 & 7), NoisyBear (Operation BarrelFire), ClickFix, APT36 (Python ELF), Chihuahua Stealer, Earth Ammit, PlushDaemon, Docker
Products
Docker Swarm(Operation BarrelFire), ClickFix, APT36 (Python ELF), Chihuahua Stealer, Earth Ammit, PlushDaemon, Docker Swarm/Kubernetes cryptojacking, and Earth Alux.KubernetesBarrelFire), ClickFix, APT36 (Python ELF), Chihuahua Stealer, Earth Ammit, PlushDaemon, Docker Swarm/Kubernetes cryptojacking, and Earth Alux.Windows Credential Manager[T1555.004 ] Windows Credential Manager – Earth Ammit specifically targeted Windows Credential Manager to enumerate saved credentials (‘Earth Ammit enumerated credentials saved on compromised systems’)
Tools
PowerShell[T1059 ] Command and Scripting Interpreter – Threat actors abused interpreters such as Python and PowerShell to deliver and execute payloads (‘APT36 or Transparent Tribe demonstrated a significant evolution in theirRuleror disabled defenses such as firewalls to maintain access and manipulate traffic (‘PlushDaemon used the Ruler system to dynamically modify iptables firewall rules to intercept and manipulate networktraffic on