
CERT-EU Attributes European Commission Cloud Breach to TeamPCP; Data May Affect 29+ EU Entities
Summary
CERT-EU attributed the European Commission cloud breach to TeamPCP, saying a stolen AWS key enabled data theft. A ShinyHunters leak may affect 42 Commission clients and at least 29 other EU entities; no sites were taken offline.
Key points
- CERT-EU attributed the March intrusion to TeamPCP and confirmed data was exfiltrated from the Commission’s cloud environment.
- The attackers used an AWS management API key stolen in the Trivy supply-chain attack, then used TruffleHog to find more secrets and added a new access key.
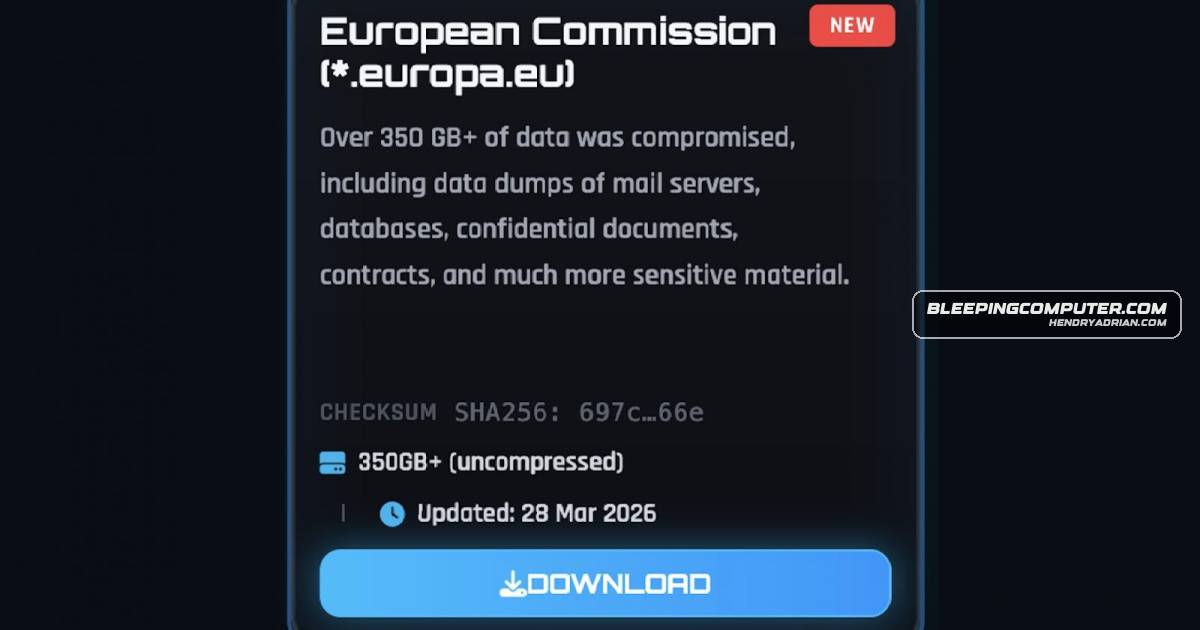
- ShinyHunters published a 90GB archive, approximately 340GB uncompressed, of stolen files.
- CERT-EU said the data may affect 42 internal Commission clients and at least 29 other Union entities using the europa[.]eu web-hosting service.
- The dataset includes personal information and at least 51,992 files related to outbound email; some bounce-back messages may contain user-submitted content.
- No websites were taken offline or tampered with, and no lateral movement to other Commission AWS accounts had been detected.
- The analysis is ongoing; the Commission has notified relevant data protection authorities and is communicating with affected entities.
Article Details
- Victim Organization
- European Commission
- Victim Domain
- europa.eu
- Incident Type
- Unauthorized access to the Commission’s AWS cloud environment and data exfiltration
- Data Types Exposed
- Names and last names
- Usernames
- Email addresses
- Email content, potentially including original user-submitted content in bounce-back notifications
- Affected Records
- CERT-EU confirmed tens of thousands of files containing personal information were stolen. The dataset included at least 51,992 email-related files. The breach potentially affects 42 internal European Commission clients and at least 29 other Union entities.
- Affected Data Size
- The leaked archive was 90 GB (approximately 340 GB uncompressed). Email-related files totaled 2.22 GB.
- Operational Impact
- No websites were taken offline or tampered with. No lateral movement to other Commission AWS accounts had been detected at the time of reporting.
- Ransom Or Extortion
- ShinyHunters published the stolen dataset on its dark web leak site. No ransom demand was reported.
- Claim Status
- confirmed