
Play Ransomware Group Claims Crystal Point
Summary
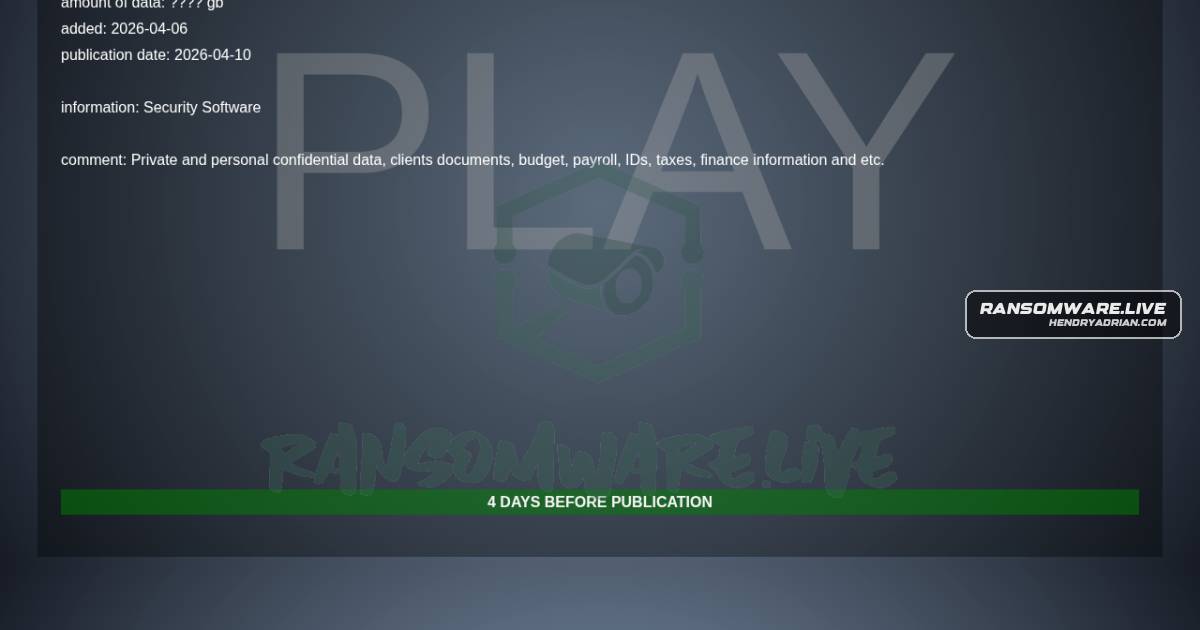
A ransomware.live monitoring record names Crystal Point as a victim in a claim attributed to “play.” The post says the claim is based on public information and that its accuracy could not be confirmed.
Key points
- The record names Crystal Point as the victim and “play” as the ransomware actor.
- It attributes the claim to a linked source and identifies ransomware[.]live as the monitoring service.
- The post says Crystal Point was targeted in a ransomware incident, but explicitly states that the claim’s accuracy could not be confirmed.
- The record lists April 6, 2026, as the discovery and publication date.
Article Details
- Victim
- Crystal Point
- Claim Date
- 2026-04-06
- Encryption Status
- Unknown; not confirmed by the source
- Exfiltration Status
- Unknown; not confirmed by the source
- Ransom Demand
- Unknown; not reported by the source
- Leak Status
- A ransomware claim was reported, but the source does not confirm a data leak or publication.