
Everest claims ransomware attack on Spain’s Umiles Group
Summary
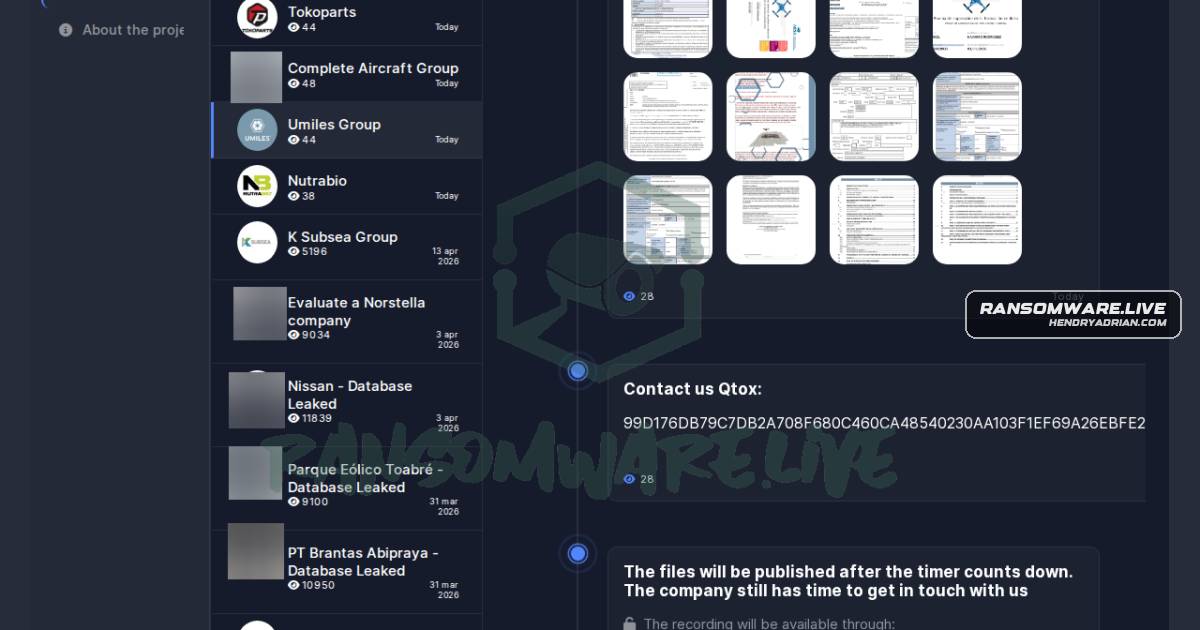
Everest claims it breached Umiles Group, deployed ransomware, and threatened disruption and data exfiltration unless demands were met. The claim is unconfirmed; ransomware.live says it monitors the record.
Key points
- The ransomware.live record attributes the claim to Everest and links to an actor leak-site post.
- Everest claims it breached Umiles Group and deployed ransomware that encrypts critical systems; this is unconfirmed.
- The actor allegedly threatened disruption to Umiles Group’s drone services and data exfiltration unless demands were met.
- Umiles Group is described as a Spain-based drone technology and services company.
Article Details
- Victim
- Umiles Group
- Encryption Status
- Everest claims to have deployed ransomware that encrypts critical systems; unverified.
- Exfiltration Status
- Data exfiltration was threatened; no exfiltration is confirmed.
- Exfiltrated Data
- Unspecified data; the article reports only a threat to exfiltrate data.
- Ransom Demand
- Monetary demands are mentioned, but no amount is disclosed.