
CL-UNK-1211 Targets Government Linux Servers With SysGoRAT and Suspected AI-Generated Scripts
Summary
Unit 42 reported that CL-UNK-1211 targeted government-linked Linux infrastructure from October 2025 to April 2026, using web shells, scripts suspected of AI generation, and SysGoRAT for persistence, reconnaissance and attempted data theft.
Key points
- Unit 42 observed CL-UNK-1211 activity targeting government and state-affiliated Linux infrastructure between October 2025 and April 2026.
- The campaign used open-source tools, custom PHP web shells and a Go remote access trojan called SysGoRAT to maintain access across Linux and Windows systems.
- SysGoRAT reportedly connects to command-and-control over WebSocket using a hard-coded IP address.
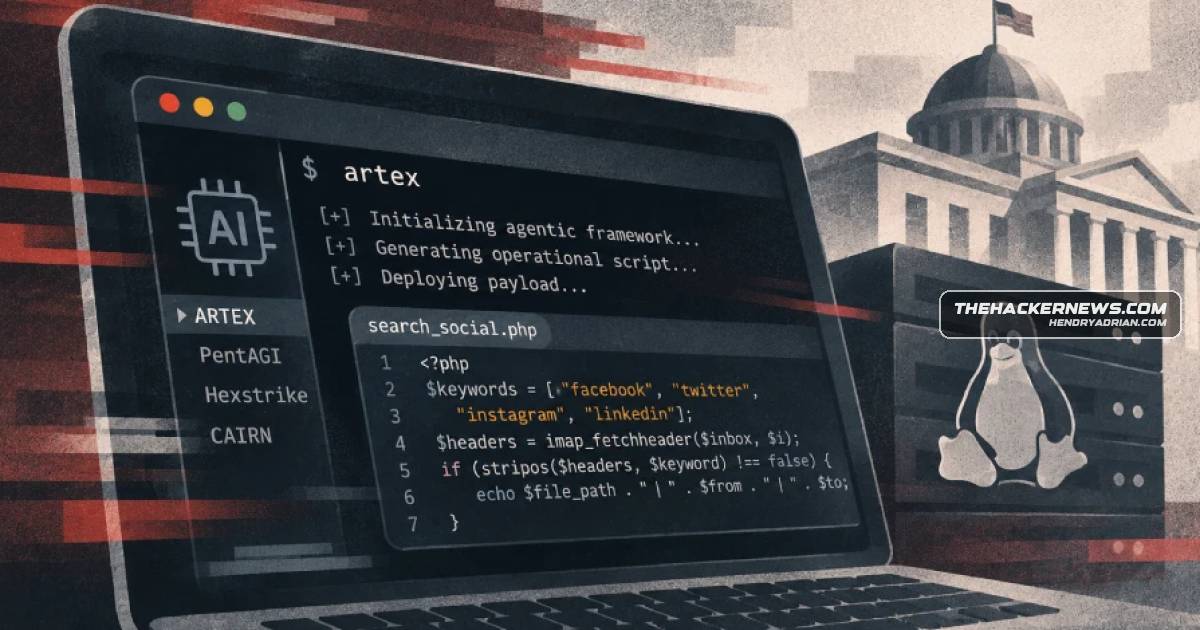
- Researchers said some malicious PHP and shell scripts contained conversational, step-by-step reasoning notes, suggesting they may have been generated by AI or deployed by an AI agent.
- The activity included attempts to disable endpoint protections, wipe logs, gather credentials and search government email for social-media-related messages.
- A script intended to compress selected emails for exfiltration reportedly failed because of syntax errors.
- Unit 42 also described a broader trend of threat actors using agentic offensive frameworks; it said these can increase attack speed but may leave detectable traffic and code traces.
Article Details
- Event Type
- Cyber espionage campaign targeting Linux infrastructure associated with government entities and state-affiliated infrastructure, tracked as CL-UNK-1211.
- Impact
- The campaign involved reconnaissance and attempts to maintain persistent access, dump sensitive databases, and exfiltrate government mailboxes to access social media accounts. The operators also attempted to disable endpoint protections and wipe system logs. A script intended to compress selected emails for exfiltration failed because of syntax errors. Researchers said scripts may have been generated using AI, based on conversational reasoning notes found in them.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 104[.]194[.]158[.]65 | Hard-coded command-and-control IP address used by SysGoRAT over WebSocket. |
MITRE ATT&CK
People
Threat Actors
Malware
Tools
ARTEXMicrosoft, documented threat actors' abuse of open-source agentic penetration testing frameworks like ARTEX, PentAGI, Hexstrike, and CAIRN to carry out a "broad range of actions" across various stages of the attackARTEX PROAlthough ARTEX was taken down by its author after reports of widespread misuse emerged, it has spawned multiple versions, including a commercial offering dubbed ARTEX PRO and a localized variation called ScopeWeaver.Cairnactors' abuse of open-source agentic penetration testing frameworks like ARTEX, PentAGI, Hexstrike, and CAIRN to carry out a "broad range of actions" across various stages of the attack life cycle at an unprecedentedHexstrikethreat actors' abuse of open-source agentic penetration testing frameworks like ARTEX, PentAGI, Hexstrike, and CAIRN to carry out a "broad range of actions" across various stages of the attack life cycle at anPentAGIdocumented threat actors' abuse of open-source agentic penetration testing frameworks like ARTEX, PentAGI, Hexstrike, and CAIRN to carry out a "broad range of actions" across various stages of the attack lifeScopeWeaverAlthough ARTEX was taken down by its author after reports of widespread misuse emerged, it has spawned multiple versions, including a commercial offering dubbed ARTEX PRO and a localized variation called ScopeWeaver.