
ESET Reports About 12 Mongolian Government Systems Infected by GopherWhisper
Summary
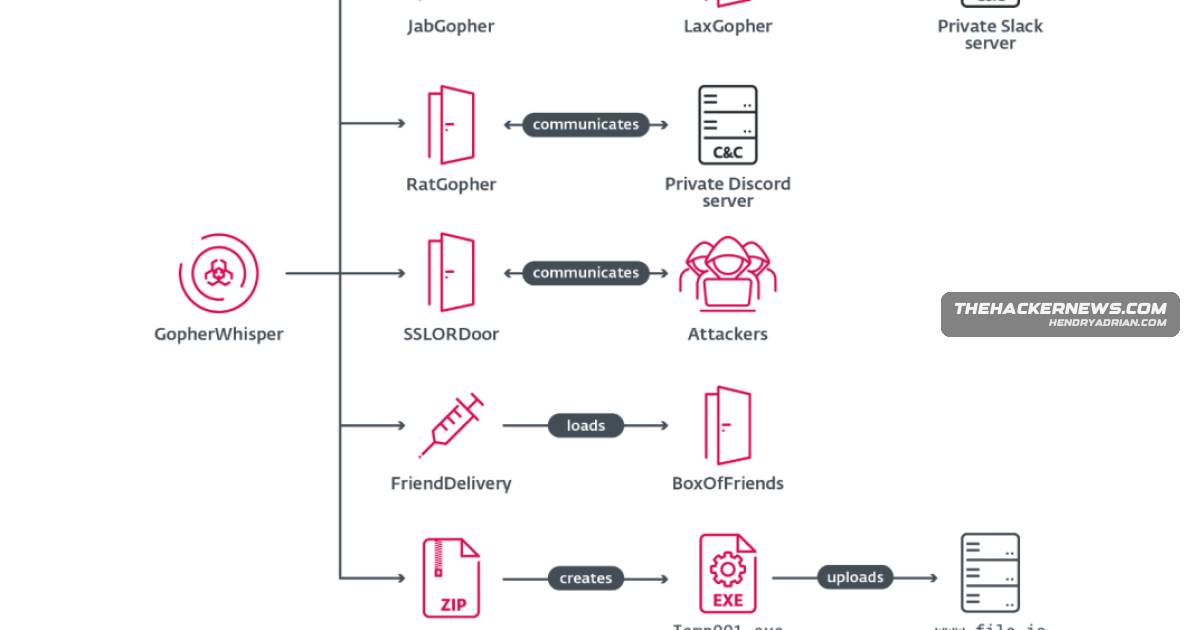
ESET reports that GopherWhisper targeted Mongolian government systems with Go-heavy backdoors, using Discord, Slack, Outlook and file[.]io for C2 or exfiltration. Telemetry showed about 12 infections; initial access is unknown.
Key points
- ESET first discovered GopherWhisper in January 2025 after finding its LaxGopher backdoor on a Mongolian government system.
- ESET telemetry showed about 12 systems associated with a Mongolian government institution infected; C2 traffic indicated dozens of other victims.
- The toolkit includes Go backdoors LaxGopher, RatGopher, CompactGopher and BoxOfFriends, plus the JabGopher and FriendDelivery loaders and the C++ backdoor SSLORDoor.
- The malware uses Slack, Discord and Microsoft Graph API for C2, and file[.]io for file transfer and exfiltration.
- CompactGopher collects files by extension, compresses them into ZIP archives, encrypts them with AES-CFB-128 and exfiltrates them to file[.]io.
- ESET says the initial access method is unknown. Slack and Discord message timestamps aligned with China Standard Time, which ESET cited in assessing the group as China-aligned.
Article Details
- Event Type
- Cyber espionage campaign targeting Mongolian government systems
- Impact
- ESET telemetry showed about 12 infected systems associated with a Mongolian governmental institution. C2 traffic from attacker-controlled Discord and Slack servers indicated dozens of other victims, though the article does not confirm their identities or infection status.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
barrantaya[.]1010@outlook[.]com | Outlook account reportedly created for BoxOfFriends C2, using hard-coded credentials to craft draft emails. |
MITRE ATT&CK
T1005 · Data from Local SystemCompactGopher reportedly collected files of interest from infected systems.T1059.003 · Windows Command ShellLaxGopher and SSLORDoor reportedly executed commands via cmd.exe.T1102 · Web ServiceThe backdoors reportedly used Discord, Slack, and Microsoft 365 Outlook as web services for command-and-control.T1567.002 · Exfiltration to Cloud StorageCompactGopher reportedly exfiltrated compressed files of interest to file.io.
People
Threat Actors
Malware
BoxOfFriendsFriendDelivery, a malicious DLL that serves as a loader and injector for BoxOfFriends.CompactGopherThe group uses multiple Go-based implants such as LaxGopher, RatGopher, and CompactGopher.FriendDeliveryLoaders and injectors include JabGopher and FriendDelivery, while SSLORDoor provides a C++ remote-access backdoor.JabGopherLoaders and injectors include JabGopher and FriendDelivery, while SSLORDoor provides a C++ remote-access backdoor.LaxGopher#GopherWhisper #LaxGopherRatGopherThe group uses multiple Go-based implants such as LaxGopher, RatGopher, and CompactGopher.SSLORDoorLoaders and injectors include JabGopher and FriendDelivery, while SSLORDoor provides a C++ remote-access backdoor.
Products
DiscordThe actor abused legitimate services including Discord, Slack, Microsoft 365 Outlook, and file[.]io for command-and-control and exfiltration, with telemetry showing about a dozen confirmed infections and activity timedfile.io“GopherWhisper abuses legitimate services, notably Discord, Slack, Microsoft 365 Outlook, and file.io for command-and-control (C&C) communication and exfiltration.”Microsoft 365 OutlookThe actor abused legitimate services including Discord, Slack, Microsoft 365 Outlook, and file[.]io for command-and-control and exfiltration, with telemetry showing about a dozen confirmed infections and activity timedSlackThe actor abused legitimate services including Discord, Slack, Microsoft 365 Outlook, and file[.]io for command-and-control and exfiltration, with telemetry showing about a dozen confirmed infections and activity timed