
Malicious PyTorch Lightning and Intercom npm Releases Target Developer Credentials
Summary
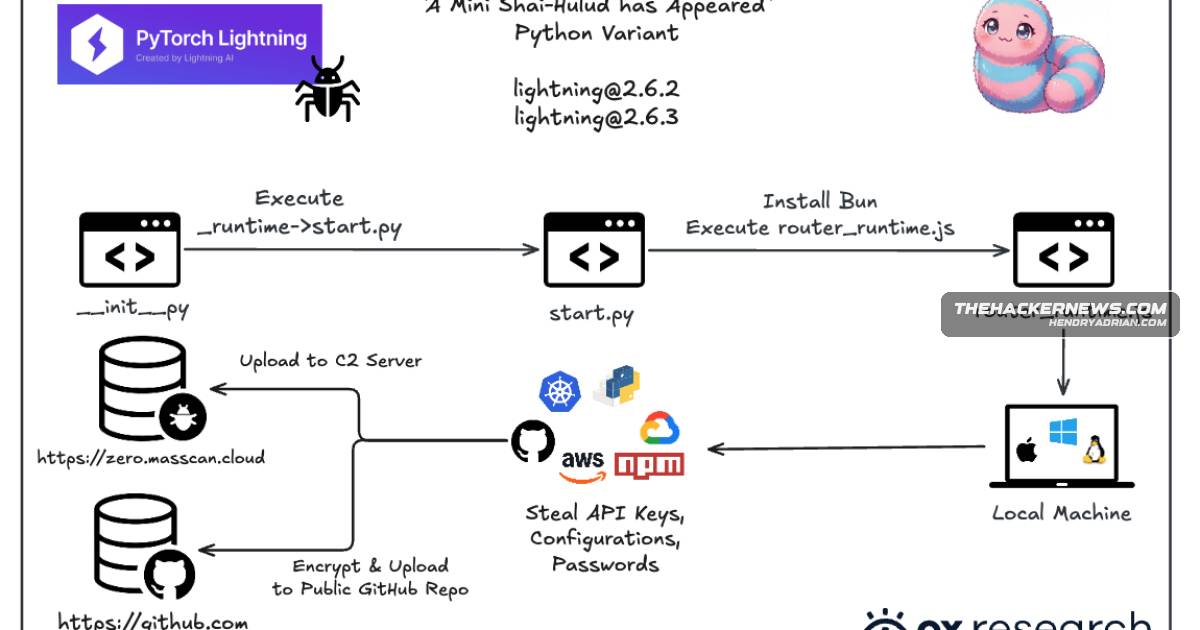
Malicious PyPI releases of PyTorch Lightning 2.6.2 and 2.6.3 run credential-stealing code on import; intercom-client 7.0.4 was also compromised. PyPI quarantined the project, and the campaign is assessed to extend Mini Shai-Hulud.
Key points
- PyTorch Lightning versions 2.6.2 and 2.6.3, published April 30, 2026, contained malicious code; PyPI quarantined the project.
- Importing the affected package triggers a downloader that runs Bun and an obfuscated JavaScript payload intended to steal credentials.
- The malware validates harvested GitHub tokens and uses them to inject worm-like commits into up to 50 branches per repository the token can write to, impersonating Anthropic’s Claude Code.
- An npm postinstall hook can modify local packages and repack them, enabling further propagation if developers publish the tampered packages.
- The intercom-client 7.0.4 npm release was also reported compromised as part of the Mini Shai-Hulud campaign, using a preinstall hook.
- The project advised removing affected versions, downgrading to 2.6.1, and rotating exposed credentials; maintainers said they were investigating the root cause.
Article Details
- Event Type
- Software supply-chain compromise involving malicious PyPI and npm package releases
- Impact
- PyTorch Lightning versions 2.6.2 and 2.6.3 reportedly execute credential-stealing code on import; stolen GitHub tokens were used to inject worm-like commits into up to 50 branches per repository. An npm postinstall propagation mechanism could pass the malware to downstream users if tampered packages were published. Version 7.0.4 of intercom-client was also reported compromised. PyPI quarantined the PyTorch Lightning project; the article advises removing affected versions, downgrading to 2.6.1, and rotating exposed credentials.
MITRE ATT&CK
T1059.006 · PythonThe attack chain uses a Python script, start.py, to download and execute the Bun runtime.T1059.007 · JavaScriptThe Bun runtime executes an obfuscated JavaScript payload used for credential theft.T1195.001 · Compromise Software Dependencies and Development ToolsMalicious PyTorch Lightning and intercom-client package releases compromised software dependencies and executed code in affected environments.T1528 · Steal Application Access TokenThe malware harvests GitHub tokens, validates them, and uses them to inject commits into repositories.
Threat Actors
LAPSUS$TeamPCP reportedly called LAPSUS$ a partner and claimed it was heavily involved in the operation; this involvement is presented as TeamPCP's claim.TeamPCPThe article attributes a series of supply-chain compromises to TeamPCP and reports that this PyTorch Lightning campaign is assessed to extend the Mini Shai-Hulud activity.