
Rogue Checkmarx Jenkins AST Plugin Published After Repository Compromise
Summary
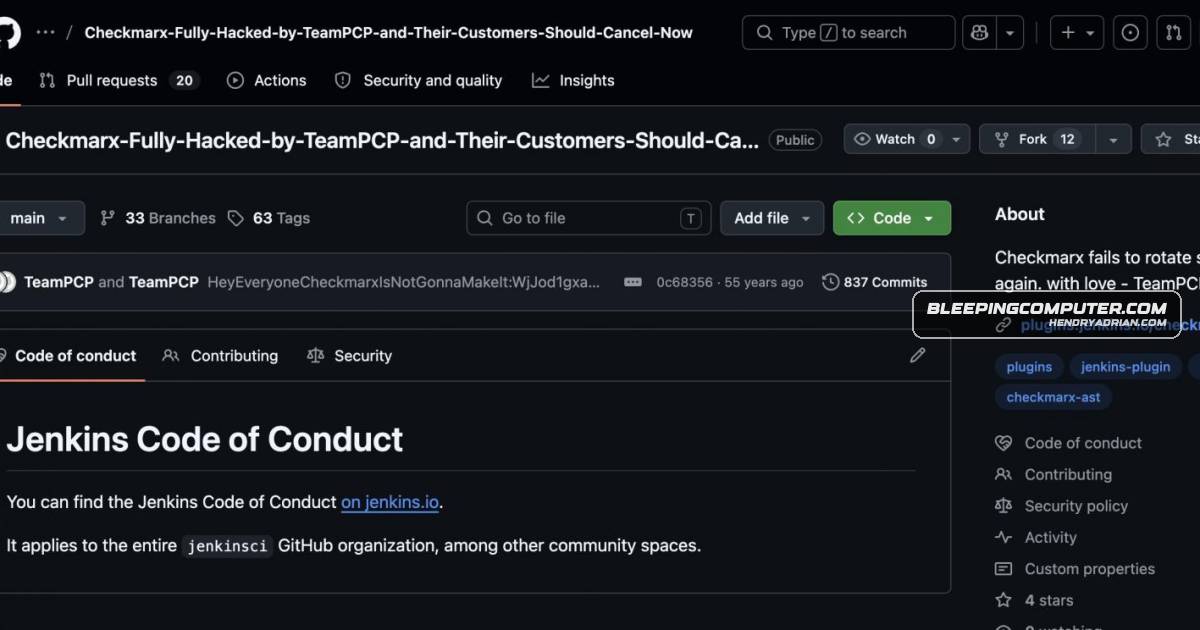
Checkmarx said attackers using credentials stolen in the Trivy supply-chain attack accessed its GitHub environment and published a rogue Jenkins AST plugin containing malicious code. Its behavior is unknown; users should rotate secrets and investigate.
Key points
- A rogue Checkmarx Jenkins AST plugin version, 2026.5.09, was uploaded on May 9 outside the official release pipeline, without a Git tag or GitHub release.
- TeamPCP claimed responsibility; Checkmarx said credentials obtained in the Trivy supply-chain attack were used to access its GitHub repositories.
- A security engineer said the plugin was backdoored to deliver credential-stealing malware, but Checkmarx has not detailed what the rogue plugin does.
- Checkmarx said its GitHub repositories are isolated from its customer production environment and contain no customer data.
- Checkmarx advised users who downloaded the rogue version to assume their credentials are compromised, rotate secrets, and investigate for persistence or lateral movement.
- Checkmarx recommends version 2.0.13-829.vc72453fa_1c16 or an older version and published malicious artifacts for defenders to use as indicators of compromise.
Article Details
- Victim Organization
- Checkmarx
- Incident Type
- Supply-chain compromise involving publication of a malicious Checkmarx Jenkins AST plugin
- Incident Date
- 2026-05-09
- Data Types Exposed
- Credentials (potentially compromised for users who downloaded the malicious plugin; theft was not confirmed)
- Affected Records
- Unknown
- Affected Data Size
- Not disclosed
- Operational Impact
- A rogue plugin version was published to the Jenkins Marketplace and repo.jenkins-ci.org outside Checkmarx's release pipeline. Checkmarx advised users who downloaded it to rotate secrets and investigate for persistence or lateral movement. The article reports no confirmed customer-data exposure.
- Ransom Or Extortion
- Unknown
- Claim Status
- confirmed
MITRE ATT&CK
People
Threat Actors
LAPSUS$The article says Checkmarx confirmed that LAPSUS$ leaked data stolen from its private GitHub repository in a separate incident in late April.TeamPCPThe group claimed responsibility for the Checkmarx supply-chain compromise. The article reports that it used credentials obtained in the Trivy supply-chain attack to access Checkmarx repositories and publish malicious code.
Vendors
Products
Checkmarx ASTThe Checkmarx AST plugin on the Jenkins Marketplace integrates security scanning into automated pipelines.JenkinsCheckmarx warned that a rogue version of its Jenkins AST plugin was published on the Jenkins Marketplace after TeamPCP compromised its GitHub repositories and used stolen credentials to push malicious code.