
Gamaredon Uses WinRAR Vulnerability to Deliver Malware in Ukraine
Summary
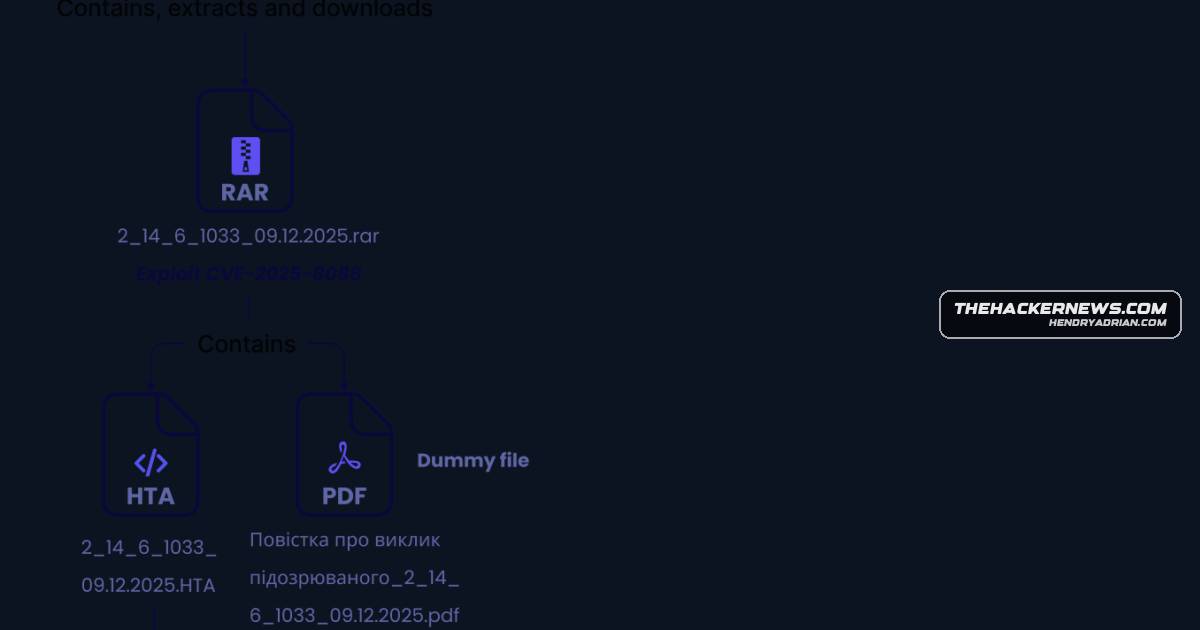
Sekoia linked Gamaredon activity targeting Ukraine to exploitation of WinRAR CVE-2025-8088. The reported chain uses GammaPhish and GammaLoad to deliver malware for persistence, propagation and file theft; GammaWorm's deployment path remains unclear.
Key points
- Sekoia observed the infection chain in January 2026 and attributed it to Gamaredon, which it says weaponized WinRAR CVE-2025-8088.
- GammaPhish is assessed to deploy GammaLoad, which can retrieve and execute additional VBScript payloads.
- GammaWorm uses scheduled tasks for persistence and can replace files in network shares and USB drives with malicious LNK files.
- GammaWorm resolves C2 through a hard-coded public Telegram channel and uses NTFS Alternate Data Streams to conceal modules.
- GammaSteel collects files matching selected extensions and exfiltrates them to an AWS S3 bucket or an attacker-controlled fallback server.
- Sekoia said GammaWipe may also be distributed; GammaWorm's exact deployment path remains ambiguous.
Article Details
- Attack Vectors
- Gamaredon used CVE-2025-8088 in WinRAR to launch the GammaPhish HTML Application payload, which retrieves GammaLoad.
- GammaWorm can spread through network shares and USB drives, replacing legitimate directories with malicious LNK files. The article says its exact deployment path is ambiguous and may involve a weaponized USB drive.
- UAC-0184 used LNK lures to deliver an executable associated with PassMark BurnInTest against Ukrainian military-related targets.
- UAC-0247 used ZIP archives to deliver HTA droppers targeting drone operators.
- APT28-attributed campaigns exploited Microsoft Office vulnerability CVE-2026-21509 to extract a COVENANT Grunt implant.
MITRE ATT&CK
T1053.005 · Scheduled TaskGammaWorm maintains persistence using scheduled tasks.T1059.005 · Visual BasicGammaLoad retrieves and runs additional VBScript payloads.T1080 · Taint Shared ContentGammaWorm spreads through network shares and replaces legitimate directories with malicious LNK files.T1082 · System Information DiscoveryThe operators' stated objectives include fingerprinting the infected host system.T1091 · Replication Through Removable MediaGammaWorm is reported to spread through USB drives; the article also says a weaponized USB drive may introduce it.T1102.001 · Dead Drop ResolverGammaWorm sends a GET request to a hard-coded public Telegram channel to resolve its C2.T1105 · Ingress Tool TransferGammaLoad retrieves additional VBScript payloads from C2 servers.T1112 · Modify RegistryThe reported infection chain updates network configuration in the registry.T1203 · Exploitation for Client ExecutionThe article reports exploitation of CVE-2025-8088 in WinRAR to launch GammaPhish, and Microsoft Office CVE-2026-21509 in campaigns attributed to APT28.T1204.002 · Malicious FileThe article reports LNK lures in UAC-0184 activity and malicious LNK files used in GammaWorm's propagation chain.T1564.004 · NTFS File AttributesGammaWorm uses NTFS Alternate Data Streams to conceal its core modules.T1566.001 · Spearphishing AttachmentThe article says Gamaredon has historically targeted Ukraine with spear-phishing emails containing malicious attachments.T1567.002 · Exfiltration to Cloud StorageGammaSteel exfiltrates files to an AWS S3 bucket or, as a fallback, an attacker-controlled server.
CVE
CVE-2025-8088Gamaredon has been linked to a WinRAR exploit chain using CVE-2025-8088 to deploy GammaPhish, GammaLoad, GammaWorm, and GammaSteel for espionage, persistence, and data theft.CVE-2026-21509loader attributed to APT28 in connection with campaigns exploiting a Microsoft Office vulnerability (CVE-2026-21509), to extract a COVENANT Grunt implant.
Threat Actors
APT28The article attributes PixyNetLoader to APT28 and links it to campaigns exploiting Microsoft Office CVE-2026-21509 to extract a COVENANT Grunt implant.GamaredonThe article attributes the WinRAR exploitation and Gamma malware infection chain to Gamaredon, which it describes as a Russian state-sponsored intrusion set officially linked to the FSB.UAC-0184The article reports that UAC-0184 targeted Ukrainian military-related targets with LNK lures delivering an executable associated with PassMark BurnInTest.UAC-0244The article identifies UAC-0244 as a previous tracking name for UAC-0247, a cluster reported to target Ukrainian drone operators.UAC-0247The article reports that UAC-0247 targeted Ukrainian drone operators with ZIP-delivered HTA droppers and a backdoor capable of establishing a reverse shell. It says this cluster was previously tracked as UAC-0244.
Malware
Covenant Gruntconnection with campaigns exploiting a Microsoft Office vulnerability (CVE-2026-21509), to extract a COVENANT Grunt implant.GamaWiperSekoia said the infection sequences could be used to distribute other malware families, such as GammaWipe (aka GamaWiper), depending on the threat actor’s objectives.GammaLoadGamaredon has been linked to a WinRAR exploit chain using CVE-2025-8088 to deploy GammaPhish, GammaLoad, GammaWorm, and GammaSteel for espionage, persistence, and data theft.GammaPhishGamaredon has been linked to a WinRAR exploit chain using CVE-2025-8088 to deploy GammaPhish, GammaLoad, GammaWorm, and GammaSteel for espionage, persistence, and data theft.GammaSteelGamaredon has been linked to a WinRAR exploit chain using CVE-2025-8088 to deploy GammaPhish, GammaLoad, GammaWorm, and GammaSteel for espionage, persistence, and data theft.GammaWipe#GamaredonGammaWormGamaredon has been linked to a WinRAR exploit chain using CVE-2025-8088 to deploy GammaPhish, GammaLoad, GammaWorm, and GammaSteel for espionage, persistence, and data theft.PixyNetLoader#Gamaredon
Vendors
Amazon Web Servicescodenamed GammaSteel that captures files matching certain extensions and exfiltrates them to an Amazon Web Services (AWS) S3 bucket or an attacker-controlled server as a fallback mechanism.Microsoftof PixyNetLoader, a malware loader attributed to APT28 in connection with campaigns exploiting a Microsoft Office vulnerability (CVE-2026-21509), to extract a COVENANT Grunt implant.
Products
Microsoft Officeof PixyNetLoader, a malware loader attributed to APT28 in connection with campaigns exploiting a Microsoft Office vulnerability (CVE-2026-21509), to extract a COVENANT Grunt implant.PassMark BurnInTestThe development coincides with UAC-0184‘s targeting of Ukrainian military-related targets to deliver an executable associated with a legitimate program called PassMark BurnInTest via LNK lures.TelegramThe activity targets Ukraine and uses obfuscation techniques like Telegram-based C2 resolution, NTFS ADS, and malicious LNK files, while other threat clusters and APT28 continue to target Ukrainian entities withWinRARGamaredon has been linked to a WinRAR exploit chain using CVE-2025-8088 to deploy GammaPhish, GammaLoad, GammaWorm, and GammaSteel for espionage, persistence, and data theft.
Countries
Industries
Critical infrastructureService (FSB), has a history of targeting Ukraine, particularly government, military, and critical infrastructure entities, using spear-phishing emails containing malicious attachments, in this booby-trapped RARGovernmentlinked to the Federal Security Service (FSB), has a history of targeting Ukraine, particularly government, military, and critical infrastructure entities, using spear-phishing emails containing maliciousMilitaryto the Federal Security Service (FSB), has a history of targeting Ukraine, particularly government, military, and critical infrastructure entities, using spear-phishing emails containing malicious attachments, in