
Leaked Shai-Hulud Clone Found in Malicious npm Packages
Summary
OXsecurity found four malicious npm packages that steal developer data; one contains a leaked Shai-Hulud clone and another adds DDoS capabilities. The packages had 2,678 downloads, and researchers advised removal and credential rotation.
Key points
- OXsecurity reported four malicious npm packages published by the account deadcode09284814, with 2,678 combined downloads.
- The chalk-tempalte package contained a non-obfuscated clone of leaked Shai-Hulud malware targeting developer credentials, secrets, crypto wallet data and account information.
- All four packages included data-exfiltration routines; the malware sent stolen information to 87e0bbc636999b[.]lhr[.]life.
- The malware retained functionality to upload stolen credentials to public, automatically generated GitHub repositories.
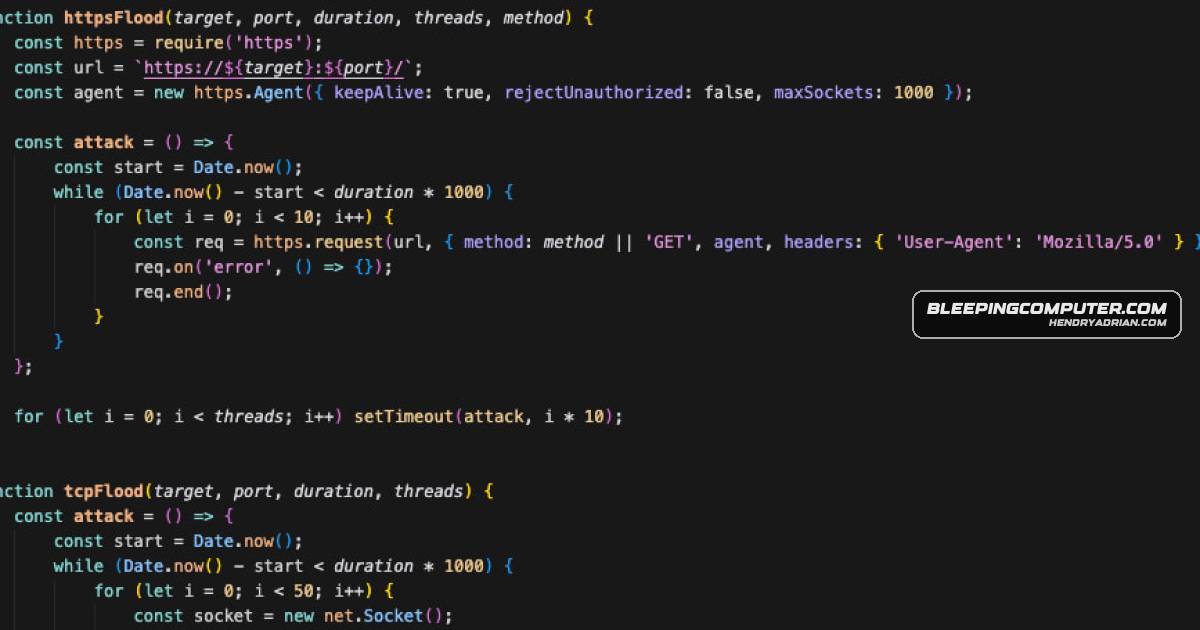
- The axois-utils package also supported HTTP, TCP and UDP floods and TCP reset attacks; researchers found references to a “phantom bot.”
- OXsecurity advised developers who downloaded the packages to remove them and rotate credentials and API keys on affected systems.
Article Details
- Event Type
- Malicious npm package campaign distributing a Shai-Hulud clone and infostealers, with one package also containing DDoS bot functionality.
- Impact
- The packages were reported to steal developer credentials, secrets, cryptocurrency wallet data, account information, and configuration files, and to exfiltrate data. The axois-utils package additionally contained HTTP, TCP, UDP, and TCP reset DDoS capabilities. OXsecurity reported 2,678 combined downloads and advised affected developers to remove the packages and rotate credentials and API keys.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| HOSTNAME | 87e0bbc636999b[.]lhr[.]life | Reported command-and-control server used by the malware to exfiltrate stolen information. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe malware reportedly exfiltrated stolen information to a command-and-control server.T1195.002 · Compromise Software Supply ChainMalicious packages were published to npm and distributed a malware clone through the software supply chain.T1567.001 · Exfiltration to Code RepositoryThe malware retained functionality to upload stolen credentials to public, auto-generated GitHub repositories.
Threat Actors
Malware
Products
GitHubThe malware emerged on GitHub last week, with a message allegedly from TeamPCP saying “Here We Go Again – Let the Carnage Continue.npmNew malicious npm packages have been found carrying a leaked Shai-Hulud clone that steals developer credentials, secrets, crypto wallet data, and account information.