
GitHub Investigates Internal Repository Access Claimed by TeamPCP
Summary
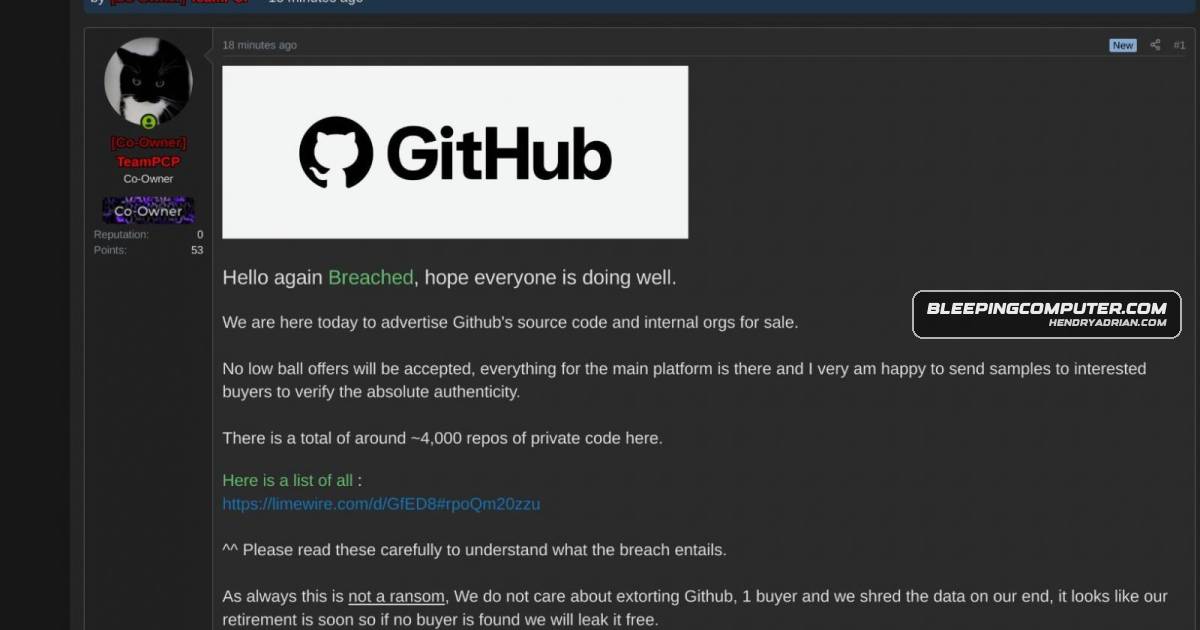
GitHub is investigating unauthorized access to internal repositories after TeamPCP claimed it accessed about 4,000 private-code repositories and offered them for sale. GitHub says it has no evidence of impact to customer data outside its internal repositories.
Key points
- GitHub said it is investigating unauthorized access to its internal repositories.
- TeamPCP claimed on the Breached forum that it accessed about 4,000 private-code repositories and sought offers of at least $50,000; the article does not independently confirm the claimed access or theft.
- GitHub said it has no evidence that customer information stored outside its internal repositories was affected.
- GitHub said it will notify affected customers through established channels if evidence of impact is found.
- The article links TeamPCP to previous supply-chain attacks involving GitHub, PyPI, NPM, Docker, and Trivy.
- The reported Trivy-related activity was linked to compromises affecting Aqua Security Docker images and Checkmarx KICS, and to LiteLLM infections involving TeamPCP Cloud Stealer.
Article Details
- Victim Organization
- GitHub
- Victim Domain
- github.com
- Incident Type
- Unauthorized access to GitHub internal repositories; TeamPCP claims it accessed and stole private code repositories.
- Data Types Exposed
- Private source code
- Affected Records
- TeamPCP claimed approximately 4,000 private repositories were accessed.
- Affected Data Size
- Not disclosed
- Operational Impact
- GitHub is investigating unauthorized access to its internal repositories. It said it had no evidence at the time of reporting that customer information stored outside those repositories was affected.
- Ransom Or Extortion
- TeamPCP asked for offers of at least $50,000 to sell the repositories, said it would delete its copy if a buyer was found, and threatened to leak the data for free if there was no buyer. The group said it was not seeking a ransom.
- Claim Status
- claimed
Threat Actors
Malware
Vendors
Aqua SecurityThe group has a history of supply chain attacks across GitHub, PyPI, NPM, and Docker, including incidents tied to Aqua Security, Trivy, LiteLLM, and the “TeamPCP Cloud Stealer” malware.CheckmarxIn March, the hacker group also compromised Aqua Security’s Trivy vulnerability scanner, which is believed to have led to cascading compromises affecting Aqua Security Docker images and the Checkmarx KICS project.GitHubGitHub is investigating unauthorized access to its internal repositories after TeamPCP claimed to have stolen about 4,000 private code repositories and offered them for sale.Mistral AIPast TeamPCP activity includes compromises of Aqua Security, Trivy, LiteLLM, and the Mistral AI source code.
Products
DockerThe group has a history of supply chain attacks across GitHub, PyPI, NPM, and Docker, including incidents tied to Aqua Security, Trivy, LiteLLM, and the “TeamPCP Cloud Stealer” malware.GitHubGitHub is investigating unauthorized access to its internal repositories after TeamPCP claimed to have stolen about 4,000 private code repositories and offered them for sale.LiteLLMThe group has a history of supply chain attacks across GitHub, PyPI, NPM, and Docker, including incidents tied to Aqua Security, Trivy, LiteLLM, and the “TeamPCP Cloud Stealer” malware.npmThe group has a history of supply chain attacks across GitHub, PyPI, NPM, and Docker, including incidents tied to Aqua Security, Trivy, LiteLLM, and the “TeamPCP Cloud Stealer” malware.PyPIThe group has a history of supply chain attacks across GitHub, PyPI, NPM, and Docker, including incidents tied to Aqua Security, Trivy, LiteLLM, and the “TeamPCP Cloud Stealer” malware.TrivyThe group has a history of supply chain attacks across GitHub, PyPI, NPM, and Docker, including incidents tied to Aqua Security, Trivy, LiteLLM, and the “TeamPCP Cloud Stealer” malware.