
Weekly Security Briefing: GitHub Repository Theft, TeamPCP PyPI Attack and AI Security Moves
Summary
A weekly security roundup covers GitHub's confirmed theft of internal repositories via a poisoned VS Code extension, TeamPCP's malicious durabletask releases, DBIR findings, Mythos exploit research, and security product and industry developments.
Key points
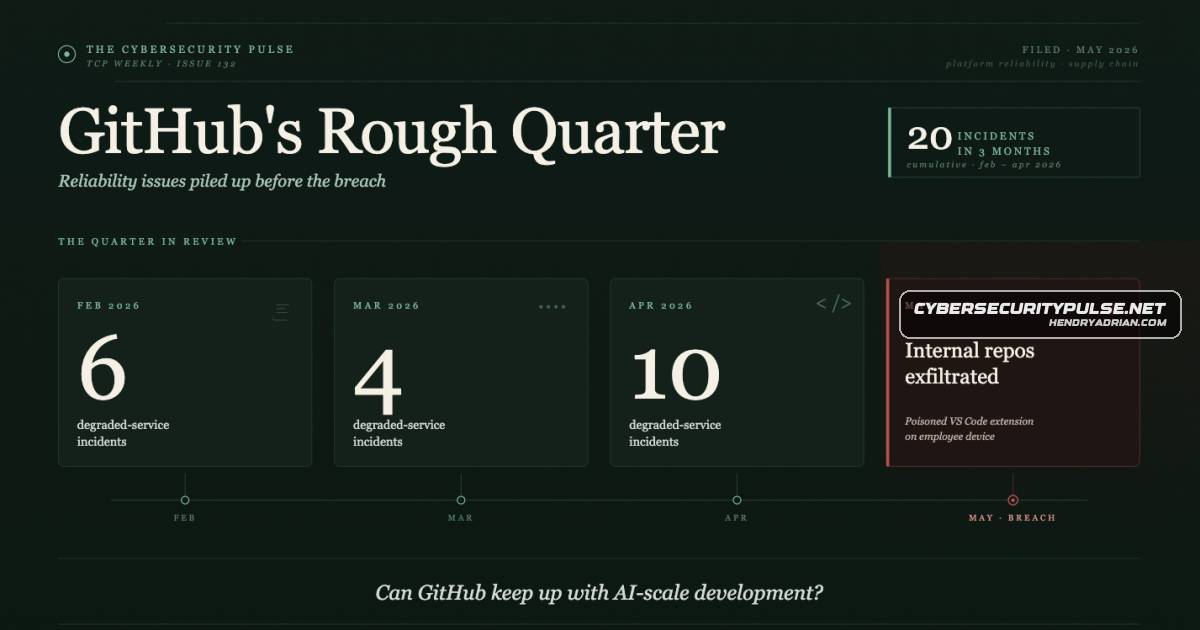
- GitHub said attackers used a poisoned VS Code extension to compromise an employee device and exfiltrate internal repositories; it reported no evidence that customer repositories were affected.
- Wiz linked malicious durabletask PyPI versions 1.4.1–1.4.3 to TeamPCP; the payload targeted cloud and other secrets, and PyPI quarantined the packages.
- Verizon's 2026 DBIR analyzed 31,000+ incidents and 22,000+ confirmed breaches; vulnerability exploitation was the top initial access vector at 31%, ahead of credential abuse at 13%.
- Cloudflare said Mythos Preview chained low-severity bugs into working exploits across 50+ repositories, and described a research harness involving validation and reachability analysis.
- Reporting said Mythos helped researchers develop a macOS privilege-escalation chain that reportedly bypassed Apple's Memory Integrity Enforcement on M5 systems.
- OpenAI announced Daybreak, an initiative using its models and Codex Security to find, validate, patch, and verify software vulnerabilities.
- Akamai agreed to acquire LayerX for about $205 million; Torq acquired Jit, while Tanium and ServiceNow announced an endpoint patching and remediation offering.
Article Details
- Event Type
- Security news roundup covering a GitHub internal-repository breach, a TeamPCP-attributed malicious PyPI package compromise, vulnerability-exploitation trends, and AI-assisted exploit research.
- Impact
- GitHub said attackers compromised an employee device through a poisoned VS Code extension and exfiltrated internal repositories; it reported no evidence so far that customer repositories were affected. The Register reported that a claim of roughly 3,800 stolen repositories was directionally consistent with GitHub’s investigation. Wiz linked TeamPCP to malicious durabletask PyPI versions that stole cloud, Kubernetes, Vault, filesystem, and password-manager secrets; PyPI quarantined the packages after Wiz’s analysis. Separately, Verizon’s DBIR reported vulnerability exploitation as the leading initial access vector at 31%. Cloudflare found Mythos Preview could chain bugs into working exploits across more than 50 internal repositories, while reporting on Calif’s research said a Mythos-assisted chain reportedly bypassed Apple’s Memory Integrity Enforcement on M5 systems and enabled standard-user root access on macOS 26.4.1.
MITRE ATT&CK
Threat Actors
Vendors
Anthropicthe latest DBIR findings, TeamPCP’s malicious durabletask PyPI compromise, and Cloudflare’s testing of Anthropic’s Mythos for exploit chaining.AppleAnthropic’s unreleased Claude Mythos Preview helped researchers find a macOS privilege escalation chain that reportedly bypassed Apple’s Memory Integrity Enforcement on M5 systems.CloudflareCode extension incident, the latest DBIR findings, TeamPCP’s malicious durabletask PyPI compromise, and Cloudflare’s testing of Anthropic’s Mythos for exploit chaining.GitHubThe Cybersecurity Pulse covers a week of major security news, including GitHub’s poisoned VS Code extension incident, the latest DBIR findings, TeamPCP’s malicious durabletask PyPI compromise, and Cloudflare’s testingMicrosoftTeamPCP compromised durabletask, Microsoft’s official Python client for the Durable Task framework, publishing malicious PyPI versions 1.4.1, 1.4.2, and 1.4.3.VerizonVerizon’s DBIR 2026 found vulnerability exploitation is now the top initial access vector.WizWiz tied the attack to the earlier @antv wave: a compromised GitHub account likely dumped repo secrets, exposed the PyPI token, and let the actor publish directly.
Products
Claude Mythos PreviewCloudflare tested Anthropic’s Mythos Preview across 50+ internal repos and found the model was best at the part scanners usually botch: turning small primitives into a working exploit chain.DurableTaskincluding GitHub’s poisoned VS Code extension incident, the latest DBIR findings, TeamPCP’s malicious durabletask PyPI compromise, and Cloudflare’s testing of Anthropic’s Mythos for exploit chaining.GitHubThe Cybersecurity Pulse covers a week of major security news, including GitHub’s poisoned VS Code extension incident, the latest DBIR findings, TeamPCP’s malicious durabletask PyPI compromise, and Cloudflare’s testingM5ð Mythos bypasses Mac defenses — Calif used Mythos to help build a macOS kernel LPE chain on M5 in five days.macOSð Mythos bypasses Mac defenses — Calif used Mythos to help build a macOS kernel LPE chain on M5 in five days.PyPIGitHub’s poisoned VS Code extension incident, the latest DBIR findings, TeamPCP’s malicious durabletask PyPI compromise, and Cloudflare’s testing of Anthropic’s Mythos for exploit chaining.VS CodeThe Cybersecurity Pulse covers a week of major security news, including GitHub’s poisoned VS Code extension incident, the latest DBIR findings, TeamPCP’s malicious durabletask PyPI compromise, and Cloudflare’s testing