
Webworm Adds EchoCreep and GraphWorm Backdoors Using Discord and Microsoft Graph API
Summary
ESET reports Webworm added EchoCreep and GraphWorm in 2025, using Discord and Microsoft Graph API for C2. The article describes their capabilities and the group’s custom proxies; initial access remains unknown.
Key points
- ESET reports that Webworm added EchoCreep and GraphWorm to its toolkit in 2025.
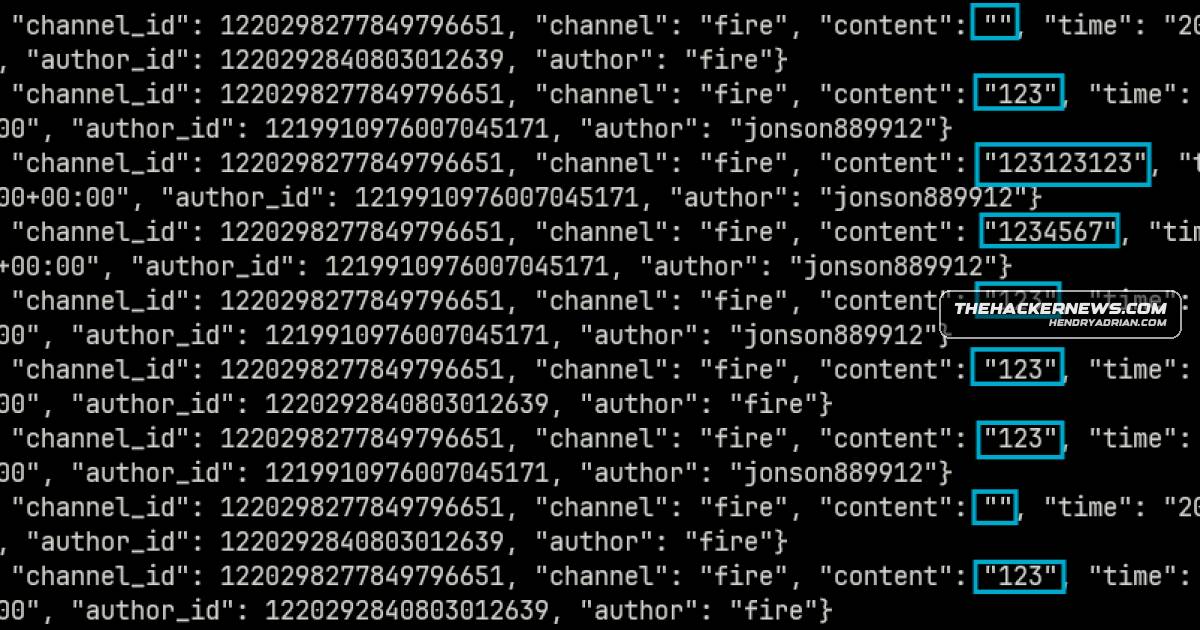
- EchoCreep uses Discord for C2 and supports command execution and file transfers; the article says 433 C2 messages were observed, with the earliest dating to March 21, 2024.
- GraphWorm uses Microsoft Graph API and can execute processes, transfer files through OneDrive, and stop execution on operator command.
- Webworm has used custom proxy tools and SoftEther VPN; WormFrp was found retrieving configurations from a compromised Amazon S3 bucket.
- The article says Webworm’s initial access method and delivery route for the backdoors are unknown.
- Separately, Cisco Talos describes BadIIS as a likely MaaS offering with tools for persistence and SEO fraud, including traffic redirection and content hijacking.
Article Details
- Event Type
- Webworm’s 2025 backdoor and proxy-tool expansion; separate reporting on a BadIIS malware-as-a-service offering.
- Impact
- EchoCreep uses Discord for C2 and supports command execution and file transfer; GraphWorm uses Microsoft Graph API and OneDrive and can execute processes and transfer files. Webworm targets government and enterprise organizations, including IT services, aerospace, and electric power. The article says its initial access method is unknown. Separately, BadIIS is described as likely sold or shared among multiple Chinese-speaking cybercrime groups, with capabilities for traffic redirection, reverse proxying, content hijacking, and SEO fraud.
People
Threat Actors
Aquatic PandaExplicitly identified in the article as an alternate name for FishMonger, a China-nexus cluster said to overlap with Webworm.FishMongerDescribed as a China-nexus cluster that overlaps with Webworm; the article explicitly identifies FishMonger as also known as Aquatic Panda.lwxatAlias of the BadIIS malware author, who is reported to have made supplementary deployment and persistence tools available for the BadIIS offering.SixLittleMonkeysDescribed as a China-nexus cluster that overlaps with Webworm; reported to deploy Gh0st RAT and Mikroceen against entities in Central Asia, Russia, Belarus, and Mongolia.Space PiratesIdentified as a China-nexus cluster that overlaps with Webworm; no further activity is detailed in the article.WebwormAssessed to have been active since at least 2022; reported targeting government and enterprise organizations and deploying EchoCreep, GraphWorm, and proxy tools. The article says Webworm overlaps with several China-nexus clusters.
Malware
9002 RATAttacks mounted by the group have leveraged remote access trojans (RATs) like Trochilus RAT, Gh0st RAT, and 9002 RAT (aka Hydraq and McRat).BadIISCisco Talos also reported a BadIIS MaaS offering with SEO fraud features.EchoCreepWebworm, a China-aligned threat actor active since at least 2022, has expanded its 2025 toolkit with EchoCreep and GraphWorm backdoors that use Discord and Microsoft Graph API for stealthy C2 communications.Gh0st RATAttacks mounted by the group have leveraged remote access trojans (RATs) like Trochilus RAT, Gh0st RAT, and 9002 RAT (aka Hydraq and McRat).GraphWormWebworm, a China-aligned threat actor active since at least 2022, has expanded its 2025 toolkit with EchoCreep and GraphWorm backdoors that use Discord and Microsoft Graph API for stealthy C2 communications.MikroceenSixLittleMonkeys is best known for deploying Gh0st RAT and a RAT called Mikroceen targeting entities in Central Asia, Russia, Belarus, and Mongolia.Trochilus RATAttacks mounted by the group have leveraged remote access trojans (RATs) like Trochilus RAT, Gh0st RAT, and 9002 RAT (aka Hydraq and McRat).
Vendors
Products
DiscordWebworm, a China-aligned threat actor active since at least 2022, has expanded its 2025 toolkit with EchoCreep and GraphWorm backdoors that use Discord and Microsoft Graph API for stealthy C2 communications.GitHubUnderlying these efforts is the use of a GitHub repository impersonating a WordPress fork (“github[.]com/anjsdgasdf/WordPress”) as a staging ground for malware and tools like SoftEther VPN in an effort to blend in andMicrosoft GraphWebworm, a China-aligned threat actor active since at least 2022, has expanded its 2025 toolkit with EchoCreep and GraphWorm backdoors that use Discord and Microsoft Graph API for stealthy C2 communications.Microsoft OneDriveGraphWorm uses Microsoft Graph API and can work with OneDrive.WordPressUnderlying these efforts is the use of a GitHub repository impersonating a WordPress fork (“github[.]com/anjsdgasdf/WordPress”) as a staging ground for malware and tools like SoftEther VPN in an effort to blend in and
Tools
ChainWormOther tools of note are iox and custom proxy solutions such as WormFrp, ChainWorm, SmuxProxy, and WormSocket.dirsearchThe group continues targeting government and enterprise victims across Asia and Europe while relying on custom proxies, SoftEther VPN, and shared tools like dirsearch and nuclei to hide activity and expand access.IOXOther tools of note are iox and custom proxy solutions such as WormFrp, ChainWorm, SmuxProxy, and WormSocket.NucleiThe group continues targeting government and enterprise victims across Asia and Europe while relying on custom proxies, SoftEther VPN, and shared tools like dirsearch and nuclei to hide activity and expand access.SmuxProxyOther tools of note are iox and custom proxy solutions such as WormFrp, ChainWorm, SmuxProxy, and WormSocket.SoftEther VPNThe group continues targeting government and enterprise victims across Asia and Europe while relying on custom proxies, SoftEther VPN, and shared tools like dirsearch and nuclei to hide activity and expand access.WormFrpOther tools of note are iox and custom proxy solutions such as WormFrp, ChainWorm, SmuxProxy, and WormSocket.WormSocketOther tools of note are iox and custom proxy solutions such as WormFrp, ChainWorm, SmuxProxy, and WormSocket.
Countries
BelarusSixLittleMonkeys is best known for deploying Gh0st RAT and a RAT called Mikroceen targeting entities in Central Asia, Russia, Belarus, and Mongolia.Belgiumproxies, while also increasingly focusing on European countries, including governmental organizations in Belgium, Italy, Serbia, Poland, and Spain, and a local university in South Africa.ChinaWebworm, a China-aligned threat actor active since at least 2022, has expanded its 2025 toolkit with EchoCreep and GraphWorm backdoors that use Discord and Microsoft Graph API for stealthy C2 communications.Georgiaagencies and enterprises spanning IT services, aerospace, and electric power sectors in Russia, Georgia, Mongolia, and several other Asian nations.Italywhile also increasingly focusing on European countries, including governmental organizations in Belgium, Italy, Serbia, Poland, and Spain, and a local university in South Africa.Mongoliaagencies and enterprises spanning IT services, aerospace, and electric power sectors in Russia, Georgia, Mongolia, and several other Asian nations.Polandfocusing on European countries, including governmental organizations in Belgium, Italy, Serbia, Poland, and Spain, and a local university in South Africa.Russiagovernment agencies and enterprises spanning IT services, aerospace, and electric power sectors in Russia, Georgia, Mongolia, and several other Asian nations.Serbiaalso increasingly focusing on European countries, including governmental organizations in Belgium, Italy, Serbia, Poland, and Spain, and a local university in South Africa.South Africagovernmental organizations in Belgium, Italy, Serbia, Poland, and Spain, and a local university in South Africa.Spainon European countries, including governmental organizations in Belgium, Italy, Serbia, Poland, and Spain, and a local university in South Africa.
Industries
Aerospaceto be active since at least 2022, targeting government agencies and enterprises spanning IT services, aerospace, and electric power sectors in Russia, Georgia, Mongolia, and several other Asian nations.Electric powerat least 2022, targeting government agencies and enterprises spanning IT services, aerospace, and electric power sectors in Russia, Georgia, Mongolia, and several other Asian nations.GovernmentThe group continues targeting government and enterprise victims across Asia and Europe while relying on custom proxies, SoftEther VPN, and shared tools like dirsearch and nuclei to hide activity and expand access.IT servicesis assessed to be active since at least 2022, targeting government agencies and enterprises spanning IT services, aerospace, and electric power sectors in Russia, Georgia, Mongolia, and several other Asian nations.