
GitHub Links Internal Repository Breach to Malicious Nx Console Extension
Summary
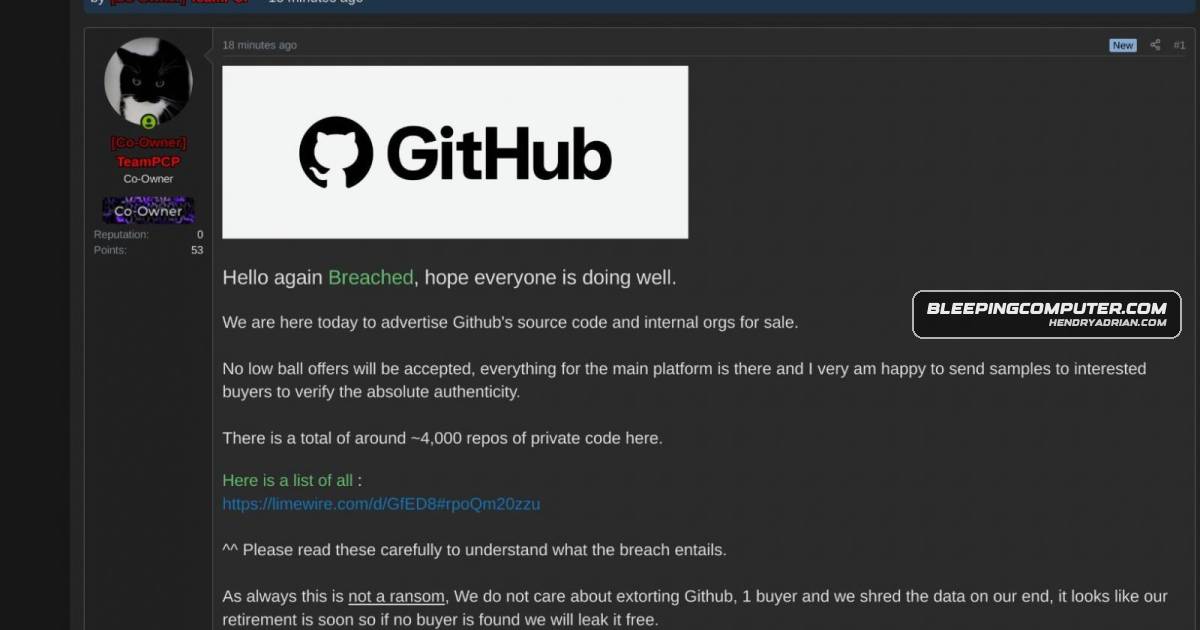
GitHub linked access to internal repositories to a malicious Nx Console extension distributed after a TanStack supply-chain compromise. TeamPCP separately claimed access to nearly 4,000 private repositories; GitHub said it found no evidence of customer data theft beyond
Key points
- GitHub said a developer's compromised device and a malicious version of the Nx Console VS Code extension were involved in the repository incident.
- The article links the attack's start to compromised TanStack and Mistral AI npm packages and the use of stolen CI/CD credentials.
- Nx Console version 18.95.0 was available on the Visual Studio Marketplace for about 18 minutes and on OpenVSX for about 36 minutes.
- TeamPCP claimed access to GitHub source code and nearly 4,000 private repositories, and reportedly sought at least $50,000; these are actor claims, not independent confirmation.
- GitHub said it secured the compromised device, rotated critical secrets, and was continuing to investigate and monitor for further activity.
- GitHub said it had found no evidence that customer data stored outside the affected repositories was stolen.
Article Details
- Victim Organization
- GitHub
- Victim Domain
- github.com
- Incident Type
- Supply-chain compromise leading to unauthorized access to GitHub internal repositories
- Data Types Exposed
- Source code and private repository data (TeamPCP claimed theft)
- CI/CD credentials and secrets
- Affected Records
- GitHub confirmed access to 3,800 internal repositories. TeamPCP separately claimed access to approximately 4,000 private repositories.
- Affected Data Size
- Not disclosed
- Operational Impact
- GitHub secured the compromised device, rotated critical secrets, and continued investigating and monitoring for follow-on activity. GitHub said it had found no evidence that customer data stored outside the affected repositories was stolen.
- Ransom Or Extortion
- TeamPCP claimed it had stolen GitHub source code and private repositories and reportedly asked for at least $50,000 for the data. The theft claim was not confirmed by GitHub.
- Claim Status
- confirmed
MITRE ATT&CK
People
Threat Actors
Vendors
GitHubGitHub confirmed that attackers accessed 3,800 internal repositories through a malicious Nx Console VS Code extension tied to the TanStack npm supply-chain attack.Microsoftdevs revealed on Monday that they were jointly investigating the impact of the attack with GitHub and Microsoft, after a malicious version of Nx Console 18.95.0 was available on the Visual Studio Marketplace forMistral AIThe attack began with the compromise of TanStack and Mistral AI npm packages.NxGitHub confirmed that attackers accessed 3,800 internal repositories through a malicious Nx Console VS Code extension tied to the TanStack npm supply-chain attack.TanStackGitHub confirmed that attackers accessed 3,800 internal repositories through a malicious Nx Console VS Code extension tied to the TanStack npm supply-chain attack.
Products
GitHubGitHub confirmed that attackers accessed 3,800 internal repositories through a malicious Nx Console VS Code extension tied to the TanStack npm supply-chain attack.npmGitHub confirmed that attackers accessed 3,800 internal repositories through a malicious Nx Console VS Code extension tied to the TanStack npm supply-chain attack.Nx ConsoleGitHub confirmed that attackers accessed 3,800 internal repositories through a malicious Nx Console VS Code extension tied to the TanStack npm supply-chain attack.OpenVSXof Nx Console 18.95.0 was available on the Visual Studio Marketplace for approximately 18 minutes and on OpenVSX for another 36 minutes.VSCodeand telling BleepingComputer that the incident resulted from an employee installing a malicious Visual Studio Code (VS Code) extension, without disclosing the extension’s name.