
Cybersecurity Roundup: 47 Zero-Days, Cloud Intrusions and AI-Driven Attacks
Summary
This week's roundup covers 47 zero-days demonstrated at Pwn2Own Berlin, a Composer token-leak fix, evolving OrBit rootkits, Storm-2949 cloud-data theft, AI-assisted intrusions in Latin America, and new malware and fraud campaigns.
Key points
- Researchers exploited 47 zero-day flaws across products from Windows, Linux, VMware and NVIDIA at Pwn2Own Berlin 2026.
- Composer fixed CVE-2026-45793, which could expose GitHub tokens in GitHub Actions logs; users were advised to update or disable affected workflows until patched.
- Intezer identified two OrBit rootkit lineages, including newer auditd-evasion hooks and a service-side PAM impersonation capability.
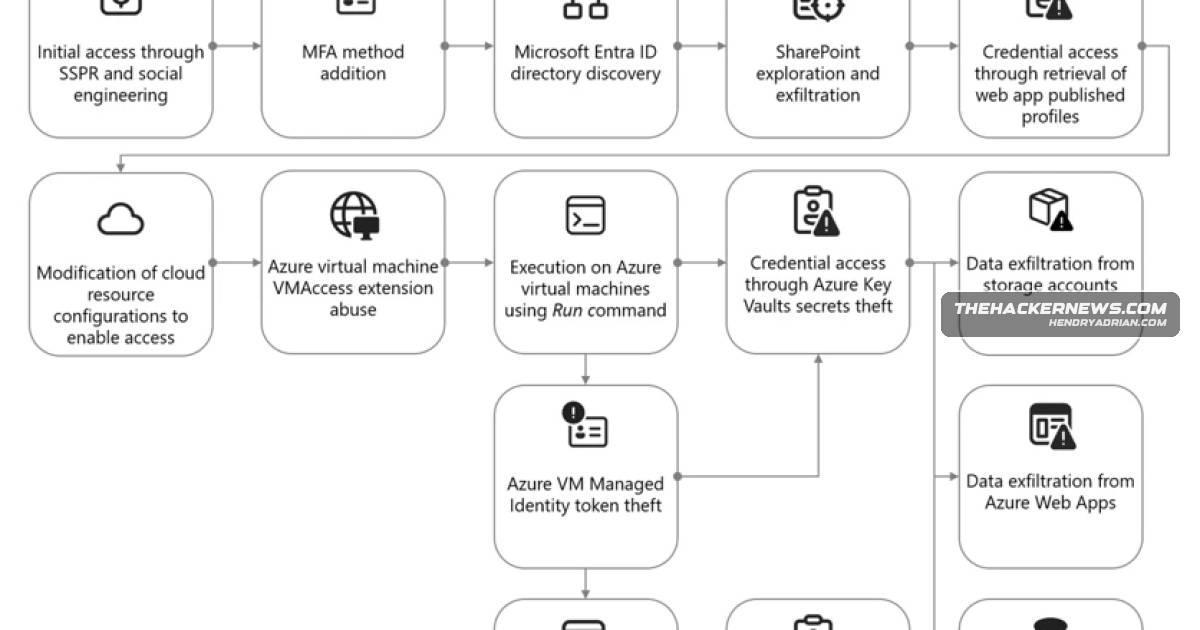
- Microsoft reported that Storm-2949 used social engineering involving SSPR and MFA, plus legitimate Azure features, to access and exfiltrate data from cloud environments.
- Trend Micro described two AI-assisted intrusion campaigns in Latin America; SHADOW-AETHER-040 compromised six Mexican government entities, while a separate attempted breach of a water utility's OT environment was unsuccessful.
- S2W said Gunra ransomware had targeted five South Korean companies since its discovery; the group has claimed 32 victims as of March 2026.
- A public repository containing CISA contractor credentials and internal-system secrets was taken offline after disclosure; the article says there is no evidence the exposed data was compromised.
Article Details
- Event Type
- Weekly cybersecurity news roundup covering zero-day flaws, data exposure, ransomware, malicious software, and cybercrime.
- Impact
- The roundup reports 47 zero-day flaws exploited during Pwn2Own Berlin 2026. Other reported impacts include Composer token exposure in GitHub Actions logs; sensitive data exfiltration in a Storm-2949 attack; six Mexican government entities compromised by SHADOW-AETHER-040; and a failed attempt to breach a municipal water utility’s operational technology environment. A Huawei router zero-day reportedly caused a nationwide telecommunications outage in Luxembourg lasting more than three hours. Additional reports describe ransomware targeting South Korean companies and malware campaigns affecting users and organizations.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | dnslog-cdn-images[.]freemyip[.]com | Attacker-controlled dynamic DNS subdomain used as a DNS TXT command-and-control channel by the malicious Go module. |
| DOMAIN | v3[.]jiathis[.]com | External domain serving a multi-stage malicious payload linked to compromised versions of the art-template npm package. |
MITRE ATT&CK
T1021.004 · SSHThe SHADOW-AETHER campaigns used SSH to access victim internal network environments.T1027.003 · SteganographyThe PawsRunner loader retrieves encrypted payload data hidden in an image using steganography.T1056.001 · KeyloggingBanana RAT includes keylogging capabilities.T1059.001 · PowerShellBanana RAT is described as a PowerShell-only client, and reported MSHTA delivery chains also involve PowerShell.T1059.007 · JavaScriptThe invoice-themed campaign executes JavaScript as part of its loader chain.T1071.004 · DNSThe malicious Go module polls DNS TXT records for its command-and-control channel.T1105 · Ingress Tool TransferThe PawsRunner loader retrieves a final payload, and the art-template compromise loads external JavaScript.T1113 · Screen CaptureBanana RAT supports screen streaming.T1218.005 · MshtaAttackers abuse Microsoft HTML Application Host (MSHTA) in malware delivery chains.T1562.001 · Disable or Modify ToolsStorm-2949 reportedly attempted to disable Microsoft Defender Antivirus protections.T1566.002 · Spearphishing LinkThe CypherLoc scareware attack directs victims from phishing emails to malicious web pages.T1572 · Protocol TunnelingThe SHADOW-AETHER campaigns established traffic tunnels to victim systems for access to internal networks.T1656 · ImpersonationThreat actors have impersonated Signal support to take control of victims’ accounts.
CVE
CVE-2026-45793Vendor / Product unavailableThe vulnerability has been assigned the CVE identifier CVE-2026-45793 (CVSS score: 7.5).CVE-2026-8631Hp · Linux imaging and printingHP has released fixes for CVE-2026-8631 (CVSS score: 9.3), a critical heap-based buffer overflow vulnerability in HPLIP that could allow escalation of privileges and/or arbitrary code execution.
People
Eric ParkerYouTuber who documented the discovery of the malicious Steam game Beyond The Dark.Kush PandyaResearcher quoted describing the malicious Go module’s DNS TXT command-and-control behavior.Mohamed Lemine Ahmed JidouSecurity researcher who discovered the HPLIP heap-based buffer overflow vulnerability.Nicole FishbeinResearcher quoted describing newly identified OrBit rootkit lineages and their capabilities.Tom KellermannTrendAI vice president of AI Security and Threat Research who commented on the risks posed by Brazilian cybercrime and banking malware.
Threat Actors
BLOCKADE SPIDERThe article says OrBit has been used by this cybercrime group in Embargo ransomware campaigns.CL-CRI-1089Unit 42 attributed distribution of trojanized applications to this cluster; it appears to target credentials and deploy adware and proxy-style payloads.CL-UNK-1090Unit 42 identified this cluster as distributing trojanized applications; its motivation is unknown.CL-UNK-1110Unit 42 identified this cluster as distributing trojanized applications; its motivation is unknown.GunraThe article describes a group using Gunra ransomware, operating a RaaS model, and claiming 32 victims as of March 2026.SandwormNozomi Networks reported identifying 29 events as Sandworm activity and 17 infected machines in its dataset.SHADOW-AETHER-064Described as a Portuguese-speaking hacking crew linked to a campaign targeting financial organizations in Brazil.Storm-2949Microsoft attributed an attack involving social engineering, cloud access, and data exfiltration to Storm-2949.
Malware
Banana RATA new Brazilian banking trojan dubbed Banana RAT has become the latest malware to target financial institutions in the region.CorunaThe final payload is the Coruna exploit kit.”EmbargoPAM impersonation primitive.” OrBit has been put to use by Blockade Spider, a cybercrime group running Embargo ransomware campaigns.EvilAIidentified 4,000 samples across 100 unique variants associated with a threat known as TamperedChef (aka EvilAI), which involves using trojanized versions of productivity software to deliver malicious payloads usingGunraFrom Pwn2Own Berlin 2026 zero-days and Composer token leakage to Storm-2949 cloud abuse, Gunra ransomware, OrBit rootkit activity, and AI-driven intrusions, the pattern is faster, stealthier, and built around normalMedusaIt’s assessed that OrBit is a fork of an open-source rootkit called Medusa, which first publicly surfaced in December 2022.OrBitFrom Pwn2Own Berlin 2026 zero-days and Composer token leakage to Storm-2949 cloud abuse, Gunra ransomware, OrBit rootkit activity, and AI-driven intrusions, the pattern is faster, stealthier, and built around normalPawsRunnerwhich employs environment variables to hide malicious commands and uses a steganographic loader dubbed PawsRunner to deploy the PureLogs infostealer malware.PureLogs Stealervariables to hide malicious commands and uses a steganographic loader dubbed PawsRunner to deploy the PureLogs infostealer malware.TamperedChef42 said it has identified 4,000 samples across 100 unique variants associated with a threat known as TamperedChef (aka EvilAI), which involves using trojanized versions of productivity software to deliver malicious
Vendors
AnthropicMexican government organizations between December 2025 and February 2026 by an unknown adversary using Anthropic’s Claude and OpenAI’s GPT AI models to carry out the intrusion activities.AppleApple said its App Store stopped over $2.2 billion in potentially fraudulent transactions and rejected over 2 million problematic app submissions in 2025.Cloudflarebroadly – including outside the program – for maximum defensive impact.” The development comes as Cloudflare said Mythos is a “real step forward” and is capable of chaining “small attack primitives together intoDiscordDiscord has announced that all voice and video calls through the communication platform are now protected by default with end-to-end encryption (E2EE).GitHubComposer fixed a token leak vulnerability affecting GitHub Actions logs.HPHP has released fixes for CVE-2026-8631 (CVSS score: 9.3), a critical heap-based buffer overflow vulnerability in HPLIP that could allow escalation of privileges and/or arbitrary code execution.HuaweiThe exploitation of a zero-day vulnerability in Huawei enterprise router software led to a nationwide telecom outage in Luxembourg on July 23, 2025, The Record reported this week.MicrosoftStorm-2949 abused Microsoft SSPR and Azure features to steal sensitive data.OpenAIbetween December 2025 and February 2026 by an unknown adversary using Anthropic’s Claude and OpenAI’s GPT AI models to carry out the intrusion activities.ValveA malicious game distributed through Steam has been removed from Valve after it was observed profiling players’ systems and communicating with external infrastructure that allows it to deploy secondary payloads.
Products
AWS GovCloudand Infrastructure Security Agency (CISA) maintained credentials to several highly privileged AWS GovCloud accounts and a large number of internal CISA systems exposed on a public GitHub repository (ironicallyAzureStorm-2949 abused Microsoft SSPR and Azure features to steal sensitive data.Beyond The DarkThe game, titled Beyond The Dark, masqueraded as a free indie horror title on Steam.Claude#Pwn2OwnBerlin2026ComposerFrom Pwn2Own Berlin 2026 zero-days and Composer token leakage to Storm-2949 cloud abuse, Gunra ransomware, OrBit rootkit activity, and AI-driven intrusions, the pattern is faster, stealthier, and built around normalDiscordDiscord has announced that all voice and video calls through the communication platform are now protected by default with end-to-end encryption (E2EE).Entra IDIt harbored 844 MB of plain-text passwords, AWS tokens, and Entra ID SAML certificates belonging to the agency.GitHub ActionsComposer fixed a token leak vulnerability affecting GitHub Actions logs.GPT#Pwn2OwnBerlin2026HPLIPHP has released fixes for CVE-2026-8631 (CVSS score: 9.3), a critical heap-based buffer overflow vulnerability in HPLIP that could allow escalation of privileges and/or arbitrary code execution.Microsoft 365 Apps for Enterpriseinto completing multi-factor authentication (MFA) prompts, led to the exfiltration of data from Microsoft 365 applications, file-hosting services, and Azure-hosted production environments.Microsoft Defender Antimalware PlatformThe attacker is also said to have conducted discovery activities, installed ScreenConnect, and attempted to disable Microsoft Defender Antivirus protections.Microsoft EdgeDEVCORE won the event with 50.5 Master of Pwn points and $505,000 in rewards throughout the three-day contest after hacking Microsoft SharePoint, Microsoft Exchange, Microsoft Edge, and Windows 11.Microsoft ExchangeDEVCORE won the event with 50.5 Master of Pwn points and $505,000 in rewards throughout the three-day contest after hacking Microsoft SharePoint, Microsoft Exchange, Microsoft Edge, and Windows 11.Microsoft SharePointDEVCORE won the event with 50.5 Master of Pwn points and $505,000 in rewards throughout the three-day contest after hacking Microsoft SharePoint, Microsoft Exchange, Microsoft Edge, and Windows 11.mSzyfrCybersecurity System” to stop using Signal, instead directing them to use an encrypted messenger called mSzyfr developed by a leading Polish research organization, citing social engineering attacks orchestrated byMythosMythos intel sharing expandsScreenConnectThe attacker is also said to have conducted discovery activities, installed ScreenConnect, and attempted to disable Microsoft Defender Antivirus protections.SignalSignal alternative pushedSteamA malicious game distributed through Steam has been removed from Valve after it was observed profiling players’ systems and communicating with external infrastructure that allows it to deploy secondary payloads.TelegramTelegram accounts hijackedWindows 11DEVCORE won the event with 50.5 Master of Pwn points and $505,000 in rewards throughout the three-day contest after hacking Microsoft SharePoint, Microsoft Exchange, Microsoft Edge, and Windows 11.
Tools
Countries
BrazilThe second campaign, linked to a Portuguese-speaking hacking crew named SHADOW-AETHER-064, has been active since April and has singled out financial organizations in Brazil.Chinato us that we probably do know about.’” While Trump did not elaborate on the attacks carried out against China, the acknowledgement comes as China has been accused of conducting sweeping intrusions into U.S.Croatiaconducting carrier billing fraud through premium SMS abuse across Malaysia, Thailand, Romania, and Croatia between March 2025 and January 2026.LuxembourgThe exploitation of a zero-day vulnerability in Huawei enterprise router software led to a nationwide telecom outage in Luxembourg on July 23, 2025, The Record reported this week.MalaysiaPremium Deception has been observed conducting carrier billing fraud through premium SMS abuse across Malaysia, Thailand, Romania, and Croatia between March 2025 and January 2026.MexicoUndertaken by a Spanish-speaking threat actor, SHADOW-AETHER-040 has compromised six government entities in Mexico between December 27, 2025, and January 4, 2026.Romaniahas been observed conducting carrier billing fraud through premium SMS abuse across Malaysia, Thailand, Romania, and Croatia between March 2025 and January 2026.ThailandDeception has been observed conducting carrier billing fraud through premium SMS abuse across Malaysia, Thailand, Romania, and Croatia between March 2025 and January 2026.United StatesWell, we do it too,” Trump said during his return flight to the U.S.
Industries
Critical infrastructureas the primary technical executor and independently identified the OT environment’s relevance to critical infrastructure, assessed its potential as a crown jewel asset, and investigated possible access pathways toGovernmentThe Polish government is urging public officials and “entities within the National Cybersecurity System” to stop using Signal, instead directing them to use an encrypted messenger called mSzyfr developed by a leading