
Play ransomware group claims it targeted NL Fisher
Summary
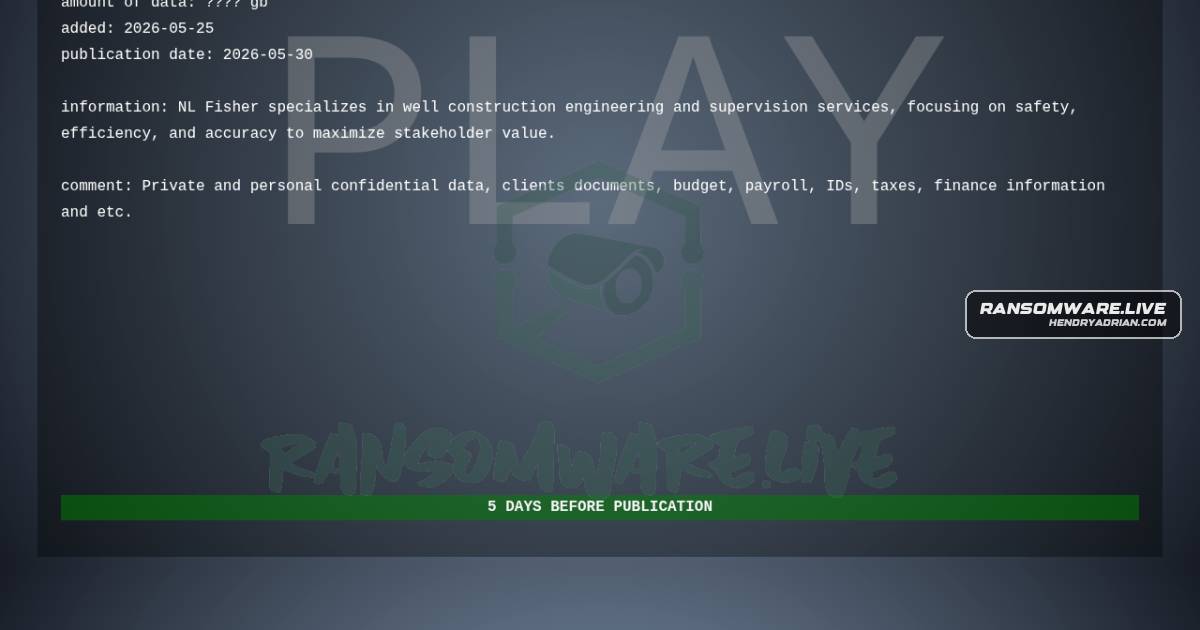
Ransomware[.]live monitored an unverified Play ransomware-group claim that it targeted NL Fisher, a Netherlands-based agriculture and food production organization, with alleged data encryption and operational disruption.
Key points
- The post attributes the claim to the Play ransomware group and names NL Fisher as the victim.
- The group allegedly targeted NL Fisher to encrypt data and disrupt operations; the post does not independently confirm those outcomes.
- A Play leak-site source is listed, and ransomware[.]live is identified as the monitoring service.
- The post says the claim's accuracy is unconfirmed and offers to share an official statement from NL Fisher.
Article Details
- Victim
- NL Fisher
- Claim Date
- 2026-05-25
- Encryption Status
- Unconfirmed; the source says play targeted systems to encrypt data but does not confirm encryption.
- Exfiltration Status
- Unknown
- Leak Status
- Unknown; no leak or data publication is reported.